
Prerequisites: Firewall Fundamentals, TCP/IP, SSH, VPN and Basic User Authentication
Imagine your organization has several network administrators.
One administrator manages firewall rules.
Another is responsible only for monitoring and troubleshooting.
A third manages remote-access VPN users.
Should every administrator have the same firewall privileges?
And how can the organization determine who logged into the firewall, which commands they executed and whether they were authorized to make changes?
These are the types of problems addressed by AAA — Authentication, Authorization and Accounting.
Cisco Secure Firewall ASA uses AAA services to control different kinds of access, including administrative sessions, supported network access and remote-access VPN connections.
AAA can use locally configured users or supported external identity servers.
In this article, you will learn:
- What AAA means in Cisco ASA
- How Authentication, Authorization and Accounting differ
- How local and centralized identity services work
- When to use RADIUS, TACACS+ and LDAP
- How AAA applies to SSH, ASDM and VPN
- How command authorization works
- What accounting does and does not record
- Why redundancy, MFA and least privilege matter
- How to design an effective AAA policy
What Is AAA in Cisco ASA?
AAA is a security framework used to verify identities, enforce access permissions and record supported activity.
The three components are related but perform different functions.
1. Authentication — Who Are You?
Authentication verifies the claimed identity of a user or device.
Examples:
- An administrator logging into ASA through SSH
- A user connecting through Cisco Secure Client VPN
- An administrator signing into ASDM
The ASA can use local credentials or supported remote identity services.
2. Authorization — What Can You Do?
Authorization determines the actions or resources a successfully authenticated user may access.
Examples:
- Allowing one administrator to inspect firewall configuration
- Permitting another administrator to execute approved configuration commands
- Restricting a VPN user to selected internal applications
3. Accounting — What Activity Is Recorded?
Accounting produces records of supported access or actions.
Examples:
- Administrative session start and stop information
- Selected CLI commands
- VPN session accounting
- Connection usage information provided by the applicable service

Understanding AAA Architecture
Cisco ASA supports both local and external AAA methods.
Local Authentication
The local user database is stored on the ASA.
This can be useful for:
- Small administrative environments
- Emergency management access
- Lab deployments
- Approved fallback authentication
External Authentication
External identity services allow organizations to maintain user information outside the firewall.
Cisco ASA supports services such as:
- RADIUS
- TACACS+
- LDAP
Available functions and authentication methods differ by protocol.
Example AAA Network
| Component | Example Address | Purpose |
|---|---|---|
| Cisco ASA | 192.168.100.1 | Firewall and AAA client |
| Administrator PC | 192.168.100.20 | SSH or ASDM access |
| RADIUS Server | 192.168.100.10 | Central authentication for supported services |
| TACACS+ Server | 192.168.100.11 | Administrative authorization and accounting |
| Directory Server | 192.168.100.12 | External user directory |
These are example private IPv4 addresses.
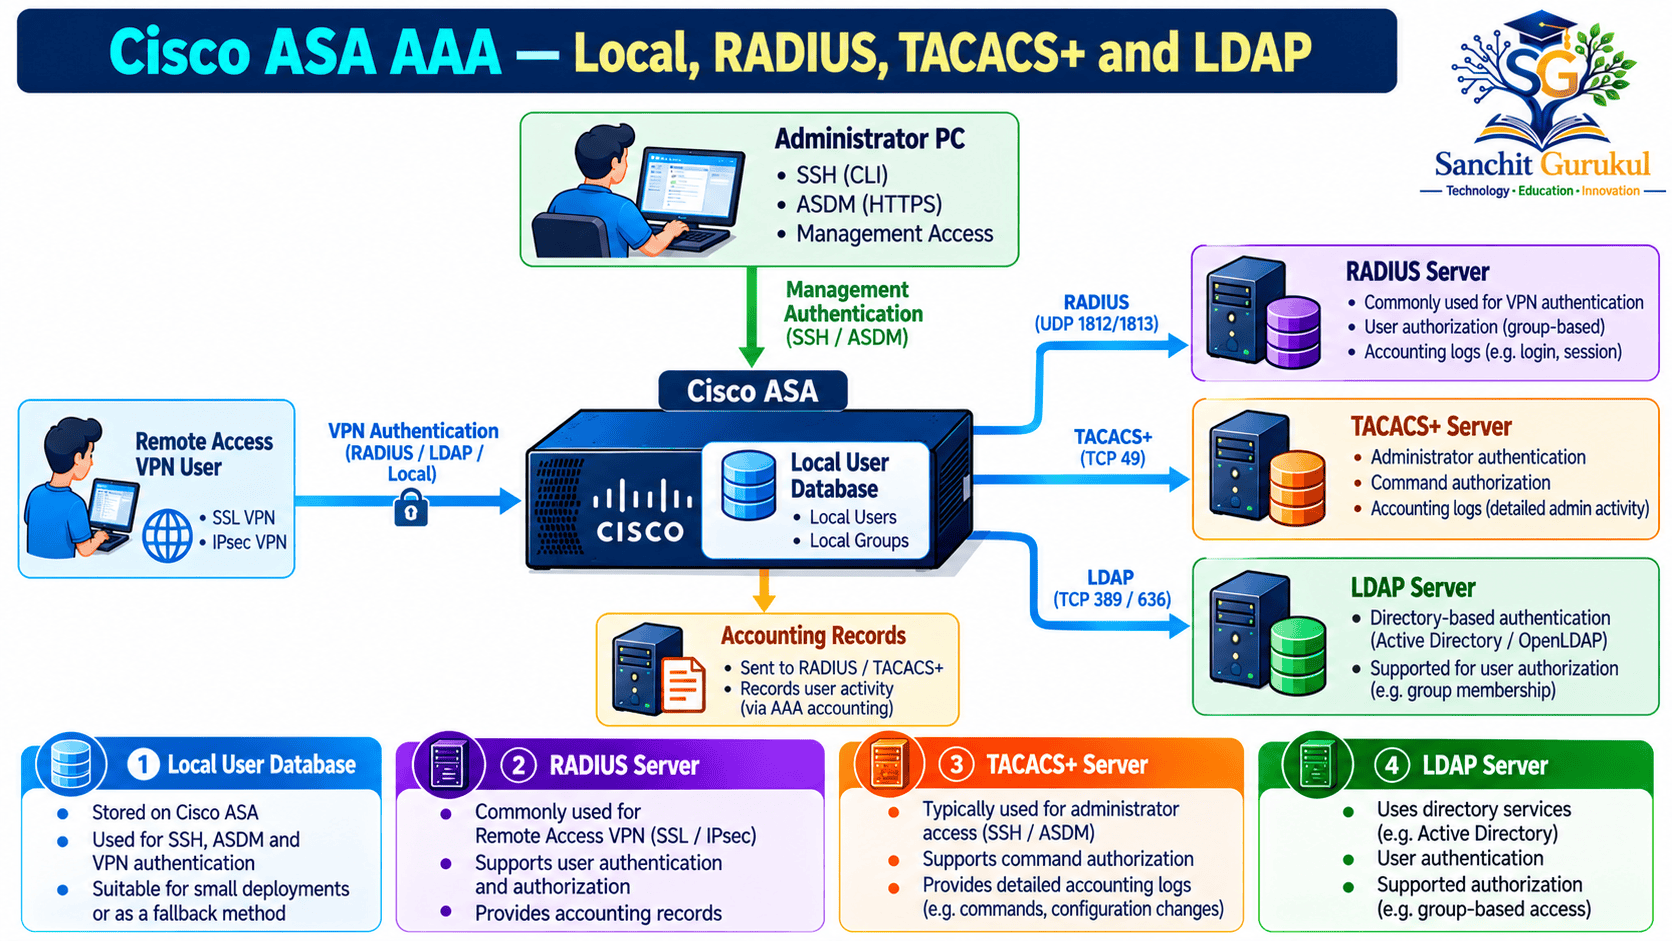
RADIUS vs TACACS+ vs LDAP
The protocols serve overlapping but different purposes.
| Feature | RADIUS | TACACS+ | LDAP |
|---|---|---|---|
| Common ASA use | VPN and network access | Network-device administration | Directory authentication and attributes |
| Authentication | Yes | Yes | Yes |
| Authorization | Supported through attributes | Fine-grained command authorization | Supported directory attribute mapping |
| Accounting | Supported session accounting | Supported session and command accounting | Not the ASA’s command-accounting transport |
| Typical transport | UDP | TCP | TCP/TLS depending on configuration |
| Typical deployment | VPN identity and policy | Administrator access control | Enterprise directory integration |
When to Use RADIUS
RADIUS is commonly selected for:
- Remote Access VPN
- Centralized user authentication
- Authentication integration with Cisco ISE or other supported systems
- Session accounting
- Supported authorization attributes
When to Use TACACS+
TACACS+ is commonly selected for:
- Network-administrator authentication
- Command-by-command authorization
- Administrator command accounting
- Centralized access control to infrastructure devices
When to Use LDAP
LDAP can provide authentication against a directory and supported user attribute retrieval or mapping.
It is not interchangeable with TACACS+ command accounting.
Where Can AAA Be Used in Cisco ASA?
AAA is not limited to VPN users.
1. SSH Administration
An administrator opens an SSH session to the ASA.
AAA can authenticate the administrator through local or remote methods.
Supported command authorization can control what the user may execute.
2. ASDM Administration
ASDM uses HTTPS-based management access.
AAA can authenticate authorized administrators.
3. Remote Access VPN
AAA can verify users connecting through compatible remote-access VPN services.
It can also supply applicable authorization information and supported session accounting.
4. Network Access
Cisco ASA supports certain AAA-based network authentication and authorization mechanisms.
The exact capabilities depend on the deployed feature.
5. Console and Privileged Access
AAA can control supported console and enable-level authentication.
How Command Authorization Works
Command authorization determines which CLI commands an administrator is allowed to execute.
Cisco ASA provides two main approaches.
Local Privilege-Level Authorization
The ASA uses locally defined command privilege levels.
A user with a particular level can access the commands permitted at that level under the configured authorization rules.
TACACS+ Command Authorization
The ASA sends the relevant command and identity information to a TACACS+ server for authorization.
The server can return an approval or denial according to centrally configured policy.
Example Roles
| Administrator Role | Intended Permission |
|---|---|
| Viewer | Review supported configuration and status |
| Operator | Run selected operational commands |
| Firewall Administrator | Make approved firewall configuration changes |
| Senior Administrator | Perform broader authorized maintenance |
Actual ASA privileges and TACACS+ policy must be designed explicitly.
A role name alone does not create command restrictions.

Understanding AAA Accounting
Accounting supports monitoring and audit processes.
It can record supported events such as:
- Administrative session activity
- Privileged access activity
- Selected commands
- VPN session start and stop information
- Usage-related data provided by the relevant service
Command Accounting
Cisco ASA supports TACACS+ command accounting.
This does not mean every possible command is recorded.
Cisco documents that command accounting does not include ordinary show commands.
If a minimum privilege level is configured, commands below that threshold are excluded.
Session Accounting
RADIUS and TACACS+ can support appropriate accounting functions.
For Remote Access VPN, RADIUS accounting can record information about user session activity.
AAA Server Redundancy and Local Fallback
An external AAA server introduces a dependency.
If the server becomes unreachable, administrators or VPN users may be unable to authenticate.
Use Server Groups
Configure appropriate multiple servers in a server group where supported.
Plan Emergency Access
Maintain documented recovery access for approved administrators.
Understand LOCAL Fallback
Cisco ASA can use a local database fallback for certain management authentication methods when the configured server group is unavailable.
However:
A rejected username or password from an available AAA server does not mean the ASA should automatically try the local account.
This distinction prevents fallback from becoming an unintended authentication bypass.
AAA Security Best Practices
Use Centralized Identity Management Where Appropriate
External AAA systems help organizations maintain consistent administrator and VPN identity policies.
Apply Least Privilege
Grant only the commands and resources each user requires.
Protect AAA Communication
Use trusted management networks, suitable protocol security, and supported transport protections.
Implement MFA
Use a supported MFA-enabled identity service or authentication integration where required.
Maintain Redundancy
Avoid relying on one authentication server when availability is important.
Protect Emergency Credentials
Store recovery credentials securely and review their use.
Enable Appropriate Accounting
Record relevant administrative and VPN session activity.
Review Authorization Regularly
Remove unnecessary user permissions and stale accounts.
Verify Context-Specific AAA
In ASA Multiple Context Mode, AAA configuration can differ between contexts.
The system execution space does not support the ordinary AAA command configuration used inside security contexts.
Benefits and Trade-Offs
| Benefit | Trade-Off |
|---|---|
| Centralized identity management | External-server availability dependency |
| Better access control | Additional configuration complexity |
| Command-level restrictions | Risk of administrator lockout |
| Useful audit information | Accounting coverage limitations |
| Scalable user administration | Licensing and infrastructure costs |
| MFA integration | Identity-service compatibility requirements |
Key Takeaways
- AAA stands for Authentication, Authorization and Accounting.
- Authentication verifies identity.
- Authorization enforces permitted actions and resources.
- Accounting records supported session and command activity.
- Local authentication and external AAA can be used for different purposes.
- RADIUS is commonly used for Remote Access VPN.
- TACACS+ supports administrator command authorization and command accounting.
- LDAP supports directory-related identity functions.
- Accounting does not automatically record every command.
- Server redundancy and recovery access are important.
Conclusion
AAA is an important part of secure Cisco ASA administration.
It helps organizations authenticate administrators and VPN users, control permitted actions and maintain appropriate records of access.
However, AAA is not one configuration switch.
Local users, RADIUS, TACACS+, LDAP, command authorization and accounting serve different purposes and must be configured for the intended use case.
The most reliable deployments combine centralized identity services with carefully designed permissions, monitoring, redundancy and emergency recovery access.
A strong AAA design protects both the firewall itself and the services managed through it.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


