
Prerequisites: Basic TCP/IP Networking, Firewall Fundamentals, HTTPS and Cisco ASA CLI Basics
Imagine you have joined a network security team responsible for maintaining a Cisco ASA firewall.
One morning, your manager asks you to review the firewall rules, investigate a blocked connection and verify whether an existing VPN tunnel is operational.
You could use the ASA command-line interface to perform these tasks.
But what if you could view the configuration, manage security rules and inspect traffic through a graphical interface?
That is where Cisco Adaptive Security Device Manager (ASDM) becomes useful.
ASDM provides a graphical management application for supported Cisco ASA firewalls.
Instead of remembering every configuration command, administrators can use menus, configuration screens, wizards and monitoring tools to perform many routine operations.
However, understanding how ASDM connects to the firewall, what it can manage and where its limitations begin is important.
In this article, you will learn:
- What Cisco ASDM is and how it works
- How ASDM differs from the ASA CLI
- Which management features ASDM provides
- How to prepare an ASA for ASDM access
- How to install and launch ASDM
- How to configure secure administrator authentication
- How to verify ASDM access using CLI commands
- How to troubleshoot common connection problems
- What advantages, limitations and best practices administrators should know
What Is Cisco ASDM?
Cisco Adaptive Security Device Manager (ASDM) is a graphical management application used to configure, monitor and troubleshoot supported Cisco Adaptive Security Appliance (ASA) firewalls.
ASDM allows administrators to perform many tasks that would otherwise require CLI commands.
Examples include:
- Managing firewall interfaces
- Creating Access Control Lists (ACLs)
- Configuring Network Address Translation (NAT)
- Managing supported VPN configurations
- Reviewing logging settings
- Monitoring interfaces and connections
- Running packet-tracing diagnostics
- Backing up supported configurations
ASDM connects to the ASA using HTTPS.
The administrator initially accesses an HTTPS launch page hosted by the firewall and then launches the ASDM management application.
How ASDM Works
The ASA runs the firewall software and maintains the active device configuration.
ASDM provides the graphical administrative interface for that ASA.
When an administrator applies a supported configuration change in ASDM, the application communicates with the ASA to make the change.

Cisco ASDM vs ASA CLI
ASDM and the CLI manage the same underlying ASA device, but they provide different administrative experiences.
| Feature | Cisco ASDM | ASA CLI |
|---|---|---|
| Interface | Graphical | Command-line |
| Configuration | Forms, menus and wizards | Commands |
| Learning experience | Helpful for visual workflows | Requires command knowledge |
| Monitoring | Graphs, dashboards and views | Command output and counters |
| Troubleshooting | Packet Tracer and graphical tools | Packet-tracer, show and debug commands |
| Automation | Limited compared with programmatic methods | Better suited to command-based workflows |
| Advanced operations | Depends on available GUI support | May provide additional control |
When ASDM Is Useful
ASDM can be especially helpful when:
- Reviewing existing security rules
- Examining NAT configurations
- Configuring supported VPN features
- Monitoring interface statistics
- Troubleshooting connectivity
- Performing occasional administrative changes
When CLI Is Preferable
The CLI is often more practical for:
- Rapid diagnostics
- Collecting detailed command output
- Repeated administrative operations
- Troubleshooting when ASDM is unavailable
- Working with features not exposed by the selected ASDM version
Key Features of Cisco ASDM
1. Firewall Policy Management
ASDM provides graphical tools for creating and modifying Access Control Lists and related security configurations.
Administrators can review source networks, destination networks, services and permitted or denied traffic.
2. Network Address Translation
ASDM supports configuring NAT rules used to translate source or destination addresses.
This includes common outbound translation and supported server-publication scenarios.
3. VPN Configuration
ASDM includes configuration workflows and wizards for supported VPN features.
Available VPN functions depend on the ASA software, licenses and platform.
4. Logging and Monitoring
Administrators can examine ASA logging information, interface statistics, connections and other supported monitoring data.
5. Troubleshooting Tools
ASDM provides integrated tools such as:
- Packet Tracer
- Packet Capture
- Logging views
- Interface statistics
- Connection information
6. Configuration Management
ASDM provides options to manage configuration changes and perform supported backup and restore operations.
Requirements Before Installing Cisco ASDM
Before configuring ASDM access, verify the ASA platform and management workstation requirements.
ASA Requirements
- Supported Cisco ASA software
- Compatible ASDM image
- Appropriate ASA licensing
- Reachable management interface
- HTTPS management access
- Authorized administrator credentials
Administrator Workstation Requirements
- Supported operating system
- Compatible ASDM Launcher
- Required Java environment for the selected ASDM package
- Network connectivity to the ASA management address
- Appropriate administrative permissions
ASDM 7.24 Java Requirements
Cisco documents different ASDM packages.
| ASDM Package | Java Requirement |
|---|---|
| Oracle JDK-based ASDM 7.24 | Compatible Oracle JDK 11 |
| OpenJRE ASDM 7.24 | OpenJRE 11 included with the package |
| OpenJRE ARM64 ASDM 7.24 | Platform-specific bundled OpenJRE for supported ARM64 environments |
Earlier ASDM releases can require different Java versions.
Example ASDM Management Network
Consider the following lab.
| Component | IP Address / Network | Purpose |
|---|---|---|
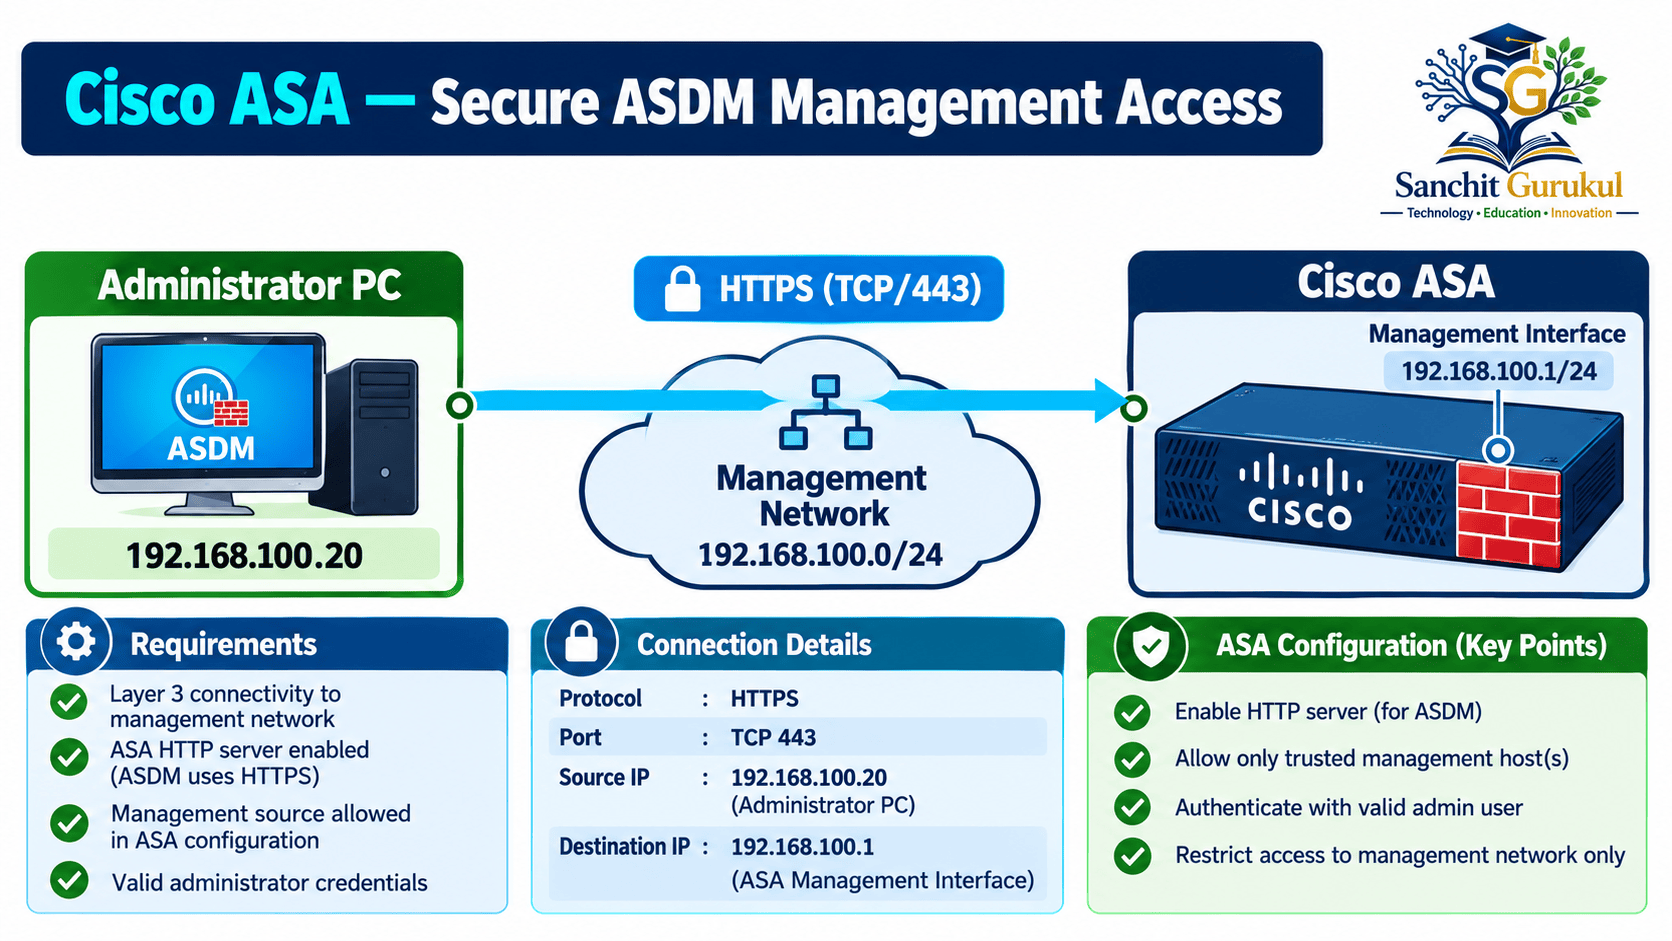
| Cisco ASA Management Interface | 192.168.100.1/24 | HTTPS management |
| Administrator Workstation | 192.168.100.20/24 | ASDM client |
| Internal LAN | 192.168.10.0/24 | Protected network |
| External Network | Deployment-specific | Upstream connectivity |
The lab assumes that the ASA already has a configured and operational interface named management.
The command examples below apply to the ASA CLI in a suitable single-context deployment.
Actual interface names may differ by hardware and software configuration.
Step 1 — Verify the ASDM Image on Cisco ASA
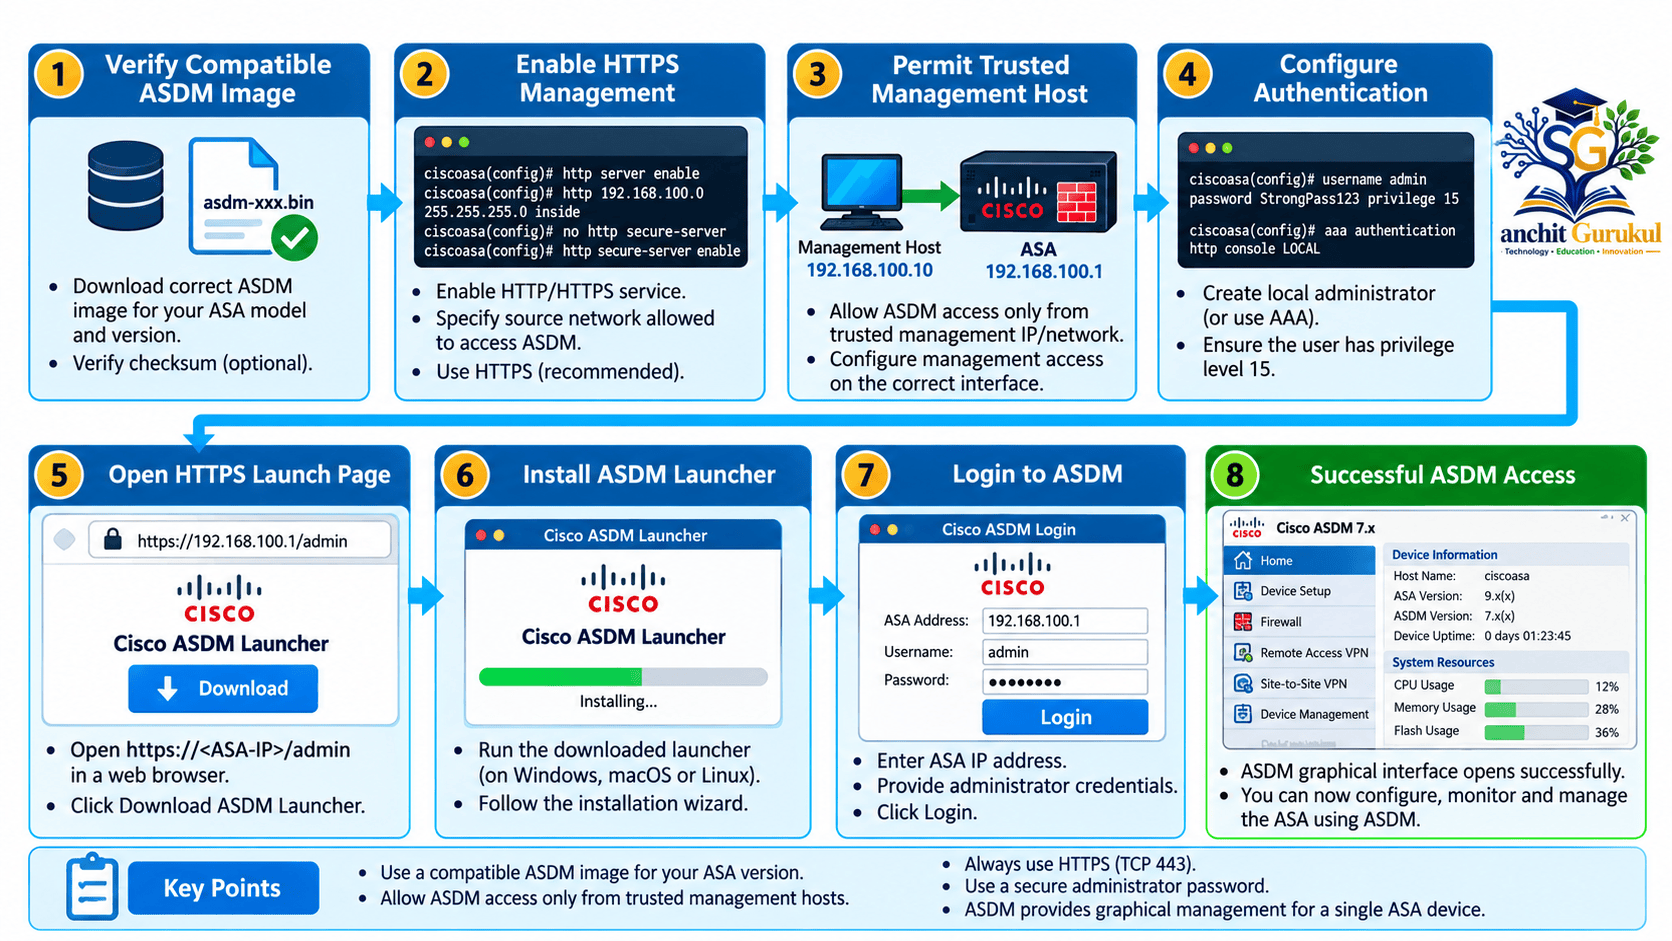
The ASA must have a compatible ASDM software image available and selected.
Connect to the firewall CLI using an authorized administrative session.
Check Storage
dir disk0:Review the available files.
Look for the installed ASDM image.
Example filename pattern:
asdm-.bin
The exact filename depends on the software package.
Check the Selected ASDM Image
show asdm imageIllustrative output:
Device Manager image file, disk0:/asdm-.binReplace the placeholder with the actual image filename.
Select the Correct Image if Necessary
If the compatible ASDM image is already available but not selected, configure its actual path.
configure terminal
asdm image disk0:/.bin
end
The image must exist at the specified location.
Do not copy an outdated filename from a tutorial into a production configuration.
Step 2 — Enable HTTPS Management Access
ASDM uses the ASA’s HTTPS management service.
Enable the ASA HTTP Server
Enter configuration mode.
configure terminal
http server enable
Despite the command name, this enables the management service used for ASDM HTTPS connections.
Allow a Trusted Management Host
For the lab workstation:
http 192.168.100.20 255.255.255.255 managementThis permits ASDM/HTTPS management access from the specified administrator IP through the interface named management.
Verify HTTP Configuration
end
show running-config httpIllustrative relevant lines:
http server enable
http 192.168.100.20 255.255.255.255 managementThese are example configuration lines, not guaranteed output from every ASA.
Step 3 — Configure Administrator Authentication
Allowing HTTPS connectivity is not sufficient.
The administrator must also authenticate successfully.
For this lab, use local ASA authentication.
Create an Administrator Account
configure terminal
username asdmadmin password  privilege 15
Replace the placeholder with an actual approved secret.
Enable Local Authentication for ASDM
aaa authentication http console LOCAL
end
The ASA now uses its local user database for HTTP/ASDM authentication under this configuration.
Save the Configuration
write memoryStep 4 — Download and Launch Cisco ASDM
After enabling HTTPS access, open a supported browser on the administrator workstation.
Open the ASDM Launch Page
https://192.168.100.1/adminUse the actual ASA management address in a production environment.
Cisco documents the /admin HTTPS launch page for ASDM.
Install ASDM Launcher
- Open the ASA HTTPS launch page.
- Select Install ASDM Launcher.
- Download the applicable installer.
- Install the Launcher on the supported workstation.
- Open the ASDM Launcher.
- Enter the ASA management address.
- Enter the authorized administrator credentials.
- Connect to the firewall.
What Happens During Connection?
ASDM establishes a management connection to the ASA.
After successful authentication, it retrieves the information needed to display supported configuration and monitoring views.
Step 5 — Understand the ASDM Interface
Once connected, become familiar with the main administrative areas.
Home
Displays general device and operational information.
Configuration
Provides access to supported configuration features.
Common areas include:
- Device Setup
- Firewall
- Remote Access VPN
- Site-to-Site VPN
- Device Management
Monitoring
Provides operational visibility, including supported connection, interface, VPN, logging and performance information.
Tools
Includes useful troubleshooting and administrative utilities.
Save Configuration
When changes are applied, confirm whether they have been written to the startup configuration.
Applying a change and saving it permanently are separate operations in common ASA workflows.
Step 6 — Use ASDM for Firewall Troubleshooting
One of ASDM’s most useful capabilities is its integrated troubleshooting interface.
Packet Tracer
Packet Tracer simulates how the ASA processes specified traffic.
It can help evaluate:
- Access Control Lists
- NAT behavior
- Interface and routing decisions
- Applicable inspection stages
- Resulting allow or drop decisions
Example Scenario
An internal workstation cannot reach an external HTTPS server.
The administrator wants to determine whether the ASA configuration would permit the connection.
| Parameter | Example |
|---|---|
| Ingress Interface | inside |
| Protocol | TCP |
| Source IP | 192.168.10.25 |
| Source Port | 50000 |
| Destination IP | 198.51.100.25 |
| Destination Port | 443 |
In ASDM, open the supported Packet Tracer tool under the Tools menu.
Enter the relevant flow parameters and run the simulation.
Review the individual processing stages and final result.

Useful Cisco ASA CLI Commands for ASDM Troubleshooting
The CLI remains valuable when ASDM cannot connect.
| Command | Purpose |
|---|---|
show version |
Review ASA version and platform |
show asdm image |
Check selected ASDM image |
dir disk0: |
Review available storage files |
show running-config http |
Review management access configuration |
show running-config aaa |
Review authentication configuration |
show interface ip brief |
Review interface addressing and status |
show route |
Review routing |
show logging |
Review configured logging and available output |
show asp table socket |
Inspect ASA listening sockets |
write memory |
Save running configuration |
Example — Check Management Connectivity Settings
show asdm image
show running-config http
show running-config aaa
show interface ip brief
Review the combined results against the intended configuration.
Common ASDM Problems and Solutions
| Problem | Possible Cause | Recommended Check |
|---|---|---|
| ASDM page does not open | HTTPS server disabled | Check show running-config http |
| Connection times out | Client not permitted or route missing | Review management source and routing |
| Launcher does not start | Java or Launcher compatibility issue | Check Cisco compatibility requirements |
| ASDM image error | Incorrect or missing image | Verify selected image and file |
| Login fails | Incorrect credentials or AAA setup | Review authentication configuration |
| HTTPS certificate warning | Untrusted or unsuitable certificate | Verify certificate and management identity |
| Page works but Launcher fails | Client-side runtime issue | Review Launcher installation |
| Connection fails on custom port | Incorrect HTTPS port used | Check HTTP server configuration |
| ASDM is slow | Client, device or network resource issue | Review performance and connectivity |
Troubleshooting Sequence
- Verify the administrator workstation IP address.
- Confirm connectivity to the ASA management interface.
- Check that the HTTPS server is enabled.
- Confirm the administrator source IP is permitted.
- Verify the selected ASDM image.
- Check administrator authentication.
- Confirm the installed Launcher and Java requirements.
- Review HTTPS port and TLS compatibility.
- Test again using the approved management path.
Advantages and Limitations of Cisco ASDM
Advantages
- Graphical configuration and monitoring
- Reduced need to memorize routine CLI syntax
- Integrated packet-tracing and capture tools
- Convenient firewall and VPN workflows
- Useful visibility into device configuration
- Suitable for device-focused administration
Limitations
- Java and Launcher compatibility requirements
- Primarily device-oriented management
- Some advanced operations may still need CLI
- Supported features differ by ASA release
- Performance depends on device and workstation resources
- Not a replacement for broad centralized security orchestration
Cisco ASDM Security Best Practices
1. Restrict ASDM Access
Allow HTTPS management only from trusted hosts or approved management networks.
Avoid exposing ASDM directly to the public internet.
2. Use Strong Authentication
Use individual administrative accounts, appropriate privileges and supported authentication controls.
3. Maintain Compatible Software
Review Cisco’s ASA and ASDM compatibility documentation before upgrades.
4. Use Trusted Management Certificates
Configure appropriate HTTPS certificates and validate the management endpoint’s identity.
5. Back Up Configuration
Use supported backup procedures before major changes.
Cisco documents complete backup capabilities in ASDM for applicable single-context configurations.
6. Monitor Administrative Activity
Enable appropriate logging and review significant configuration changes.
7. Test Changes Carefully
Use Packet Tracer and approved connectivity tests before and after significant modifications.
8. Review Resource Utilization
Monitor CPU, memory, interfaces and connection information to detect operational problems.
Key Takeaways — Cisco ASDM Fundamentals
- ASDM is a graphical management application for supported Cisco ASA firewalls.
- The ASA performs traffic inspection; ASDM provides the management interface.
- ASDM connects through HTTPS.
- The ASDM Launcher is used to run the management application.
- Java requirements depend on the ASDM package and release.
Key Takeaways — Installation
- Verify the compatible ASDM image.
- Enable the ASA HTTPS management service.
- Restrict access to trusted administrator hosts.
- Configure appropriate authentication.
- Open the HTTPS
/adminlaunch page. - Install the supported ASDM Launcher.
- Verify connectivity and save approved configuration changes.
Key Takeaways — Troubleshooting
- Packet Tracer helps simulate traffic handling.
- CLI commands help diagnose ASDM connection problems.
- Missing images, HTTPS restrictions and authentication errors are common causes of failed access.
- An ASDM graphical result should be validated against actual device behavior when necessary.
Conclusion
Cisco ASDM makes many Cisco ASA administration tasks easier by providing a graphical interface for firewall rules, NAT, VPN configuration, monitoring and troubleshooting.
It is particularly useful when administrators need to understand an existing configuration or perform routine device management without relying exclusively on CLI commands.
However, ASDM is not simply a browser-based firewall dashboard.
Successful deployment requires a compatible software image, correct Java or Launcher environment, secure HTTPS management access and valid administrator authentication.
Understanding these requirements, alongside the ASA CLI, helps administrators manage their firewalls more securely and troubleshoot problems more confidently.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


