
An Access Control List (ACL) is a set of ordered rules used by network devices to identify and control traffic.
ACLs are commonly configured on routers, Layer 3 switches, firewalls, and other network devices to determine which traffic should be permitted and which traffic should be denied.
A typical ACL can evaluate information such as:
- Source IP address
- Destination IP address
- IP protocol
- TCP or UDP port
- Traffic direction
- Interface
ACLs are fundamental to network administration because they provide a relatively simple way to control communication between networks.
How Access Control Lists Work
ACLs consist of individual entries called Access Control Entries (ACEs).
Each ACE defines criteria that traffic must match and specifies an action such as:
- permit
- deny
For a traditional Cisco IOS ACL, entries are evaluated sequentially.
The basic logic is:
- A packet reaches an interface where an ACL is applied.
- The device evaluates the packet against the ACL.
- ACL entries are checked in sequence.
- When a matching ACE is found, its permit or deny action is applied.
- Processing of that ACL stops for that packet.
- If no configured ACE matches, the packet reaches the implicit deny at the end of the ACL.
The important rule to remember is:
First matching ACE wins.
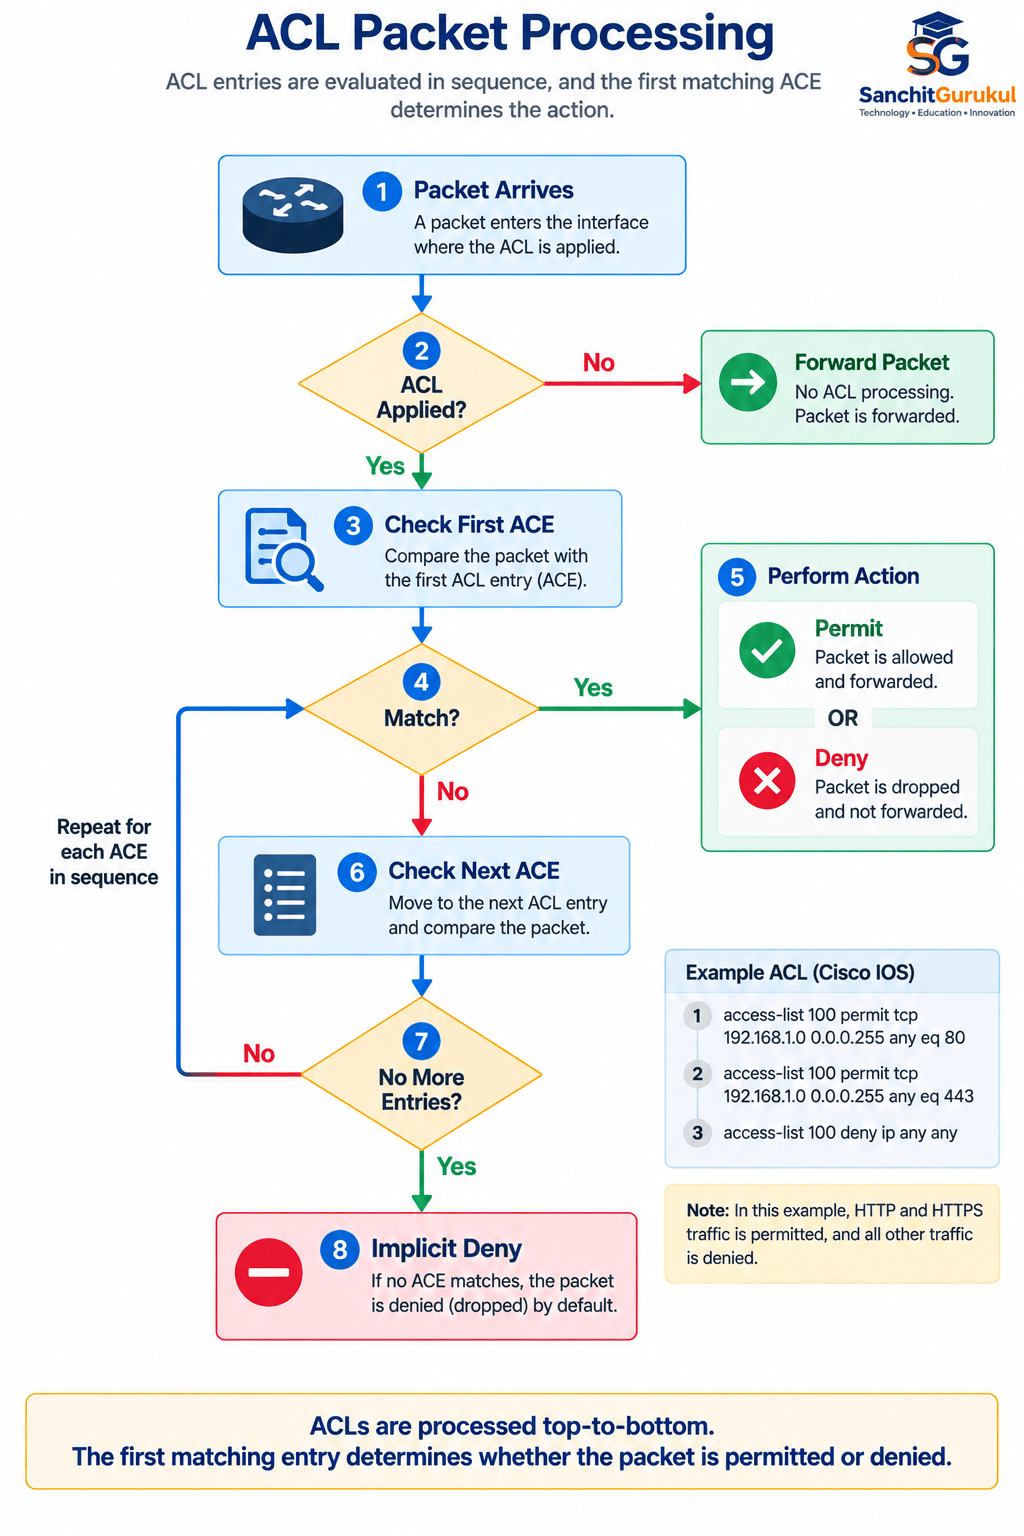
ACL Processing Example
Consider this simplified policy:
- Permit network
192.168.1.0/24 - Deny everything else
Traffic sourced from 192.168.1.25 matches the first rule and is permitted.
Traffic sourced from 10.10.10.25 does not match the first rule and is denied by the following deny rule.
The Implicit Deny
Cisco ACLs have an implicit deny at the end.
Conceptually:
deny any
or, for an extended IP ACL:
deny ip any any
Therefore, traffic that does not match a permit statement is denied when it reaches the end of the ACL.
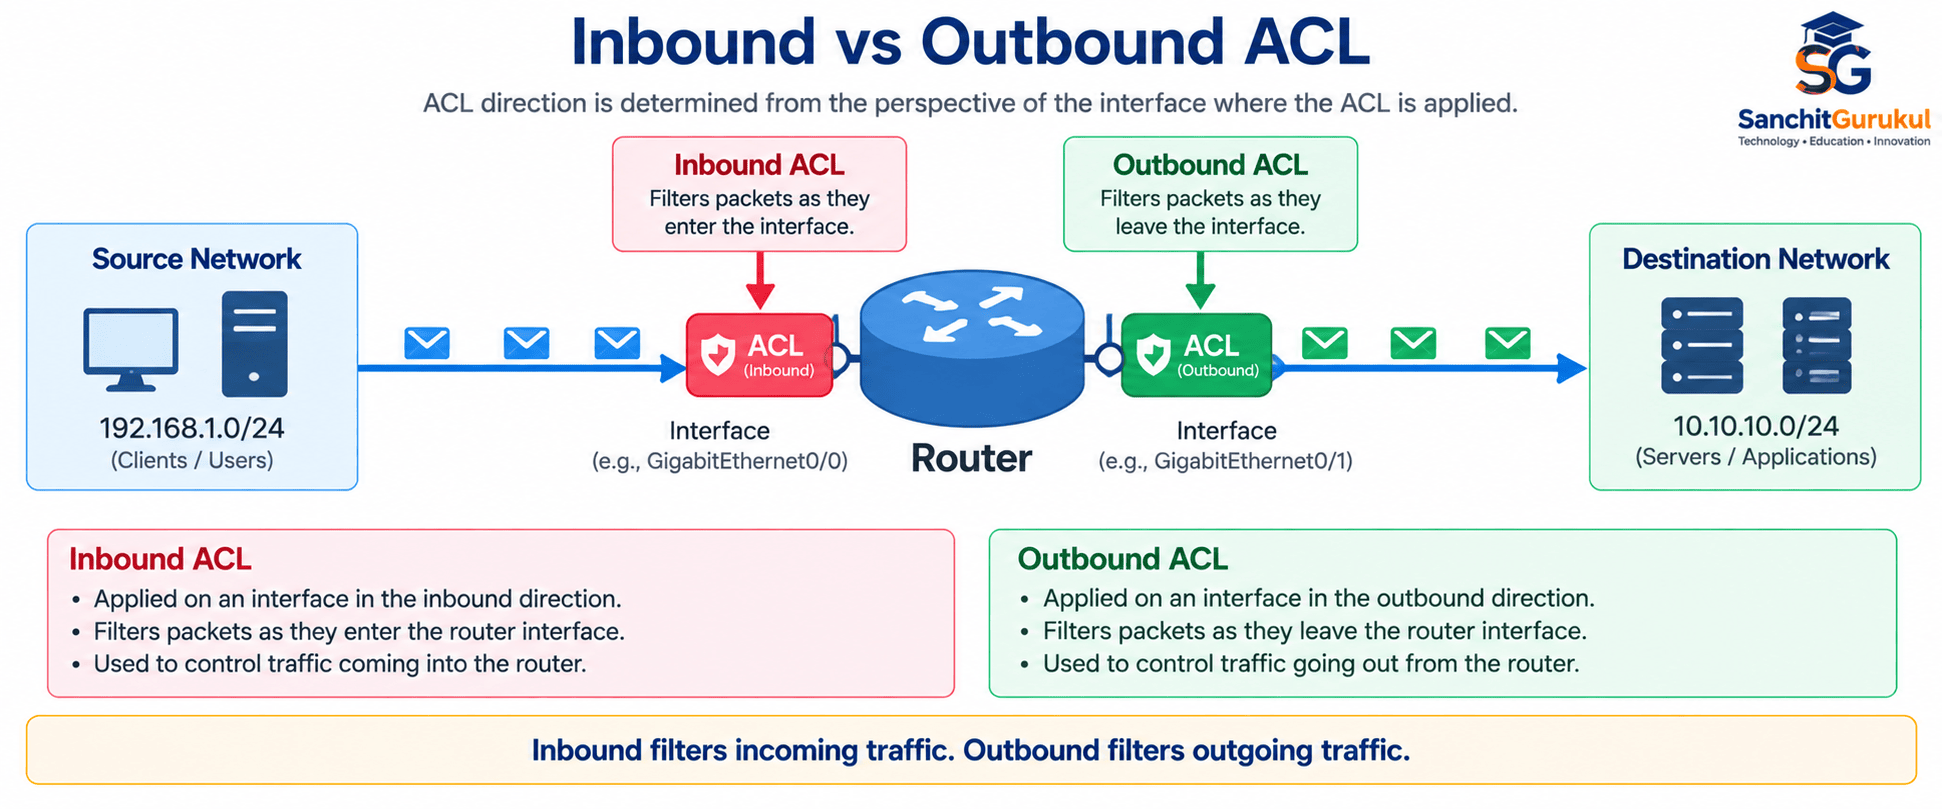
Inbound vs Outbound ACL
An ACL can be applied to an interface in a particular direction.
Inbound ACL
Evaluates packets as they enter the interface.
Outbound ACL
Evaluates packets before they leave the interface.
Types of Access Control Lists
Cisco IOS commonly uses Standard ACLs and Extended ACLs.
ACLs can also be configured using numbers or names.
Standard ACL
A Standard IPv4 ACL primarily matches the source IPv4 address.
It does not provide the same destination, protocol, and Layer 4 port matching available with an Extended ACL.
Typical use cases include:
- Allowing a specific source network
- Blocking a particular source
- Restricting management access
- Simple traffic classification
Traditionally, Standard ACLs are placed relatively close to the destination because they provide less granular traffic matching.
Extended ACL
An Extended ACL provides much more detailed traffic matching.
Depending on the protocol and syntax, it can match information such as:
- Source IPv4 address
- Destination IPv4 address
- IP protocol
- TCP source/destination ports
- UDP source/destination ports
- ICMP information
- Other supported criteria
For example, an Extended ACL can express a policy such as:
Permit HTTP traffic from 192.168.1.0/24 to a specific web server while denying other traffic.
Traditionally, Extended ACLs are often placed relatively close to the source so unwanted traffic can be filtered before it travels farther through the network.
Numbered ACL
A numbered ACL is identified using an ACL number.
For example:
10
or:
101
The permitted number ranges depend on the ACL type and platform/software support.
Named ACL
A Named ACL uses a descriptive name instead of relying only on an ACL number.
Examples include:
ALLOW_INTERNAL
WEB_ACCESS
FILTER_TRAFFIC
Named ACLs are useful because descriptive names can make configurations easier to understand and maintain.
Standard vs Extended ACL
| Capability | Standard ACL | Extended ACL |
|---|---|---|
| Source IPv4 matching | Yes | Yes |
| Destination IPv4 matching | No | Yes |
| Protocol matching | No | Yes |
| TCP/UDP port matching | No | Yes |
| Granularity | Lower | Higher |
| Typical placement guideline | Closer to destination | Closer to source |
| Simple source filtering | Excellent | Possible |
| Application-specific filtering | No | Yes |
Cisco Standard ACL Configuration
Consider the following requirement:
Allow traffic sourced from 192.168.1.0/24 and deny other source addresses matched by this ACL.
Step 1: Create the Standard ACL
access-list 10 permit 192.168.1.0 0.0.0.255
access-list 10 deny any
Step 2: Apply the ACL to an Interface
interface GigabitEthernet0/1
 ip access-group 10 in
Understanding the Configuration
The first ACE is:
access-list 10 permit 192.168.1.0 0.0.0.255
It permits source addresses in:
192.168.1.0/24
The wildcard mask:
0.0.0.255
corresponds to the /24 network mask for this ACL match.
The second ACE is:
access-list 10 deny any
It explicitly denies all other source addresses.
Understanding Wildcard Masks
Cisco IPv4 ACLs traditionally use wildcard masks.
A wildcard mask is effectively the inverse of the corresponding subnet mask for common network matching.
Example:
Subnet mask:
255.255.255.0
Wildcard mask:
0.0.0.255
Therefore:
192.168.1.0 0.0.0.255
matches addresses from:
192.168.1.0 through 192.168.1.255
Common examples:
| Prefix | Subnet Mask | Wildcard Mask |
|---|---|---|
| /32 | 255.255.255.255 | 0.0.0.0 |
| /30 | 255.255.255.252 | 0.0.0.3 |
| /29 | 255.255.255.248 | 0.0.0.7 |
| /28 | 255.255.255.240 | 0.0.0.15 |
| /27 | 255.255.255.224 | 0.0.0.31 |
| /26 | 255.255.255.192 | 0.0.0.63 |
| /25 | 255.255.255.128 | 0.0.0.127 |
| /24 | 255.255.255.0 | 0.0.0.255 |
| /16 | 255.255.0.0 | 0.0.255.255 |
| /8 | 255.0.0.0 | 0.255.255.255 |
Cisco Extended and Named ACL Configuration
Extended ACLs provide much more granular traffic control.
Consider this requirement:
- Permit HTTP from
192.168.1.0/24 - Permit DNS from
192.168.2.0/24 - Deny other IP traffic
Step 1: Create an Extended Named ACL
ip access-list extended FILTER_TRAFFICThis enters Extended Named ACL configuration mode.
Step 2: Add ACL Rules
permit tcp 192.168.1.0 0.0.0.255 any eq 80
permit udp 192.168.2.0 0.0.0.255 any eq 53
deny ip any any
The first ACE:
permit tcp 192.168.1.0 0.0.0.255 any eq 80
permits TCP traffic:
Source: 192.168.1.0/24
Destination: Any
Destination Port: TCP 80 / HTTP
The second ACE:
permit udp 192.168.2.0 0.0.0.255 any eq 53
permits UDP traffic:
Source: 192.168.2.0/24
Destination: Any
Destination Port: UDP 53 / DNS
The final ACE:
deny ip any any
explicitly denies other IPv4 traffic evaluated by the ACL.
Step 3: Apply the ACL
interface GigabitEthernet0/1
 ip access-group FILTER_TRAFFIC in
This applies FILTER_TRAFFIC to traffic entering GigabitEthernet0/1.
Named Standard ACL Example
Now consider another requirement:
Permit these source networks:
192.168.1.0/24192.168.2.0/24
and deny other sources.
Create the Named Standard ACL:
ip access-list standard ALLOW_INTERNAL
 permit 192.168.1.0 0.0.0.255
 permit 192.168.2.0 0.0.0.255
 deny any
Apply it to an interface:
interface GigabitEthernet0/0
 ip access-group ALLOW_INTERNAL in
The important difference is:
ALLOW_INTERNAL is a Named Standard ACL.
FILTER_TRAFFIC is a Named Extended ACL.
“Named” identifies how the ACL is referenced; Standard or Extended determines its matching capabilities.
ACL Verification, Placement and Troubleshooting
Creating the ACL is only part of the task.
Always verify the configuration and traffic behavior.
Display Configured ACLs
show access-listsFor IPv4 ACLs, depending on the Cisco platform/software:
show ip access-listsThese commands can help display:
- ACL names or numbers
- Permit entries
- Deny entries
- Sequence information
- Match counters where supported
Check the Interface
show ip interface GigabitEthernet0/1Verify that the correct ACL is attached in the intended direction.
Look for whether the ACL is applied:
- Inbound
- Outbound
Check the Running Configuration
show running-configOr inspect the relevant ACL/interface configuration according to the platform.
Common ACL Problems
| Problem | Likely Cause |
|---|---|
| Valid traffic is blocked | Missing permit ACE |
| ACL appears ineffective | Applied to wrong interface |
| ACL filters wrong traffic | Incorrect inbound/outbound direction |
| Rule never matches | Earlier ACE matches first |
| Wrong hosts are matched | Incorrect wildcard mask |
| HTTP works but another service fails | Required protocol/port not permitted |
| DNS behaves inconsistently | Only UDP or TCP 53 permitted when both are required |
| Unexpected traffic denied | Implicit deny reached |
Rule Order
ACL rule order is extremely important.
Consider:
deny ip any any
permit tcp 192.168.1.0 0.0.0.255 any eq 80
The permit rule will never be reached for IP traffic because the first ACE already matches and denies it.
A better order for that policy is:
permit tcp 192.168.1.0 0.0.0.255 any eq 80
deny ip any anyACL Placement
A traditional guideline is:
Standard ACL → closer to destination
because Standard ACLs primarily identify the source address and provide less granular filtering.
Extended ACL → closer to source
because Extended ACLs can identify both endpoints, protocol, and ports, allowing unwanted traffic to be discarded earlier.
Advantages, Limitations and Security Best Practices
ACLs remain useful because they provide straightforward and efficient traffic control.
Advantages of ACLs
Security Control
ACLs can restrict unwanted communication between networks and systems.
Traffic Filtering
Administrators can define which traffic is permitted or denied.
Granular Matching
Extended ACLs can match combinations of:
- Source
- Destination
- Protocol
- TCP/UDP ports
Infrastructure Protection
ACLs can help restrict access to:
- Management interfaces
- Network infrastructure
- Internal networks
- Sensitive services
Cost Efficiency
Basic ACL functionality is already available on many routers and Layer 3 switches.
Limitations of ACLs
Configuration Complexity
Large ACLs can become difficult to understand and maintain.
Rule-Order Dependency
An incorrect ACE placed earlier in the ACL can change the result of all entries below it.
Human Error
Incorrect wildcard masks, ports, directions, or interface placement can cause outages or security gaps.
Limited Application Context
Traditional ACLs primarily evaluate network and transport-layer information and do not provide the same application context as modern NGFW, WAF, or application-security systems.
Static Policy
Traditional ACL entries normally remain unchanged until an administrator or automation system modifies them.
Performance Considerations
ACL processing can consume device resources, but the actual performance impact depends heavily on:
- Platform
- Hardware
- ACL implementation
- Number of ACEs
- Traffic rate
- Feature combination
- Software version
ACL Best Practices
Use the following practices when designing ACLs:
- Define the traffic requirement before creating the ACL.
- Use descriptive Named ACLs where appropriate.
- Place more specific rules carefully.
- Remember that the first matching ACE determines the action.
- Account for the implicit deny.
- Verify wildcard masks.
- Verify TCP and UDP requirements.
- Confirm inbound or outbound direction.
- Review ACL counters where available.
- Remove obsolete rules carefully.
- Document the purpose of important ACLs.
- Test changes before production deployment where possible.
- Maintain a rollback plan for remote changes.
- Review ACLs periodically.
Common Questions
What Does ACL Stand For?
ACL stands for Access Control List.
What Is an ACE?
ACE stands for Access Control Entry.
An ACL contains one or more ACEs.
Each ACE defines matching criteria and an action such as permit or deny.
How Are ACL Rules Processed?
Traditional Cisco ACL entries are processed sequentially.
The first matching ACE determines the result.
What Happens If Nothing Matches?
The traffic reaches the implicit deny at the end of the ACL and is denied.
What Is the Difference Between Standard and Extended ACLs?
A Standard IPv4 ACL primarily matches the source IPv4 address.
An Extended IPv4 ACL can provide more granular matching based on source, destination, protocol, and supported Layer 4 information.
What Is the Difference Between Named and Numbered ACLs?
A Numbered ACL is referenced by a number.
A Named ACL uses a descriptive name.
A Named IPv4 ACL can still be either Standard or Extended.
What Does any Mean?
any represents any address within the relevant source or destination field.
What Does host Mean?
host identifies one specific IP address.
For example:
host 192.168.1.10is a convenient representation of a single IPv4 host match.
What Does eq 80 Mean?
eq means equal.
In an Extended TCP ACL:
eq 80matches TCP port 80 in the relevant port position.
Are ACLs the Same as Firewalls?
No.
ACLs provide traffic-filtering functionality, while modern firewalls can additionally provide features such as:
- Stateful security inspection
- Application identification
- User-based policy
- Threat prevention
- URL filtering
- TLS inspection
- Malware detection
The exact capabilities depend on the platform.
Summary
An Access Control List (ACL) is an ordered collection of rules used to identify and control network traffic.
The most important concepts to remember are:
ACL entries are evaluated in sequence.
The first matching ACE determines the action.
Unmatched traffic reaches an implicit deny.
Standard IPv4 ACLs primarily filter according to the source IPv4 address, while Extended IPv4 ACLs can provide much more granular control using information such as:
- Source address
- Destination address
- Protocol
- TCP or UDP ports
Named ACLs improve readability and management but can still be either Standard or Extended.
When implementing ACLs, always verify:
- Rule order
- Source and destination
- Wildcard masks
- Protocol
- Port numbers
- Interface
- Inbound/outbound direction
- Implicit deny behavior
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.

