
IPv6 should be treated as a production protocol that requires the same level of security planning, monitoring, and policy enforcement as IPv4.
One of the biggest IPv6 security problems is not the protocol itself.
It is unmanaged IPv6.
An organization may carefully secure IPv4 while endpoints, servers, network devices, and cloud systems also communicate using IPv6.
If IPv6 is not included in the security architecture, attackers may find:
- Less restrictive firewall policies
- Missing IDS/IPS inspection
- Unmonitored IPv6 traffic
- Rogue Router Advertisements
- Uncontrolled DHCPv6
- Unnecessary transition tunnels
- Internet-facing services exposed through IPv6
- Incomplete asset inventories
- Missing vulnerability scans
A secure IPv6 deployment should therefore apply consistent controls across:
IPv4 + IPv6
rather than assuming existing IPv4 protection automatically covers both protocols.

Build an Intentional IPv6 Security Baseline
The first IPv6 security decision should be:
Are we intentionally using IPv6 on this network?
Avoid leaving IPv6 enabled but unmanaged.
Inventory IPv6 Assets
Identify systems with:
- Global IPv6 addresses
- Unique Local Addresses
- Link-local addresses
- IPv6 default routes
- IPv6 DNS records
- IPv6 listening services
Inventory should include:
- Workstations
- Servers
- Routers
- Switches
- Firewalls
- Load balancers
- Wireless infrastructure
- Cloud networks
- VPN systems
- Security appliances
On Linux:
ip -6 addr showDisplay IPv6 routes:
ip -6 route showDisplay IPv6 neighbors:
ip -6 neigh showDo Not Assume an IPv4-Only Network Has No IPv6
Modern operating systems commonly enable IPv6 by default.
Even without a global IPv6 prefix, devices normally configure link-local addresses from:
fe80::/10A malicious device on the same Layer 2 network may also attempt to introduce IPv6 connectivity using rogue Router Advertisements.
Therefore:
No planned IPv6 deployment does not necessarily mean no IPv6 traffic exists.
Disable IPv6 Only When It Is Truly Unneeded
If IPv6 is intentionally prohibited on a particular environment or interface, disabling or filtering it may reduce unnecessary exposure.
However, do not blindly disable IPv6 across operating systems without:
- Testing application dependencies
- Reviewing vendor guidance
- Understanding link-local behavior
- Confirming management requirements
A better organizational policy is:
Either manage IPv6 securely or intentionally disable/restrict it where supported and appropriate.
Avoid the middle state where IPv6 operates without security ownership.
Maintain IPv4 and IPv6 Policy Parity
If an application is protected in IPv4 by:
- Firewall
- ACL
- IDS/IPS
- WAF
- Vulnerability scanner
- SIEM
verify the equivalent IPv6 path.
A useful review question is:
Could the same server be reached over IPv6 using a less restrictive policy?
Secure IPv6 Addressing and the First Hop
The local network is one of the most important IPv6 security areas because IPv6 relies heavily on Neighbor Discovery and Router Advertisements.
Use Addressing Appropriate to the Device Role
IPv6 addressing should be planned rather than randomly assigned without operational purpose.
Common address types include:
Global Unicast Addresses
Used for globally routable IPv6 communication.
Unique Local Addresses
Defined within:
fc00::/7In practice, locally generated ULA prefixes normally use:
fd00::/8ULAs are intended for local communication and are not expected to be routed across the global Internet.
However:
ULA is not a security mechanism.
Internal systems using ULAs still require:
- Firewall policy
- Segmentation
- Authentication
- Access control
Avoid Predictable MAC-Derived Interface Identifiers
Older IPv6 deployments commonly generated interface identifiers using Modified EUI-64, which could expose stable link-layer information.
RFC 8064 recommends stable interface identifiers that do not embed persistent MAC-address information.
For systems that need temporary client addresses, RFC 8981 defines temporary-address mechanisms designed to improve privacy.
A practical model is:
Servers and infrastructure
Use intentionally managed stable addresses.
User endpoints
Use operating-system-supported privacy mechanisms where appropriate.
Privacy Addresses Are Not a Firewall
Temporary addresses can make long-term host tracking and simple address prediction more difficult.
They do not replace:
- Firewall controls
- Endpoint security
- NAC
- Segmentation
- Authentication
They can also complicate:
- Asset tracking
- Incident investigation
- Log correlation
Security and privacy requirements should therefore be balanced.
Protect Router Advertisements
Router Advertisements are fundamental to IPv6.
Hosts use them to learn information including:
- Default routers
- Prefixes
- Autoconfiguration parameters
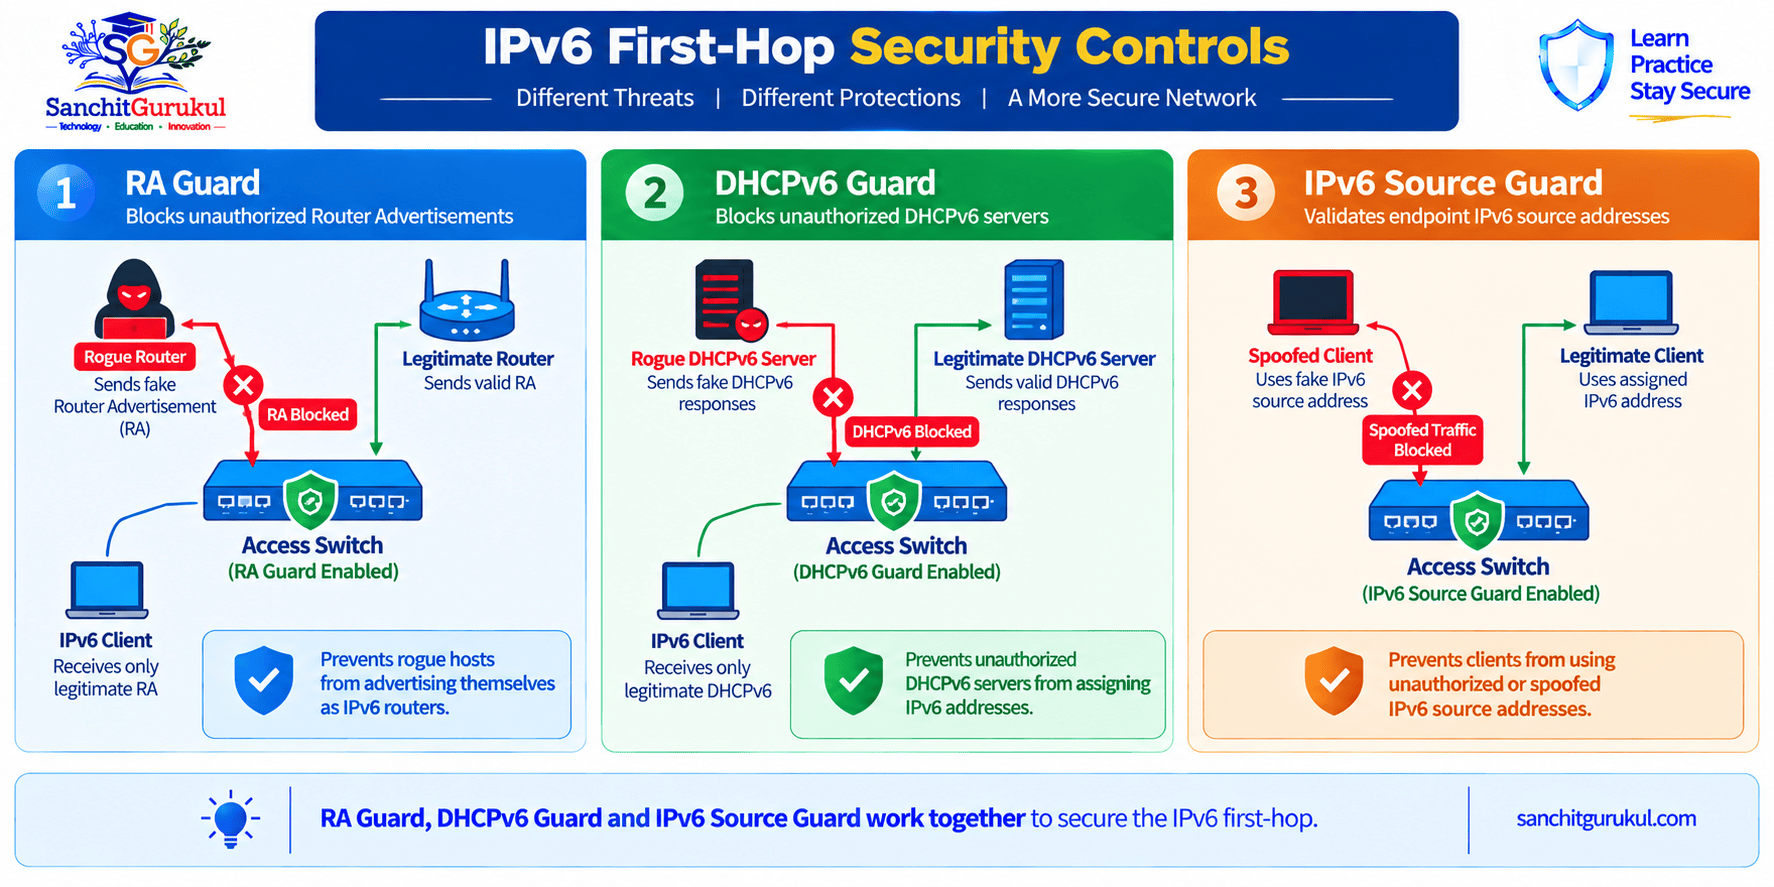
An unauthorized host sending RAs can disrupt or redirect traffic.
Deploy:
RA Guard
on supported access switches.
The principle is:
Authorized router-facing ports
RA permitted.
Ordinary host-facing ports
Unauthorized RA blocked.
Use Modern RA Guard Implementations
Early RA Guard implementations could be bypassed using IPv6 extension headers or fragmentation techniques.
Use network platforms implementing the improvements described by RFC 7113 and keep switch software current.
Protect DHCPv6
Use DHCPv6 Guard or DHCPv6-Shield where appropriate.
Only trusted ports connected to legitimate:
- DHCPv6 servers
- DHCPv6 relays
should be permitted to send DHCPv6 server messages toward clients.
Use Source Validation
Where supported, consider:
- IPv6 Source Guard
- SAVI
- Neighbor Discovery inspection
- Device tracking
These controls can help prevent hosts from using unauthorized IPv6 source addresses.
Harden IPv6 Firewalls, ICMPv6 and Network Services
IPv6 should use explicit security policy rather than relying on obscurity or the absence of NAT.
Use Stateful IPv6 Firewalling
Implement stateful inspection for IPv6 just as you would for IPv4.
Permit only:
- Required applications
- Authorized sources
- Approved destinations
- Necessary management access
Use a default-deny approach where appropriate to the environment.
NAT Is Not a Security Requirement
IPv6 generally allows globally unique addresses without requiring traditional IPv4-style NAT.
This does not mean internal hosts should automatically be reachable from the Internet.
A stateful firewall can permit outbound sessions while blocking unsolicited inbound connections.
Security comes from:
Firewall policy
not from address translation itself.
Do Not Block All ICMPv6
ICMPv6 performs critical IPv6 functions.
It is used for:
- Error reporting
- Neighbor Discovery
- Router Discovery
- Path MTU Discovery
- Duplicate Address Detection
Blocking ICMPv6 indiscriminately can break legitimate IPv6 connectivity.
For example, IPv6 Path MTU Discovery depends on:
ICMPv6 Packet Too Big — Type 2
If these messages are blocked, a TCP connection may establish successfully but later fail when larger packets are transmitted.
Important ICMPv6 Error Messages
RFC 4890 identifies important ICMPv6 messages that should generally not be indiscriminately dropped.
Examples include:
| Type | Purpose |
|---|---|
| 1 | Destination Unreachable |
| 2 | Packet Too Big |
| 3 | Time Exceeded |
| 4 | Parameter Problem |
Local-link IPv6 operation additionally relies on Neighbor Discovery messages such as:
- Router Solicitation
- Router Advertisement
- Neighbor Solicitation
- Neighbor Advertisement
Apply filtering according to:
- Interface
- Direction
- Network role
- Message type
rather than using a blanket deny icmpv6 policy.
Rate Limit Carefully
Rate limiting can help protect router control planes from abusive traffic.
However, aggressive ICMPv6 rate limits can interfere with legitimate:
- Neighbor Discovery
- Error reporting
- Path MTU Discovery
Apply platform-specific control-plane protection instead of arbitrary limits that break IPv6 operation.
Inspect IPv6 Extension Headers
Security devices should correctly parse IPv6 extension-header chains.
Evaluate support on:
- Firewalls
- IDS/IPS
- Load balancers
- DDoS systems
- Packet-analysis tools
Do not automatically block every extension header.
Instead:
- Allow required functionality.
- Reject invalid combinations.
- Apply organizational policy.
- Keep security devices updated.
Audit Listening Services
A service may listen on IPv6 even when administrators only tested IPv4.
On Linux:
sudo ss -lntupLook for listeners bound to addresses such as:
:::or:
[::]Verify that every IPv6 listening service is:
- Required
- Patched
- Authenticated
- Protected by firewall policy
Secure DNS, Routing and Transition Technologies
IPv6 security extends beyond the endpoint and first-hop network.
Control AAAA Records
IPv6-enabled services are commonly published using:
AAAA records
Only publish externally reachable IPv6 addresses for services that are intentionally available.
Do not publish sensitive internal systems simply because they have globally scoped IPv6 addresses.
Internal-only services can use appropriately controlled internal DNS where required.
Use DNSSEC Where Appropriate
DNSSEC can provide origin authentication and integrity validation for signed DNS data.
That includes:
- A records
- AAAA records
- Other signed DNS information
DNSSEC does not encrypt DNS queries.
It protects the authenticity and integrity of signed DNS responses.
Split DNS Where Operationally Appropriate
Organizations may use different internal and external DNS views.
This can prevent unnecessary publication of:
- Internal hostnames
- Internal IPv6 addresses
- Management services
However, split DNS adds operational complexity and should be managed carefully.
DNS64 Is Not a Security Feature
DNS64 is commonly used with NAT64 to provide IPv6-only clients with access to IPv4 services.
It synthesizes AAAA responses in specific scenarios.
DNS64 should not be confused with:
- DNSSEC
- DNS filtering
- DNS security
If NAT64/DNS64 is deployed, ensure:
- Security policy covers the translation path.
- Logs preserve useful source/destination information.
- DNSSEC validation behavior is understood.
- Monitoring includes translated traffic.
Remove Unnecessary Transition Mechanisms
IPv6 transition technologies historically included:
- 6to4
- Teredo
- ISATAP
- Configured tunnels
Unmanaged tunnels can bypass network visibility or firewall policy.
RFC 7123 documents security risks associated with IPv6 operating inside environments believed to be IPv4-only.
If a transition mechanism is not required:
- Disable it on endpoints where possible.
- Block unwanted tunnel protocols at network boundaries.
- Monitor for unexpected tunneled IPv6 traffic.
6to4 has been formally deprecated and should not be deployed as a general IPv6 transition mechanism.
Protect IPv6 Routing
For routed enterprise networks:
- Authenticate routing protocols where supported.
- Restrict routing neighbors.
- Filter unexpected prefixes.
- Apply route-policy controls.
- Monitor route changes.
- Protect router management interfaces.
Do not accept unexpected IPv6 routes simply because the prefix appears syntactically valid.
Monitor, Log and Audit IPv6
A network is difficult to defend if security tools cannot see its IPv6 traffic.
Enable IPv6 Logging
Verify that:
- Firewalls log IPv6 sessions.
- IDS/IPS understands IPv6.
- SIEM parsers support IPv6 addresses.
- VPN logs capture IPv6.
- DNS logs contain AAAA activity.
- DHCPv6 events are collected.
- RA Guard violations are recorded.
Monitor First-Hop Activity
Useful events include:
- Unexpected Router Advertisements
- New DHCPv6 servers
- Neighbor table changes
- Duplicate Address Detection failures
- New default routers
- Source Guard violations
Capture IPv6 Traffic
On Linux:
sudo tcpdump -nn -i any ip6Capture ICMPv6:
sudo tcpdump -nn -i any icmp6Wireshark IPv6 Filters
Display all IPv6:
ipv6Display ICMPv6:
icmpv6Router Advertisements:
icmpv6.type == 134Neighbor Advertisements:
icmpv6.type == 136DHCPv6:
dhcpv6Include IPv6 in Vulnerability Management
Make sure vulnerability scanners assess:
- IPv6 server addresses
- IPv6 web services
- Firewall exposure
- Management interfaces
- Cloud IPv6 endpoints
Scanning only the IPv4 address of a dual-stack server provides incomplete coverage.
Include IPv6 in Incident Response
Incident-response procedures should support:
- IPv6 addresses in IOC searches
- IPv6 firewall queries
- IPv6 packet capture
- IPv6 DNS investigation
- Neighbor Discovery analysis
Analysts should understand compressed notation such as:
2001:db8:10::25and avoid relying on string matching that fails when the same IPv6 address is represented differently.

Operational Best Practices and Key Takeaways
IPv6 security should be continuously maintained rather than treated as a one-time deployment project.
Maintain Configuration Standards
Create approved standards for:
- IPv6 addressing
- SLAAC
- DHCPv6
- Router Advertisements
- First-hop security
- Firewall policy
- DNS
- Routing
- Logging
Review IPv6 Changes
Include IPv6 in change management for:
- New applications
- Firewall changes
- New VLANs
- Cloud deployments
- VPN changes
- Network migrations
Train Operations and Security Teams
Teams responsible for IPv6 should understand:
- Address notation
- Neighbor Discovery
- Router Advertisements
- DHCPv6
- ICMPv6
- Extension headers
- Firewalling
- Troubleshooting
IPv6 should not be treated as an obscure specialist technology if it is active on production endpoints.
Audit Regularly
Periodic reviews should identify:
- Unknown IPv6 prefixes
- Unexpected global addresses
- Unauthorized routers
- Rogue DHCPv6
- Exposed services
- Firewall-policy differences
- Obsolete tunnels
- Missing security telemetry
Key Takeaways
- IPv6 should be either intentionally managed or intentionally restricted—not left unmanaged.
- Apply equivalent security policy to IPv4 and IPv6 in dual-stack environments.
- Inventory IPv6 addresses, routes, DNS records, listening services, and cloud endpoints.
- ULA addressing can support internal communication but is not a substitute for firewalling or segmentation.
- Avoid predictable MAC-derived interface identifiers; use modern stable or temporary addressing mechanisms as appropriate.
- RA Guard helps protect access networks from unauthorized Router Advertisements.
- DHCPv6 Guard protects against rogue DHCPv6 servers but does not replace RA Guard.
- Use source validation, ND inspection, or SAVI-style controls where supported.
- Do not broadly block ICMPv6 because several message types are essential to IPv6 operation.
- Apply stateful IPv6 firewall policy and audit services listening on IPv6.
- Disable or control unnecessary IPv6 transition and tunneling technologies.
- Ensure logging, SIEM, IDS/IPS, vulnerability management, and incident response all support IPv6.
Summary
IPv6 security does not require abandoning the security principles already used for IPv4.
The same fundamental controls still matter:
- Least privilege
- Segmentation
- Stateful firewalling
- Secure routing
- Monitoring
- Vulnerability management
- Incident response
IPv6 simply requires those controls to understand additional mechanisms such as:
- Neighbor Discovery
- Router Advertisements
- SLAAC
- DHCPv6
- ICMPv6
- Extension headers
- IPv6 addressing
A practical IPv6 security strategy should therefore follow this model:
Know your IPv6 assets → Secure the first hop → Enforce firewall policy → Preserve required ICMPv6 → Control addressing and DNS → Disable unnecessary tunnels → Monitor everything → Audit regularly
The most important rule is:
Do not allow IPv6 to become the less-protected path through your network.
If an organization operates both IPv4 and IPv6, attackers should not gain an advantage simply by choosing IPv6.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


