
LDAP, or Lightweight Directory Access Protocol, is an Internet protocol used by applications and systems to access and manage information stored in directory services.
A directory commonly contains information about:
- Users
- Groups
- Computers
- Applications
- Email addresses
- Organizational structures
- Service accounts
- Network resources
- Security-related attributes
LDAP is commonly seen in enterprise environments where applications need a centralized way to locate users, retrieve directory information, or validate credentials.
However, an important distinction is:
LDAP is a protocol—not the directory database itself.
Products such as OpenLDAP, 389 Directory Server, Red Hat Directory Server, and Microsoft Active Directory Domain Services provide directory services that can be accessed using LDAP.
LDAP is also not automatically:
- Single Sign-On
- Multi-Factor Authentication
- Role-Based Access Control
- Kerberos
- RADIUS
- OAuth
- OpenID Connect
It can participate in identity and authentication architectures that use those technologies.

What Is LDAP and How Is Directory Data Organized?
The current LDAP specification is commonly referred to as:
LDAPv3
LDAPv3 is defined through the RFC 4510 family of specifications.
LDAP follows concepts derived from the X.500 directory model and organizes information hierarchically.
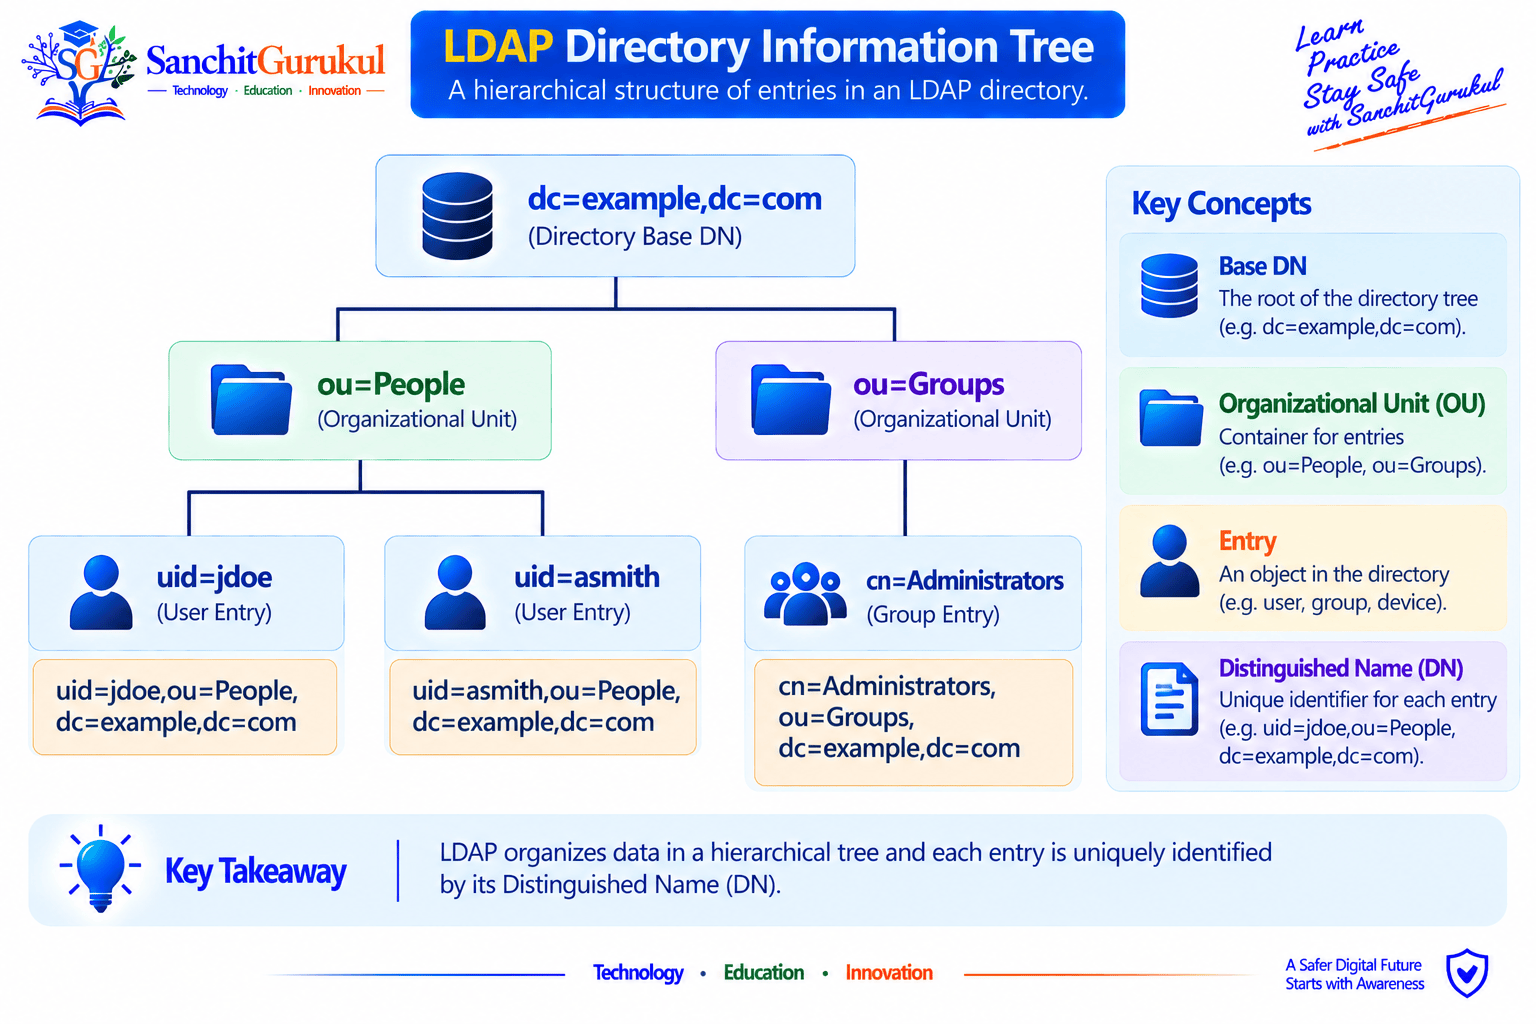
Directory Information Tree
LDAP information is organized in a:
Directory Information Tree, or DIT.
The hierarchy can represent structures such as:
- Organizations
- Departments
- Users
- Groups
- Devices
- Geographic locations
A typical directory may use:
dc=example,dc=com
as its base.
Below that could be containers such as:
ou=People
and:
ou=Groups
LDAP Entry
An LDAP entry represents an object in the directory.
For example, a user entry may contain:
dn: uid=jdoe,ou=People,dc=example,dc=com
objectClass: inetOrgPerson
uid: jdoe
cn: John Doe
sn: Doe
mail: john.doe@example.com
This entry represents one directory object.
Distinguished Name
Every LDAP entry has a Distinguished Name, or DN.
Example:
uid=jdoe,ou=People,dc=example,dc=comThe DN uniquely identifies the entry within the directory tree.
Relative Distinguished Name
The portion identifying the entry relative to its parent is called the:
Relative Distinguished Name, or RDN.
For the previous example:
uid=jdoeis the RDN.
Common DN Components
| Attribute | Meaning | Example |
|---|---|---|
dc |
Domain Component | dc=example |
ou |
Organizational Unit | ou=People |
cn |
Common Name | cn=John Doe |
uid |
User Identifier | uid=jdoe |
Attributes
Entries contain attributes.
For example:
cn: John Doe
sn: Doe
mail: john.doe@example.com
telephoneNumber: +1-555-0100
Some attributes may contain multiple values.
Object Classes
The objectClass attribute determines which object classes apply to an entry.
Object classes define which attributes are:
- Required
- Allowed
- Structurally appropriate
For example:
objectClass: top
objectClass: person
objectClass: organizationalPerson
objectClass: inetOrgPerson
LDAP Schema
The schema defines rules for directory information.
It describes:
- Attribute types
- Object classes
- Matching rules
- Attribute syntax
- Naming constraints
The schema prevents arbitrary incompatible data from being added to the directory.
How LDAP Works: Bind, Search, Filters and TLS
LDAP follows a client-server model.
An LDAP client connects to a directory server and performs operations against directory entries.
Common LDAP Operations
Important LDAP operations include:
| Operation | Purpose |
|---|---|
| Bind | Establish authentication state |
| Search | Find directory entries |
| Compare | Compare an attribute with a value |
| Add | Create an entry |
| Modify | Change attributes |
| Delete | Remove an entry |
| Modify DN | Rename or move an entry |
| Unbind | End the LDAP session |
| Abandon | Request cancellation of an operation |
| Extended Operation | Add protocol extensions such as StartTLS |
Bind
A Bind changes the authentication state of an LDAP connection.
LDAP supports multiple authentication approaches.
Anonymous Bind
No authenticated identity is established.
Whether anonymous users can read directory information depends on server configuration and access controls.
Simple Bind
A name and password are supplied.
Conceptually:
Bind DN: uid=jdoe,ou=People,dc=example,dc=com
Password: User password
Simple Bind credentials must be protected using TLS or another suitable confidentiality mechanism.
Sending username/password authentication without appropriate transport protection creates a serious security risk.
SASL Bind
LDAP can also use the Simple Authentication and Security Layer, or SASL.
Depending on the environment, SASL mechanisms can integrate technologies such as:
- Kerberos
- GSSAPI
- Client certificates
- Other authentication mechanisms
Search
Search is one of the most commonly used LDAP operations.
An LDAP search normally specifies:
- Server
- Base DN
- Search scope
- Search filter
- Requested attributes
Search Scope
Common search scopes include:
| Scope | Meaning |
|---|---|
| Base | Search only the specified entry |
| One Level | Search immediate children |
| Subtree | Search the base and descendants |
LDAP Search Filters
LDAP filters use a standardized syntax.
Find a user by UID:
(uid=jdoe)Find all person objects:
(objectClass=person)Combine conditions:
(&(objectClass=inetOrgPerson)(uid=jdoe))OR search:
(|(uid=jdoe)(uid=asmith))LDAP Ports
Two ports are commonly encountered:
| Port | Typical Use |
|---|---|
| TCP 389 | LDAP; can be upgraded using StartTLS |
| TCP 636 | LDAP with TLS from connection establishment, commonly called LDAPS |
Port 389 does not necessarily mean that the entire session remains unencrypted.
A client can connect and then issue:
StartTLS
to establish TLS protection before credentials or sensitive directory information are exchanged.
Port 636 normally establishes TLS immediately.
Test an LDAP Bind
OpenLDAP client utilities include ldapwhoami.
Example using StartTLS:
ldapwhoami -x
-H ldap://ldap.example.com
-ZZ
-D "uid=jdoe,ou=People,dc=example,dc=com"
-W
-W prompts for the password instead of placing it directly on the command line.
Search with ldapsearch
ldapsearch -LLL -x
-H ldap://ldap.example.com
-ZZ
-D "uid=jdoe,ou=People,dc=example,dc=com"
-W
-b "dc=example,dc=com"
"(uid=jdoe)" cn mail
Important options:
| Option | Purpose |
|---|---|
-H |
LDAP server URI |
-D |
Bind DN |
-W |
Prompt for password |
-b |
Search Base DN |
-x |
Use simple authentication |
-ZZ |
Require successful StartTLS |
-LLL |
Produce cleaner LDIF-style output |
A result might resemble:
dn: uid=jdoe,ou=People,dc=example,dc=com
cn: John Doe
mail: john.doe@example.com
LDAP Authentication, Active Directory and Common Use Cases
LDAP is widely used in identity environments, but its role needs to be understood correctly.
Application Authentication
A common enterprise application can:
- Connect to the LDAP server using a service account.
- Search for the user’s directory entry.
- Determine the user’s DN.
- Attempt authentication using the user’s credentials.
- Retrieve authorized directory attributes.
The exact workflow depends on the application and directory product.
Central Directory Lookup
Applications can query LDAP for information such as:
- Username
- Email address
- Group membership
- Department
- Employee identifier
- Telephone number
Network Device Administration
Firewalls, routers, VPN gateways, and other appliances may query LDAP or Active Directory for:
- Administrator authentication
- Group membership
- User lookup
However, RADIUS or TACACS+ may be more appropriate when device access requires network-specific authorization and accounting capabilities.
LDAP and Active Directory
It is misleading to describe this as:
LDAP vs Active Directory
They are not equivalent technologies.
LDAP is a protocol.
Active Directory Domain Services is a directory service.
AD DS supports LDAP for accessing directory information but also uses technologies such as:
- Kerberos
- NTLM
- DNS
- Group Policy
- Directory replication
Windows domain authentication should therefore not be described simply as “LDAP authentication.”
LDAP and Single Sign-On
LDAP by itself does not provide modern web SSO.
It may provide the identity directory behind an authentication system.
SSO may instead use technologies such as:
- Kerberos
- SAML
- OpenID Connect
For example, an identity provider may retrieve users and groups from LDAP while using SAML or OpenID Connect to authenticate users to applications.
LDAP Compared with Related Technologies
| Technology | Primary Role |
|---|---|
| LDAP | Access and manage directory information |
| Active Directory | Microsoft enterprise directory service |
| Kerberos | Ticket-based authentication protocol |
| RADIUS | Network-access AAA protocol |
| SAML | Federated authentication / SSO |
| OAuth 2.0 | Delegated authorization framework |
| OpenID Connect | Authentication layer built on OAuth 2.0 |
These technologies are frequently integrated rather than mutually exclusive.
Typical LDAP Use Cases
LDAP remains useful for:
- Enterprise user directories
- Application authentication backends
- Employee directories
- Unix/Linux identity integration
- Network-device user lookup
- Group membership lookup
- Address books
- Service-account directories
- Legacy enterprise applications
- Active Directory integrations
LDAP Security and Deployment Best Practices
Directory systems can contain highly sensitive information.
Security must therefore include both transport protection and authorization.
Encrypt LDAP Connections
Do not send simple Bind passwords across an unprotected network.
Use:
- StartTLS
- LDAP over TLS
- Suitable SASL protection
according to the directory product and architecture.
Validate Server Certificates
Encryption is not sufficient if the client accepts any certificate.
LDAP clients should validate:
- Certificate chain
- Server identity
- Validity period
- Trusted issuing CA
Do not disable certificate verification simply to make an LDAP integration work.
Use Least-Privilege Bind Accounts
Applications frequently use a service account to search the directory.
That account should receive only the permissions required by the application.
For example, a web application may need permission to read:
uidcnmail- Group membership
It generally does not need permission to:
- Modify users
- Change passwords
- Read sensitive credential attributes
- Administer the directory
LDAP Does Not Define a Universal ACL Model
LDAP provides protocol operations and security mechanisms, but it does not define one standardized access-control implementation for every LDAP server.
Directory products implement their own authorization mechanisms.
Examples include:
- OpenLDAP ACLs
- Red Hat Directory Server ACIs
- Active Directory security descriptors and ACLs
Always follow the security model of the directory platform being deployed.
Restrict Anonymous Access
Anonymous LDAP access may be required in specific environments, but unnecessary anonymous directory browsing should be restricted.
Review which:
- Entries
- Attributes
- Search operations
can be accessed without authentication.
Protect LDAP Search Filters
Applications must not concatenate untrusted user input directly into LDAP filters.
For example, an application should not blindly construct:
(uid=)Special LDAP filter characters must be safely escaped according to LDAP filter syntax.
Use the LDAP library’s appropriate escaping or filter-building functions.
This helps prevent LDAP injection and unexpected directory searches.
Secure Active Directory LDAP
In Active Directory environments, evaluate Microsoft’s security guidance for:
- LDAP signing
- LDAP channel binding
- Secure LDAP
- Simple Bind restrictions
LDAP signing protects message integrity for supported SASL LDAP sessions.
Channel binding can bind authentication to the underlying TLS channel in supported scenarios.
Protect Administrative Accounts
Directory administrator credentials are extremely sensitive.
Use:
- Separate administration accounts
- Strong authentication
- Restricted management networks
- Least privilege
- Audit logging
- Secure management protocols
Applications should not normally use the directory’s root or domain-administrator account as their service Bind identity.
Plan Availability and Replication
Directory services frequently support critical authentication and application services.
Design for:
- Multiple directory servers
- Replication
- DNS availability
- Monitoring
- Configuration backup
- Directory data backup
- Restore testing
A highly secure LDAP server is still an operational problem if every application fails whenever that single server becomes unavailable.
LDAP Administration and Troubleshooting
LDAP problems are easiest to resolve when each layer is tested separately.

Step 1 — Verify DNS
Check that the LDAP server name resolves correctly.
getent hosts ldap.example.comStep 2 — Check TLS on Port 636
openssl s_client
-connect ldap.example.com:636
-servername ldap.example.com
Check:
- Certificate subject
- Subject Alternative Name
- Issuing CA
- Expiration
- Verification result
Step 3 — Check StartTLS
openssl s_client
-connect ldap.example.com:389
-starttls ldap
-servername ldap.example.com
This helps determine whether the server supports a valid LDAP StartTLS negotiation.
Step 4 — Test Bind Independently
ldapwhoami -x
-H ldap://ldap.example.com
-ZZ
-D "uid=jdoe,ou=People,dc=example,dc=com"
-W
If authentication fails here, fix the Bind problem before troubleshooting the application.
Step 5 — Verify the Base DN
A common problem is using the wrong search base.
For example:
dc=example,dc=comis different from:
ou=People,dc=example,dc=comThe second limits the search to the People subtree.
Step 6 — Verify the Filter
Test the exact filter independently.
ldapsearch -LLL -x
-H ldap://ldap.example.com
-ZZ
-D "cn=app-reader,ou=Services,dc=example,dc=com"
-W
-b "ou=People,dc=example,dc=com"
"(uid=jdoe)"
If no entry is returned, investigate:
- Wrong attribute
- Wrong username
- Wrong Base DN
- Search scope
- Incorrect filter
- Access-control restrictions
Step 7 — Check Access Controls
Successful authentication does not guarantee permission to search or modify directory information.
A service account may successfully Bind but still be unable to read an attribute.
Check the directory server’s:
- ACL
- ACI
- Security descriptor
- Attribute permissions
depending on the product.
LDAP Modify Example
LDAP modifications are commonly represented using LDIF, or LDAP Data Interchange Format.
Example:
dn: uid=jdoe,ou=People,dc=example,dc=com
changetype: modify
replace: mail
mail: john.doe@example.com
Save it as:
update-mail.ldif
Then apply it with an authorized account:
ldapmodify -x
-H ldap://ldap.example.com
-ZZ
-D "cn=Directory Manager"
-W
-f update-mail.ldif
Use an account with only the permissions required for the change.
Common LDAP Failure Patterns
| Symptom | Likely Areas to Check |
|---|---|
| Connection refused | Server, port, listener, firewall |
| Timeout | Routing, ACL, firewall, wrong address |
| TLS certificate error | CA trust, hostname, expiration |
| Invalid credentials | Bind DN, password, auth method |
| No search results | Base DN, filter, scope, ACL |
| Insufficient access | Directory permissions |
| Works with IP but not hostname | DNS |
| Application fails but ldapsearch works | Application mapping/configuration |
| StartTLS fails | Server TLS config, certificate, client trust |
Key Takeaways and Summary
Key Takeaways
- LDAP is a protocol for accessing distributed directory services; it is not the directory database itself.
- The current protocol family is commonly called LDAPv3.
- LDAP directory information is organized as a hierarchical Directory Information Tree.
- Every directory entry has a Distinguished Name that uniquely identifies it.
- Object classes and schema control what information an entry can contain.
- Common LDAP operations include Bind, Search, Compare, Add, Modify, Delete and Modify DN.
- LDAP commonly uses TCP 389, while LDAP over TLS commonly uses TCP 636.
- StartTLS can upgrade an LDAP connection on port 389 to TLS.
- Simple password Bind should not be used without suitable confidentiality protection.
- LDAP and Active Directory are not competing equivalents—AD DS is a directory service that supports LDAP.
- LDAP alone does not provide modern SSO; it can serve as an identity source for SSO systems.
- LDAP does not define one universal access-control implementation.
- Application Bind accounts should follow least-privilege principles.
- User input used in LDAP filters must be safely escaped to prevent LDAP injection.
- Effective troubleshooting should validate DNS, connectivity, TLS, Bind, Base DN, filters and authorization separately.
Summary
LDAP remains one of the most important protocols for enterprise identity and directory integration.
Its core purpose is straightforward:
Provide a standardized way for clients to search, retrieve and modify structured directory information.
A typical LDAP architecture contains:
- Directory entries
- Distinguished Names
- Attributes
- Object classes
- Schema
- LDAP clients
- LDAP servers
- Authentication mechanisms
- Access-control policies
Applications can use LDAP to retrieve users and groups, perform directory lookups, and participate in authentication workflows.
However, secure LDAP deployment requires more than simply opening TCP port 389.
Administrators should:
- Protect credentials with TLS.
- Validate certificates.
- Restrict anonymous access.
- Use least-privilege service accounts.
- Secure search filters.
- Apply directory-specific ACLs.
- Maintain replication and backups.
- Monitor authentication and directory changes.
The most important distinction to remember is:
LDAP provides the language and operations used to communicate with a directory service; the directory platform determines how the information is stored, replicated, authorized and administered.
Understanding that distinction makes LDAP integrations with Linux, Active Directory, firewalls, applications, VPN systems and enterprise identity platforms much easier to design and troubleshoot.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


