
Network Address Translation can be implemented in different ways depending on how many internal systems need translation, how many translated addresses are available, and whether a predictable address mapping is required.
Three important NAT models are:
- Static NAT
- Dynamic NAT
- PAT
They all translate network addressing information, but they solve different problems.
Static NAT normally creates a predictable mapping.
Dynamic NAT normally selects a translated address from an available pool.
PAT allows many connections to share one or a small number of translated addresses by also using port information.
Understanding the Three NAT Models
Static NAT
Static NAT creates a consistent mapping between an original address and a translated address.
For example:
Original Address
10.10.10.50
Translated Address
203.0.113.50
Whenever the relevant NAT rule applies, the system uses the same mapping.
Static NAT is useful when another system needs to consistently identify the device by the same translated address.
Dynamic NAT
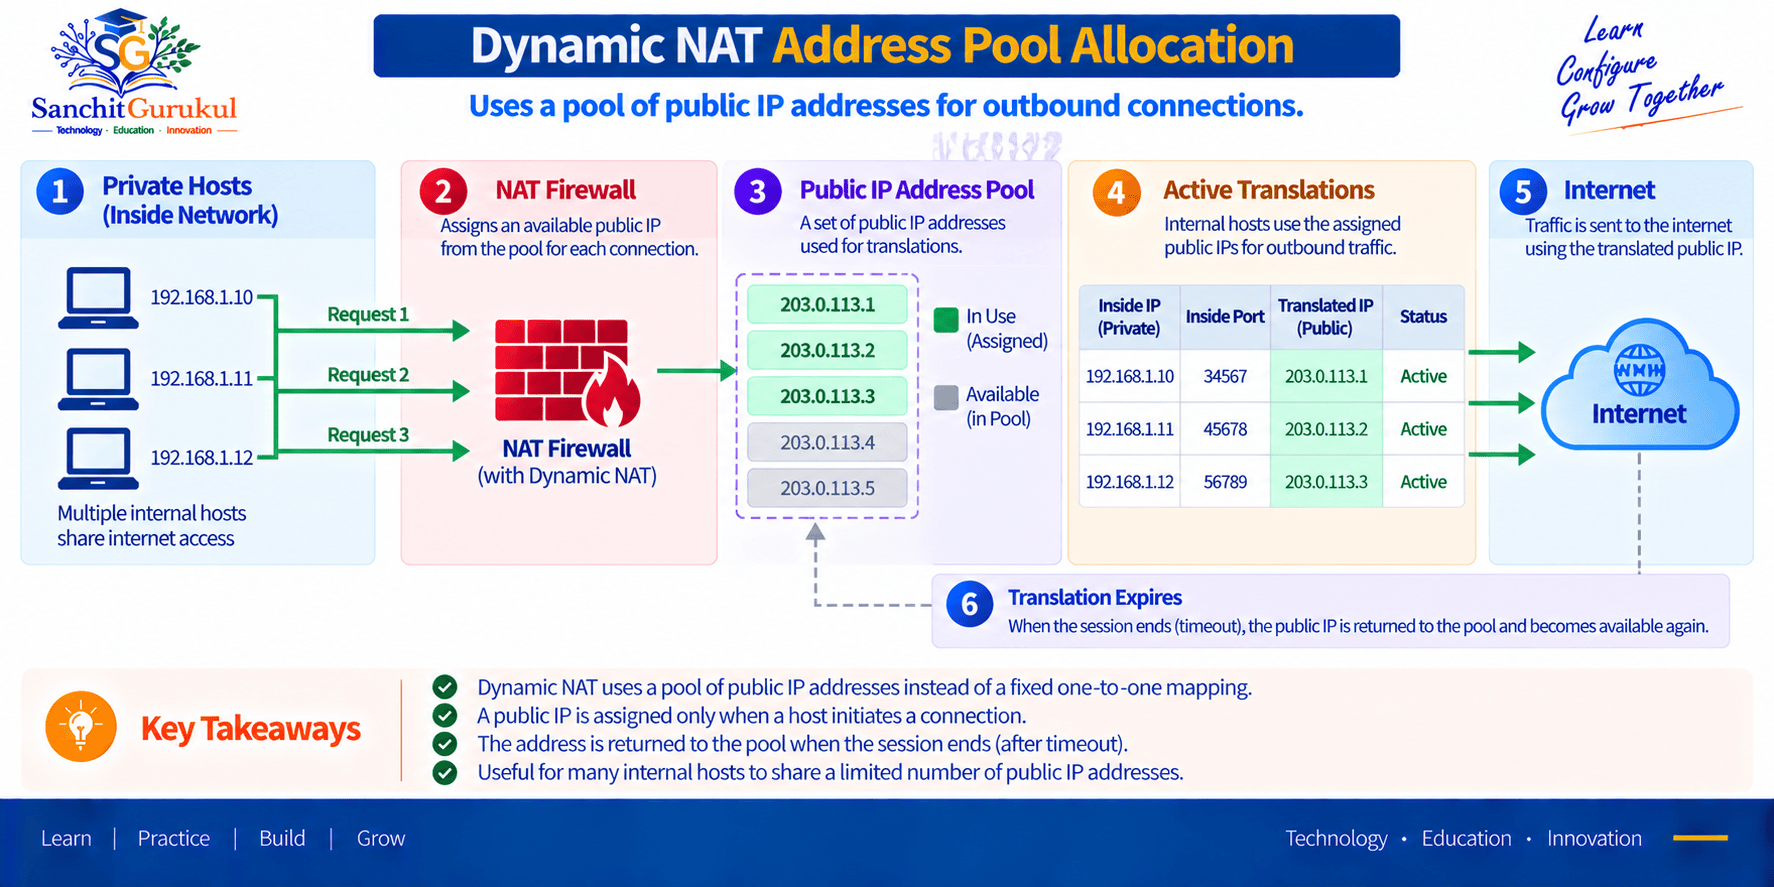
Dynamic NAT uses a pool of translated addresses.
For example:
Internal network:
10.10.10.0/24
Translation pool:
203.0.113.100 – 203.0.113.110
When an internal system creates a matching connection, the NAT device assigns an available address from the pool.
The same internal host may not always receive the same translated address.
PAT
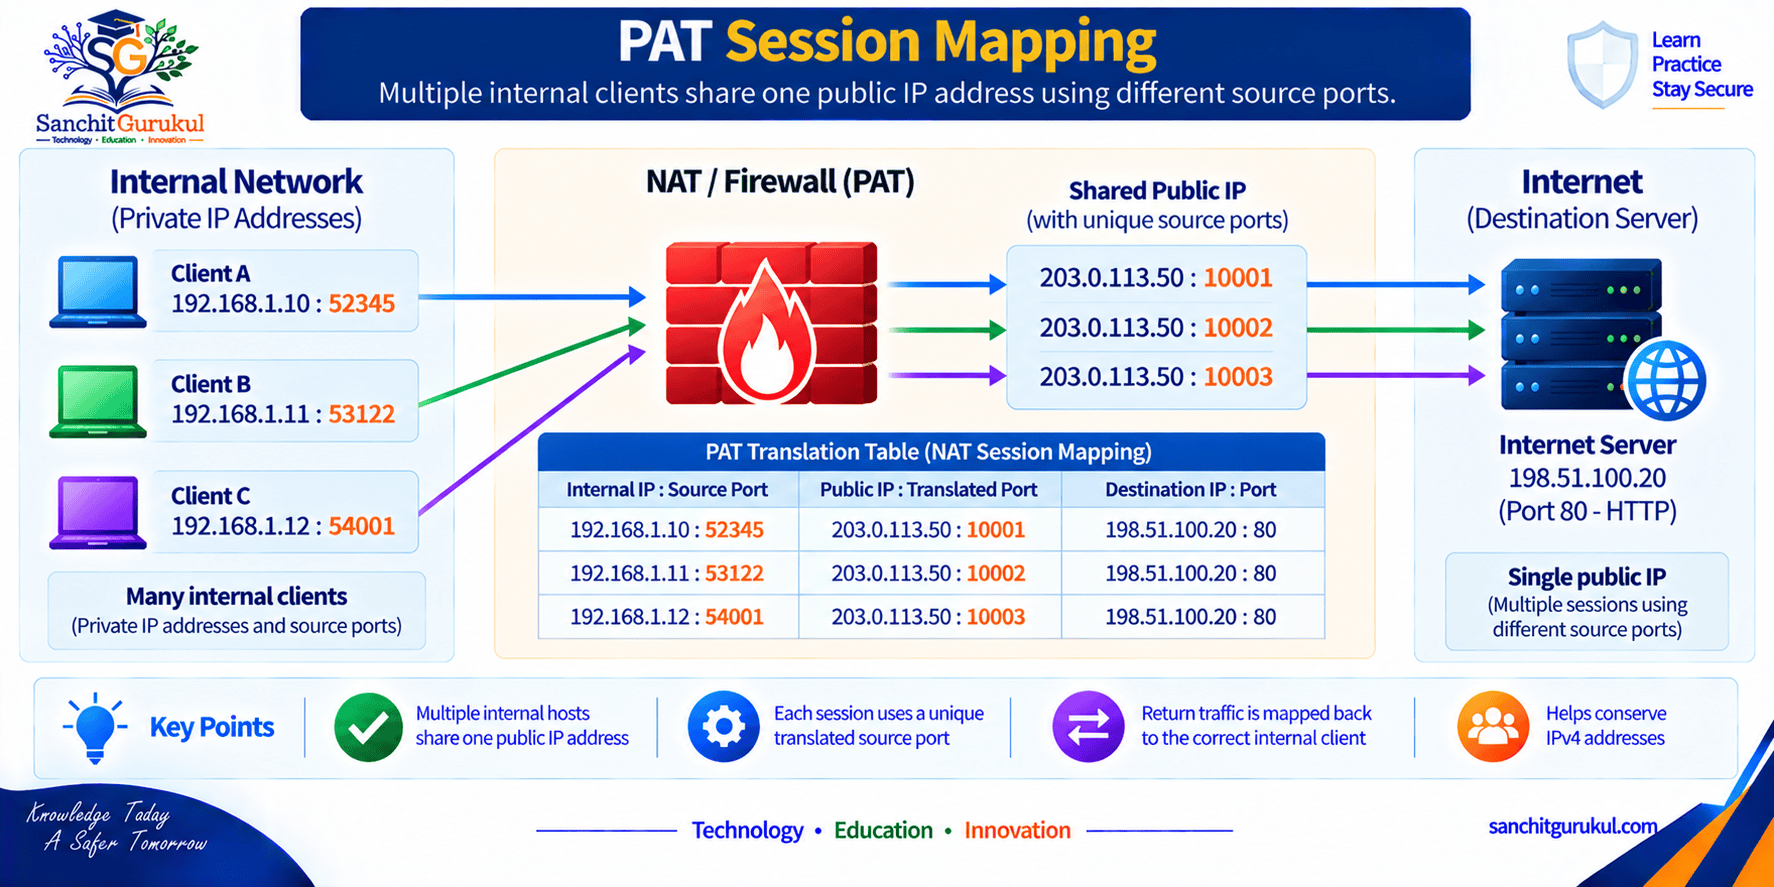
PAT, or Port Address Translation, allows multiple sessions to share a translated IP address.
The NAT device distinguishes sessions using transport-layer port information.
For example:
10.10.10.25:51001
may become:
203.0.113.10:40001
while:
10.10.10.26:51001
may become:
203.0.113.10:40002
Both connections use the same public IP but have different translated ports.

The Important Question
The best way to distinguish these models is to ask:
How is the translated address assigned?
Static NAT:
The mapping is predetermined.
Dynamic NAT:
The address is selected from a pool.
PAT:
Address translation is combined with port translation so the same translated IP can support many simultaneous sessions.
How Static and Dynamic NAT Work
Static NAT Operation
Suppose an internal application server has:
10.10.20.50
A partner organization expects connections from:
172.20.50.50
The firewall can create a static source translation so the internal server consistently appears as:
172.20.50.50
This gives the partner a predictable address to permit.
Common Static NAT Uses
Static NAT may be useful for:
- Partner connectivity
- Published applications
- Network migrations
- Overlapping networks
- Devices requiring fixed translated identities
- Certain bidirectional translation designs
Static Does Not Always Mean Internet Public IP
Static NAT is often demonstrated using private-to-public translation, but that is only one use case.
A fixed translation can also occur between:
- Two private networks
- Business partners
- Data centers
- Cloud environments
- Overlapping address spaces
Dynamic NAT Operation
Dynamic NAT does not normally reserve one translated address permanently for every internal host.
Instead, an address is allocated when needed.
Example pool:
203.0.113.100
through:
203.0.113.109
An internal system starts a connection.
The NAT device chooses an available public address.
When the translation is no longer required and its state expires, the address can return to the available pool.
What Happens When the Dynamic NAT Pool Is Full?
Suppose the pool contains ten translated addresses.
If each active translation requires one address and all ten are already allocated, another host may not receive a translation.
The exact behavior depends on the implementation, but the new connection may fail until an address becomes available.
This is one reason address-pool sizing matters.
How PAT Supports Large Numbers of Sessions
Why PAT Is So Common
Public IPv4 addresses are limited.
Giving every internal user a separate public address would be inefficient for ordinary Internet access.
PAT allows many users to share a single public IP or a small group of public IPs.
Address and Port Translation
Consider three users accessing the same HTTPS server.
| Original Source | Translated Source |
|---|---|
10.10.10.25:51000 |
203.0.113.10:40001 |
10.10.10.26:51000 |
203.0.113.10:40002 |
10.10.10.27:52000 |
203.0.113.10:40003 |
The destination might be the same:
198.51.100.20:443
The firewall uses the translated source port to maintain unique session mappings.
Return Traffic
When the server replies to:
203.0.113.10:40002
the firewall identifies that the response belongs to:
10.10.10.26:51000
It then performs reverse translation.
PAT and Session Scale
PAT can support many simultaneous connections, but it is not unlimited.
Available resources can depend on:
- Number of translated IP addresses
- Available transport-layer ports
- Protocol behavior
- Session timeout
- NAT implementation
- Firewall capacity
Large environments must therefore consider translation scale.
Port Exhaustion
A translated address has a finite port space available for transport-layer session mappings.
If a very large number of sessions compete for the same translation resources, the system can experience port exhaustion.
Symptoms may include:
- New Internet sessions fail
- Existing sessions continue working
- Some users are affected intermittently
- NAT allocation errors appear in logs
Increasing PAT Capacity
Depending on the platform, capacity may be increased by:
- Adding more translated IP addresses
- Using a larger address pool
- Adjusting architecture
- Reviewing session timeouts
- Distributing traffic across additional gateways
Changes should be based on actual resource usage rather than arbitrary timeout reduction.
Comparing Use Cases and Design Choices
Static NAT vs Dynamic NAT vs PAT
| Feature | Static NAT | Dynamic NAT | PAT |
|---|---|---|---|
| Address Assignment | Predetermined | Selected from a pool | Shared with port mapping |
| Mapping Predictability | High | Lower | Session dependent |
| Public Address Usage | Higher | Pool dependent | Very efficient |
| Port Translation Required | Not necessarily | Not necessarily | Yes, commonly |
| Typical Scale | Individual systems | Groups of systems | Large numbers of sessions |
| Common Internet User Access | Possible but inefficient | Possible | Very common |
| Partner Whitelisting | Very useful | Less predictable | Depends on design |
| Risk of Pool Exhaustion | Low for fixed mapping | Yes | Address/port resource exhaustion possible |
When Static NAT Is Appropriate
Use static NAT when a predictable translated identity is required.
Examples:
- Partner whitelisting
- Fixed server mappings
- Application dependencies
- Network migration
- Overlapping network integration
When Dynamic NAT Is Appropriate
Dynamic NAT can be useful when:
- Several translated addresses are available
- Predictable mappings are unnecessary
- Users can share a temporary public address pool
- Port sharing is not required for the design
When PAT Is Appropriate
PAT is commonly appropriate for:
- Employee Internet access
- Home Internet access
- Branch office egress
- Cloud workload egress
- Large groups of private hosts

Combining NAT Techniques
Enterprise firewalls can use several NAT techniques at the same time.
For example:
Employees
Use PAT for Internet access.
Application Server
Uses static source NAT for partner communication.
Public Web Server
Uses destination NAT.
VPN Traffic
Uses no translation or a specialized VPN NAT rule.
A firewall is therefore rarely limited to one NAT method.
Common Problems and Troubleshooting
Static NAT Problems
Common issues include:
- Wrong fixed mapping
- Duplicate translated address
- Routing problem
- Firewall policy mismatch
- Return traffic bypassing the NAT device
Dynamic NAT Pool Exhaustion
If a dynamic pool contains insufficient addresses, new translations may fail.
Check:
- Pool size
- Active mappings
- Translation timeouts
- Usage patterns
- NAT logs
PAT Port Exhaustion
When users report intermittent failures but existing sessions remain stable, check:
- Active PAT sessions
- Port utilization
- Translation pool size
- NAT allocation failures
- Session growth
Wrong NAT Rule Matches
A broad PAT rule can sometimes capture traffic that should use a static or no-NAT rule.
For example:
Rule 1
All internal traffic to any destination
Use PAT
Rule 2
Application server to partner network
Use static NAT
If the firewall’s processing logic causes the broad rule to take precedence, the partner may see the wrong source address.
The exact rule-order behavior depends on the platform.
Practical Troubleshooting Example
Verify the Translation Table
Useful information includes:
- Original source
- Translated source
- Original port
- Translated port
- Destination
- Protocol
- NAT rule
- Session state
- Creation time
- Packet counters
Troubleshooting Workflow

Troubleshooting Questions
Ask:
- Which NAT type should be used?
- Which NAT rule actually matched?
- What original address was seen?
- What translated address was allocated?
- Was a port also translated?
- Is the translation pool available?
- Is PAT capacity available?
- Is routing correct?
- Does firewall policy permit the traffic?
- Does return traffic come back through the same NAT device?
Key Takeaways and Summary
Key Takeaways
- Static NAT provides a predictable translation mapping.
- Dynamic NAT assigns translated addresses from an available pool.
- PAT allows many sessions to share translated IP addresses by using port mappings.
- Static NAT is useful when another network requires a consistent translated identity.
- Dynamic NAT requires enough available addresses in its translation pool.
- PAT is widely used for large-scale private-to-Internet connectivity.
- PAT resources are finite and can experience port exhaustion.
- Different NAT methods can operate simultaneously on the same firewall.
- NAT rule order and matching are important in complex configurations.
- Troubleshooting should verify both the expected translation method and the actual translation created by the device.
Summary
Static NAT, dynamic NAT, and PAT provide different methods of allocating translated addressing information.
Static NAT creates a consistent mapping and is useful when an application, business partner, or network architecture requires a predictable translated address.
Dynamic NAT assigns translated addresses from a pool as connections require them. This provides more flexibility but depends on having enough available addresses.
PAT provides greater IPv4 efficiency by allowing many simultaneous sessions to share translated addresses. It does this by maintaining unique port mappings for individual connections.
The appropriate NAT method therefore depends on whether the design requires predictability, address-pool allocation, or large-scale address sharing.
When troubleshooting, do not stop after confirming that a NAT rule exists. Verify the actual rule match, allocated address, translated port where applicable, resource availability, routing, firewall policy, and return path.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


