
IPv6, or Internet Protocol version 6, is the current Internet Protocol designed as the successor to IPv4.
One of the primary reasons IPv6 was developed was the limited IPv4 address space.
IPv4 uses:
32-bit addresses
which provides approximately:
4.3 billion possible addresses
IPv6 uses:
128-bit addresses
which provides approximately:
3.4 × 10³⁸ possible addresses
This much larger address space allows networks to allocate addresses and subnets without the extreme address-conservation practices commonly associated with IPv4.
IPv6 also introduces or expands capabilities such as:
- Hierarchical address allocation
- Stateless Address Autoconfiguration
- Neighbor Discovery
- Multicast-based network functions
- Anycast addressing
- Simplified base-header processing
- More scalable subnet planning
- Reduced dependence on traditional IPv4 NAT
However, IPv6 should not be considered automatically faster or more secure than IPv4.
Its security and performance still depend on:
- Network design
- Firewall policy
- Routing
- Endpoint security
- Application security
- Monitoring
- Operational practices
Understanding IPv6 Address Format
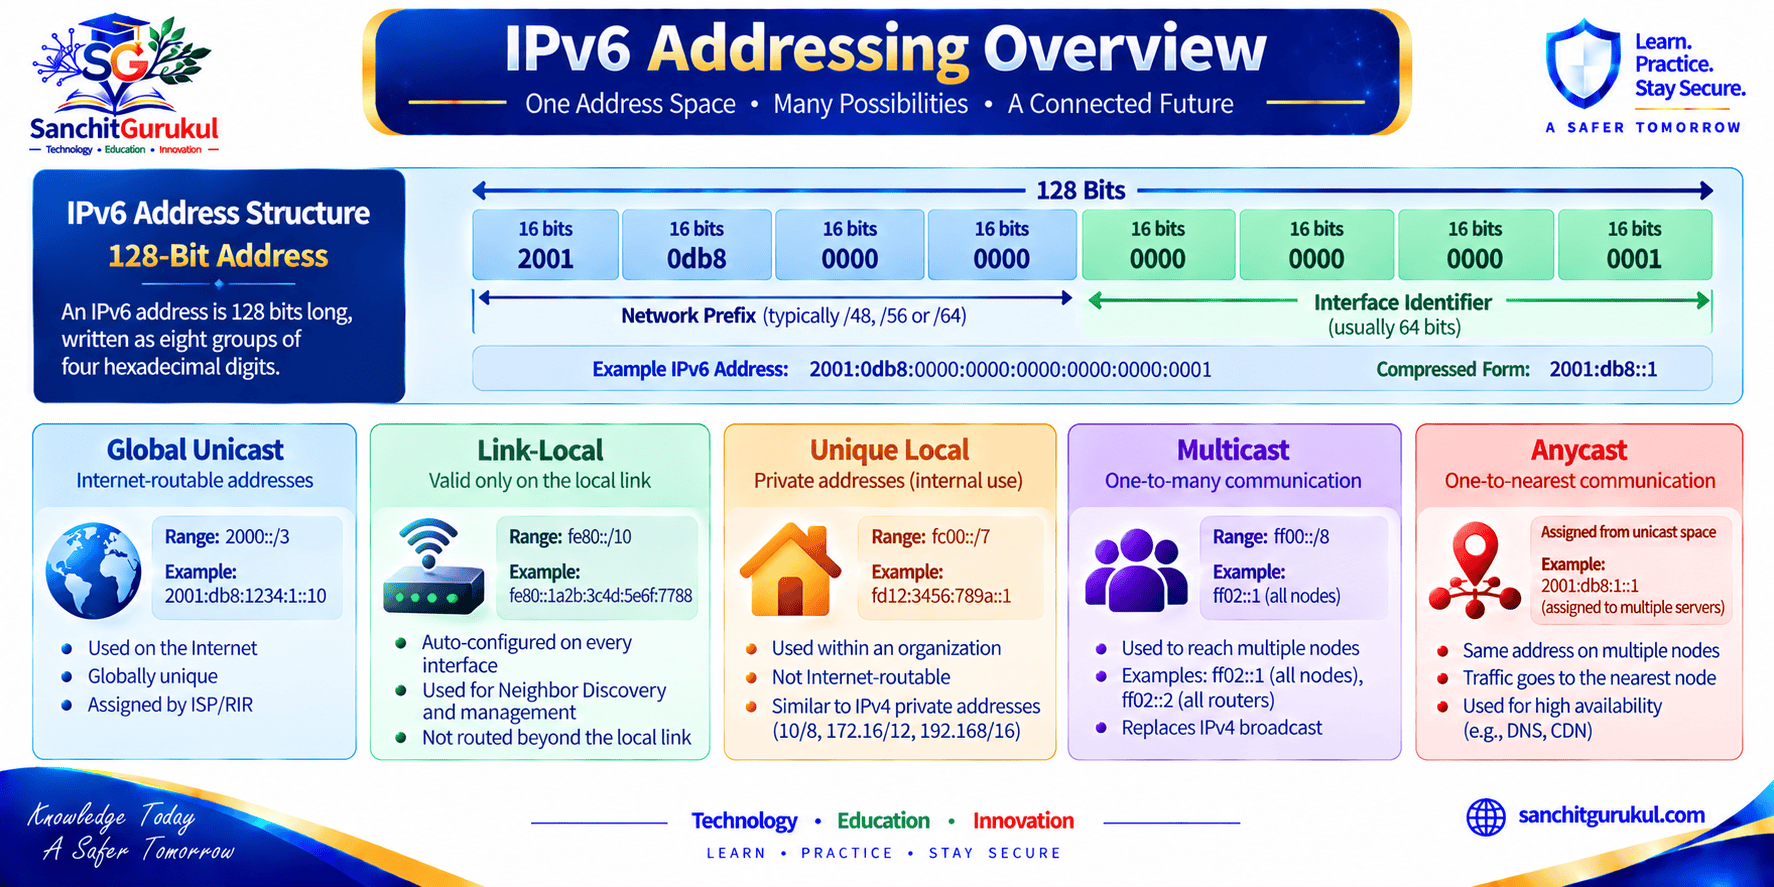
An IPv6 address contains:
128 bits
These bits are normally represented as eight groups of four hexadecimal digits.
Each group contains:
16 bits
A full address may look like:
2001:0db8:85a3:0000:0000:8a2e:0370:7334Each hexadecimal digit represents four binary bits.
Eight 16-Bit Groups
The address can be viewed as:
2001 : 0db8 : 85a3 : 0000 : 0000 : 8a2e : 0370 : 7334Eight groups multiplied by 16 bits gives:
128 bits
Removing Leading Zeros
Leading zeros within each group can be omitted.
For example:
2001:0db8:0000:0000:0000:0000:0000:0025can become:
2001:db8:0:0:0:0:0:25Using :: Zero Compression
One continuous sequence of zero groups can be replaced with:
::Therefore:
2001:db8:0:0:0:0:0:25can become:
2001:db8::25:: Can Be Used Only Once
Consider:
2001:db8::10::25This is invalid because the receiver could not determine how many zero groups belong to each compressed section.
Only one :: compression may appear in an IPv6 address.
IPv6 Prefix Length
IPv6 uses CIDR-style prefix notation.
Example:
2001:db8:1234:100::/64The:
/64
means that the first 64 bits identify the subnet prefix.
For ordinary IPv6 LANs, /64 is the standard and widely used subnet size.
Documentation Addresses
The prefix:
2001:db8::/32is reserved for documentation and examples.
Addresses from this range should not be used as real production Internet addresses.
Major Types of IPv6 Addresses
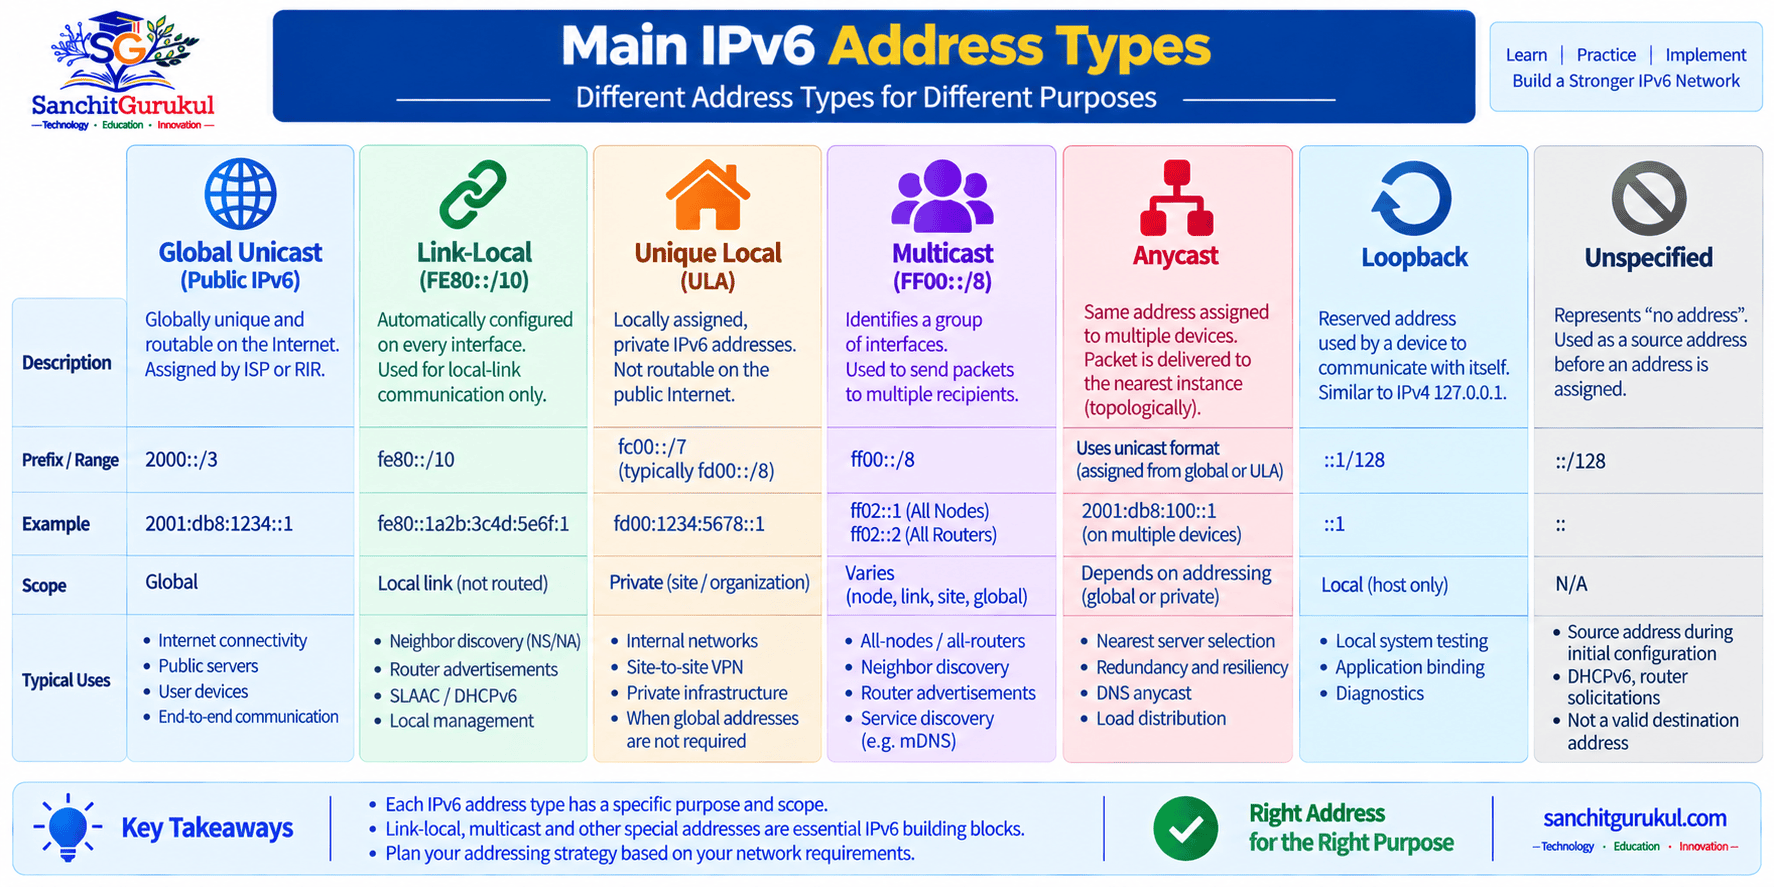
IPv6 defines three fundamental address types:
- Unicast
- Anycast
- Multicast
Within unicast addressing, several important address scopes and special-purpose addresses exist.
Unicast
A unicast address identifies one interface.
Traffic sent to a unicast address is delivered to that interface.
Important forms include:
Global Unicast
Global Unicast Addresses are used for globally routable IPv6 communication.
An example using the documentation prefix is:
2001:db8:1234:10::25A global unicast address commonly contains hierarchical information such as:
- Global routing prefix
- Subnet information
- Interface identifier
This structure supports scalable address planning and route aggregation.
Link-Local
IPv6 link-local addresses use:
fe80::/10Example:
fe80::21a:2bff:fe3c:4d5eLink-local addresses are valid only on the local link.
Routers do not forward normal link-local traffic between different links.
Link-local addresses are important for IPv6 operations including:
- Neighbor Discovery
- Router Discovery
- Routing protocol relationships
- Local next-hop communication
An IPv6 interface can therefore have both:
- Link-local address
- Global or other unicast addresses
at the same time.
Unique Local Addresses
Unique Local Addresses use:
fc00::/7Locally generated ULA prefixes normally appear under:
fd00::/8ULA addresses are intended for local or organizational communication and are not intended to be globally routed across the public Internet.
Example:
fd12:3456:789a:10::25ULAs may be useful for:
- Internal services
- Private inter-site communication
- Infrastructure that does not require direct Internet addressing
Loopback
IPv6 loopback is:
::1/128It performs a role similar to IPv4:
127.0.0.1Unspecified Address
The all-zero IPv6 address is:
::/128It represents the unspecified address.
It may be used temporarily by a node before it has an appropriate usable address.
It is not a normal destination address.
Multicast
IPv6 multicast addresses begin with:
ff00::/8A multicast address identifies a group of interfaces.
Traffic is delivered to members of that multicast group.
Common examples include:
All Nodes on the Local Link
ff02::1All Routers on the Local Link
ff02::2IPv6 makes extensive use of multicast for functions such as Neighbor Discovery.
IPv6 Has No Broadcast Address
IPv4 uses broadcast for several network operations.
IPv6 removes broadcast addressing and uses multicast instead.
This avoids forcing every device on a network segment to process traffic intended only for a specific group.
Anycast
An IPv6 anycast address is assigned to more than one interface, normally on different systems or locations.
Routing delivers traffic to one instance according to routing topology.
Anycast is useful for distributed services such as:
- DNS
- Content platforms
- Distributed infrastructure
- Globally replicated services
Unlike multicast, anycast does not have a unique visible address format.
Anycast addresses come from unicast address space and are distinguished by how they are configured and routed.
| Address Type | Example | Typical Purpose |
|---|---|---|
| Global Unicast | 2001:db8:10::25 |
Globally routed communication |
| Link-Local | fe80::1 |
Local-link communication |
| Unique Local | fd12:3456::1 |
Internal communication |
| Loopback | ::1 |
Local host |
| Unspecified | :: |
No address yet |
| Multicast | ff02::1 |
Group communication |
| Anycast | Uses unicast format | Reach one of several service instances |
How IPv6 Addresses Are Assigned and Used
IPv6 addresses can be configured through several mechanisms.
Static Addressing
Infrastructure such as:
- Servers
- Routers
- Firewalls
- Load balancers
may use manually assigned IPv6 addresses.
Example:
2001:db8:100:10::20/64Static addressing makes infrastructure addresses predictable for:
- DNS
- Monitoring
- Management
- Firewall policy
Stateless Address Autoconfiguration
IPv6 supports:
SLAAC — Stateless Address Autoconfiguration
A host can learn prefix information from IPv6 Router Advertisements and create an address for itself.
SLAAC can reduce the need to manually assign every endpoint address.
DHCPv6
IPv6 can also use:
DHCPv6
Depending on the deployment, DHCPv6 can provide:
- IPv6 address information
- DNS information
- Other configuration options
However, DHCPv6 does not normally provide the IPv6 default router.
Default-router discovery is performed through:
Router Advertisements
Duplicate Address Detection
Before most IPv6 unicast addresses become fully usable, IPv6 can perform:
Duplicate Address Detection — DAD
DAD helps determine whether another node on the same link is already using the address.
It is part of IPv6 Stateless Address Autoconfiguration behavior and uses Neighbor Discovery.
Interface Identifiers
Older IPv6 examples often show Interface Identifiers derived from the system’s MAC address using Modified EUI-64.
Modern systems should not be assumed to work this way.
Stable IPv6 addresses may use privacy-preserving interface identifier generation, while client operating systems can also use temporary addresses.
Temporary Privacy Addresses
Temporary addresses can periodically change the interface identifier used for outbound communication.
This reduces the ability to correlate activity over long periods based only on a stable IPv6 address.
They are especially useful for:
- User endpoints
- Mobile systems
- Client devices
Infrastructure servers generally benefit from predictable addresses.

Benefits and Practical Importance of IPv6
IPv6 brings several important benefits, but they should be described accurately.
Vast Address Space
The most obvious benefit is the 128-bit address space.
It allows organizations to design networks around:
- Sites
- VLANs
- Security zones
- Services
- Cloud environments
- Future growth
rather than conserving individual addresses as aggressively as IPv4 often requires.
Easier Hierarchical Address Planning
Large IPv6 allocations can be divided into structured prefix blocks.
For example:
Organization:
2001:db8:1234::/48

Headquarters:
2001:db8:1234:100::/56

HQ Users:
2001:db8:1234:101::/64

HQ Servers:
2001:db8:1234:110::/64
This hierarchy can support route aggregation and simplify troubleshooting.
Reduced Dependence on Traditional NAT
IPv6 provides enough address space for globally unique addressing without requiring IPv4-style address conservation through NAT.
This can simplify certain end-to-end communication designs.
However:
IPv6 does not prohibit address translation.
Translation technologies exist for specialized purposes.
More importantly:
Not using NAT does not mean permitting unrestricted inbound traffic.
Stateful firewalls remain essential.
Simplified IPv6 Base Header
The IPv6 base header has a fixed size of:
40 bytes
Several functions that were part of the IPv4 header are handled differently in IPv6, including through extension headers.
For example, routers along the path do not perform ordinary IPv6 fragmentation.
IPv6 fragmentation, when required, is performed by the source.
This can simplify some forwarding operations.
It does not mean:
IPv6 is always faster than IPv4.
Actual performance depends on:
- Routing path
- ISP connectivity
- DNS
- Application behavior
- Network equipment
- MTU
- Peering
Multicast Instead of Broadcast
IPv6 has no broadcast address type.
Multicast allows protocols to address relevant groups rather than automatically sending certain traffic to every node on the link.
Autoconfiguration
SLAAC can allow endpoints to create IPv6 addresses using information provided through Router Advertisements.
This can simplify endpoint deployment in appropriately designed networks.
Better Long-Term Internet Scalability
The largest strategic benefit of IPv6 is continued Internet growth without dependence on the increasingly constrained IPv4 address space.
It allows providers and organizations to build networks with:
- Large subnet allocations
- Native IPv6 connectivity
- IPv6-only segments
- Reduced dependence on carrier-grade IPv4 NAT
IPv6 Security: What It Does and Does Not Provide
IPv6 is sometimes described as being inherently more secure than IPv4.
That description is misleading.
IPsec and IPv6
IPv6 was designed with IPsec in mind, but modern IPv6 node requirements do not mean every IPv6 session automatically uses IPsec.
Current standards recommend support for the IPsec architecture, but actual protection still requires:
- Configuration
- Security associations
- Key management
- Appropriate deployment
Therefore:
IPv6 ≠ Automatically encrypted traffic
A normal IPv6 HTTP connection is still unencrypted HTTP.
A normal IPv6 Telnet connection is still insecure Telnet.
Use technologies such as:
- TLS
- SSH
- IPsec
- Application encryption
where appropriate.
IPv6 Still Needs a Firewall
Globally unique addresses should not be confused with unrestricted Internet accessibility.
A stateful firewall should control:
- Inbound traffic
- Outbound traffic
- Management access
- Inter-VLAN traffic
- Server exposure
Neighbor Discovery Security
IPv6 uses Neighbor Discovery instead of ARP.
This creates security considerations involving:
- Rogue Router Advertisements
- Neighbor Advertisement spoofing
- DHCPv6 spoofing
- Duplicate Address Detection attacks
Enterprise access networks may use controls such as:
- RA Guard
- DHCPv6 Guard
- Neighbor Discovery inspection
- IPv6 Source Guard
ICMPv6 Is Important
ICMPv6 supports critical functions including:
- Neighbor Discovery
- Router Discovery
- Error reporting
- Path MTU Discovery
Do not create a blanket policy that blocks all ICMPv6.
Use standards-aware filtering instead.
Dual Stack Means Two Security Paths
A dual-stack server may be reachable over:
- IPv4
- IPv6
Security teams therefore need to review both.
A server protected over IPv4 but accidentally exposed through IPv6 is still exposed.
IPv4 vs IPv6 and Deployment Considerations
IPv6 solves important scaling problems, but migration requires planning.
| Feature | IPv4 | IPv6 |
|---|---|---|
| Address Size | 32 bits | 128 bits |
| Example | 192.0.2.10 |
2001:db8::10 |
| Address Space | About 4.3 billion | About 3.4 × 10³⁸ |
| Broadcast | Supported | Not used |
| Multicast | Supported | Fundamental to several functions |
| Address Resolution | ARP | Neighbor Discovery |
| Autoconfiguration | DHCP / manual | SLAAC / DHCPv6 / manual |
| Normal LAN Prefix | Varies by host requirement | Commonly /64 |
| Router Fragmentation | Possible | Not performed by routers |
| NAT for Address Conservation | Common | Usually not required for conservation |
Dual-Stack Complexity
Many organizations operate:
IPv4 + IPv6
simultaneously.
This provides compatibility but means administrators must manage:
- Two address families
- Two routing environments
- Firewall policy for both
- Monitoring for both
- DNS A and AAAA records
- Troubleshooting for both
Legacy Applications
Older applications may:
- Store addresses in IPv4-only fields
- Parse addresses incorrectly
- Assume dotted-decimal notation
- Reject IPv6 literals
- Generate incomplete logs
Applications should be tested rather than assumed to support IPv6.
Operational Skills
Engineers need to understand:
- IPv6 notation
- Prefix lengths
- Neighbor Discovery
- Router Advertisements
- SLAAC
- DHCPv6
- ICMPv6
- IPv6 routing
The notation may look unfamiliar initially, but the fundamental networking principles remain similar.
IPv6 Does Not Guarantee Better Performance
IPv6 may provide a better path in some environments.
IPv4 may provide a better path in others.
Performance depends on real infrastructure rather than simply the IP version.
IPv6 Is Increasingly an Operational Requirement
Modern environments may encounter IPv6 in:
- Home broadband
- Mobile networks
- Cloud environments
- Content-delivery networks
- Enterprise networks
- ISP access networks
- Data centers
Administrators should therefore understand IPv6 even in environments where the migration is not yet complete.
Key Takeaways and Summary
Key Takeaways
- IPv6 uses 128-bit addresses compared with IPv4’s 32-bit addresses.
- An IPv6 address is written as eight hexadecimal groups and can be shortened using zero suppression and
::compression. - IPv6 defines unicast, anycast, and multicast addressing and does not use broadcast.
- Important unicast forms include Global Unicast, Link-Local, Unique Local, Loopback, and Unspecified addresses.
- Link-local addresses are fundamental to many IPv6 local-link operations and are not routed between links.
- SLAAC, DHCPv6, and static configuration can all participate in IPv6 address assignment.
- Modern IPv6 hosts should not be assumed to generate Interface Identifiers directly from stable MAC addresses.
- IPv6’s larger address space enables scalable hierarchical subnet planning and reduces dependence on IPv4-style NAT for address conservation.
- IPv6 does not automatically encrypt traffic or make a network secure simply because IPsec exists.
- IPv6 should receive the same firewalling, monitoring, vulnerability management, and operational attention as IPv4.
Summary
IPv6 addresses are the foundation of modern IPv6 networking.
A 128-bit address provides an enormous address space and allows organizations to design networks using structured prefixes rather than aggressively conserving individual host addresses.
IPv6 also introduces important addressing concepts including:
- Global Unicast
- Link-Local
- Unique Local
- Multicast
- Anycast
- SLAAC
- Temporary addresses
The move from IPv4 to IPv6 also changes several operational mechanisms.
IPv6 uses:
Neighbor Discovery instead of ARP
and:
Multicast instead of broadcast
while hosts can obtain configuration through:
- Router Advertisements
- SLAAC
- DHCPv6
- Static configuration
The larger address space reduces the requirement for IPv4-style NAT purely for address conservation, but it does not remove the need for:
- Stateful firewalls
- Access controls
- Segmentation
- Monitoring
- Application security
Similarly, IPv6’s relationship with IPsec should not be interpreted as automatic encryption.
IPv6 security still requires deliberate configuration.
The most important reason to understand IPv6 addressing is therefore not simply:
IPv6 has more addresses.
It is that modern networks increasingly need an addressing architecture capable of supporting large-scale connectivity, structured subnetting, cloud services, mobile systems, and continued Internet growth.
Understanding IPv6 addresses is the first step toward understanding the rest of IPv6 networking.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


