
Prerequisites: Basic FTP, TCP, IP Addressing and Firewall Concepts
Imagine connecting to an FTP server to download a file.
You enter the correct username and password, and the FTP server accepts your login.
However, when you try to view the available files, the directory listing fails.
How can the login succeed while the file transfer does not work?
The answer is related to how FTP establishes its connections.
FTP uses one connection to exchange commands and another connection to transfer files or directory listings.
The second connection is called the data connection.
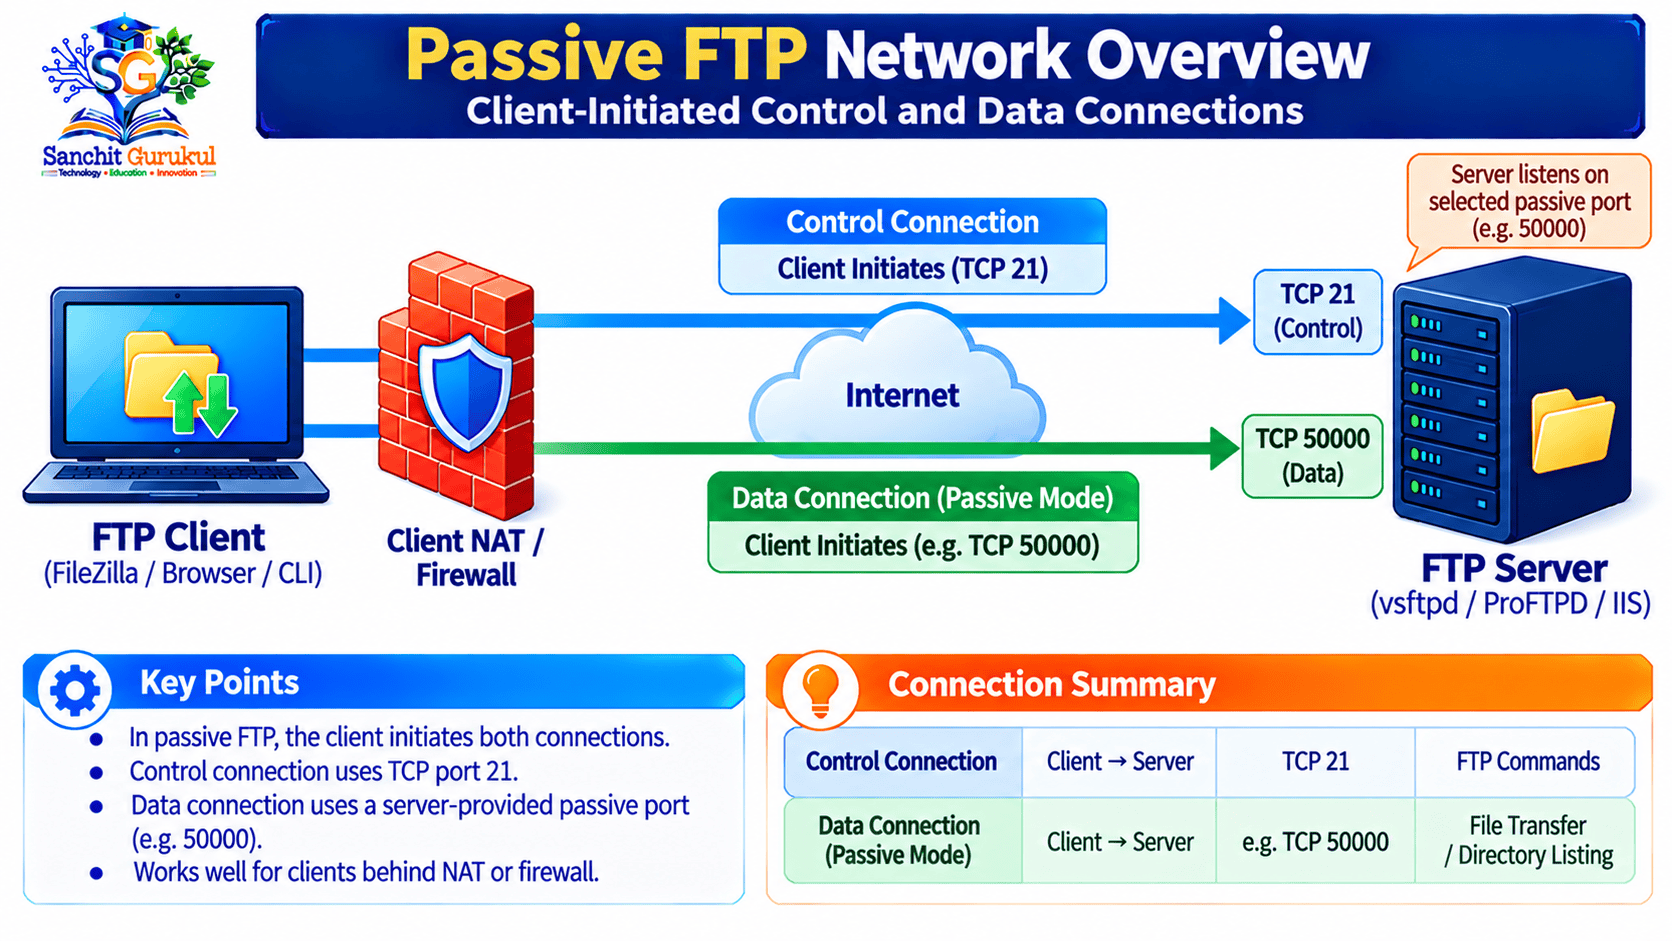
In Passive FTP, the client initiates this data connection toward a listening port on the FTP server.
This is particularly useful when the client is behind a firewall or Network Address Translation (NAT) device that restricts incoming connections.
In this article, you will learn:
- What Passive FTP is
- Why passive mode is used
- How control and data connections work
- How the PASV and EPSV commands operate
- How passive FTP port numbers are calculated
- Why passive mode is useful with NAT and firewalls
- How passive FTP supports uploads and downloads
- Common connection problems and troubleshooting
- Security considerations for FTP and FTPS
What Is Passive FTP and Why Is It Used?
Passive FTP is an operating method of the File Transfer Protocol in which the FTP server listens for a data connection and the client initiates that connection.
It is defined through the PASV mechanism in RFC 959.
A related, extended mechanism called EPSV is specified in RFC 2428.
Why Does FTP Need Passive Mode?
Standard FTP separates command communication from file transfer.
The client normally initiates the control connection to server TCP port 21.
However, the data connection can be established in different ways.
In traditional active FTP, the server initiates the data connection toward the client.
This can create problems if a client is behind a firewall or NAT router that does not permit the incoming connection.
Passive FTP changes which endpoint starts the data connection.
Instead of requiring the server to connect back to the client, the client connects to a listening port on the server.
Two Connections in Passive FTP
| Connection | Purpose | Initiated By |
|---|---|---|
| Control Connection | Commands and responses | FTP Client |
| Data Connection | Files and directory listings | FTP Client |
The two connections are separate TCP connections.
The data connection normally uses a port selected by the server rather than a fixed universal passive FTP port.
Does Passive FTP Only Download Files?
No.
Passive FTP supports:
- File downloads
- File uploads
- Directory listings
The client initiates the TCP data connection in all these cases.
Once the TCP connection exists, information can travel in either direction, depending on the requested FTP operation.
For example:
Download: The server sends file content to the client.
Upload: The client sends file content to the server.
Directory Listing: The server sends the requested listing to the client.
How Passive FTP Works — Step-by-Step Connection Process
Let’s understand a typical passive FTP download.
Consider the following example setup:
| Component | Example |
|---|---|
| FTP Client | 192.168.1.100 |
| Client Network | Behind a NAT router |
| FTP Server | 203.0.113.20 |
| FTP Control Port | TCP 21 |
| FTP Passive Data Port | TCP 50000 |
| File | example.txt |
The addresses are illustrative. 203.0.113.20 is a documentation address, not a live internet server.
Step 1 — Establish the Control Connection
The FTP client opens a TCP connection to:
203.0.113.20:21
The server responds that the FTP service is ready.
220 FTP Server ReadyThe control connection is now available for FTP commands.
Step 2 — Authenticate the User
The client provides its username.
If required, the server requests a password.
A simplified exchange is:
USER student
PASS example-password331 Password Required
230 User Logged InThese are illustrative commands and responses, not a live capture.
The password is a placeholder.
Step 3 — Request Passive Mode
The client sends:
PASVThe PASV command asks the server to prepare a listening data endpoint.
Step 4 — Server Advertises a Passive Port
The server selects an available listening port and returns the corresponding connection information.
For example:
227 Entering Passive Mode (203,0,113,20,195,80)The response contains an IPv4 address and two numbers representing a TCP port.
We will calculate the port in the next section.
Step 5 — Establish the Data Connection
The FTP client uses the response to establish a separate TCP connection to the appropriate server endpoint.
In this example:
203.0.113.20:50000
The client chooses its own TCP source port.
The server waits for the client to connect.
Step 6 — Request the File
The client requests the file using:
RETR example.txtThe server may respond:
150 Opening Data ConnectionThe server transfers the requested file through the separate data connection.
The control connection continues to carry commands and response messages.
Step 7 — Complete the Transfer
After the file transfer finishes successfully, the server may respond:
226 Transfer CompleteThe data connection is normally closed following the transfer in the typical FTP stream-mode workflow.
The control connection can remain open for additional FTP operations.
Step 8 — End the FTP Session
When the client has finished, it can send:
QUITA typical successful response is:
221 Service Closing Control Connection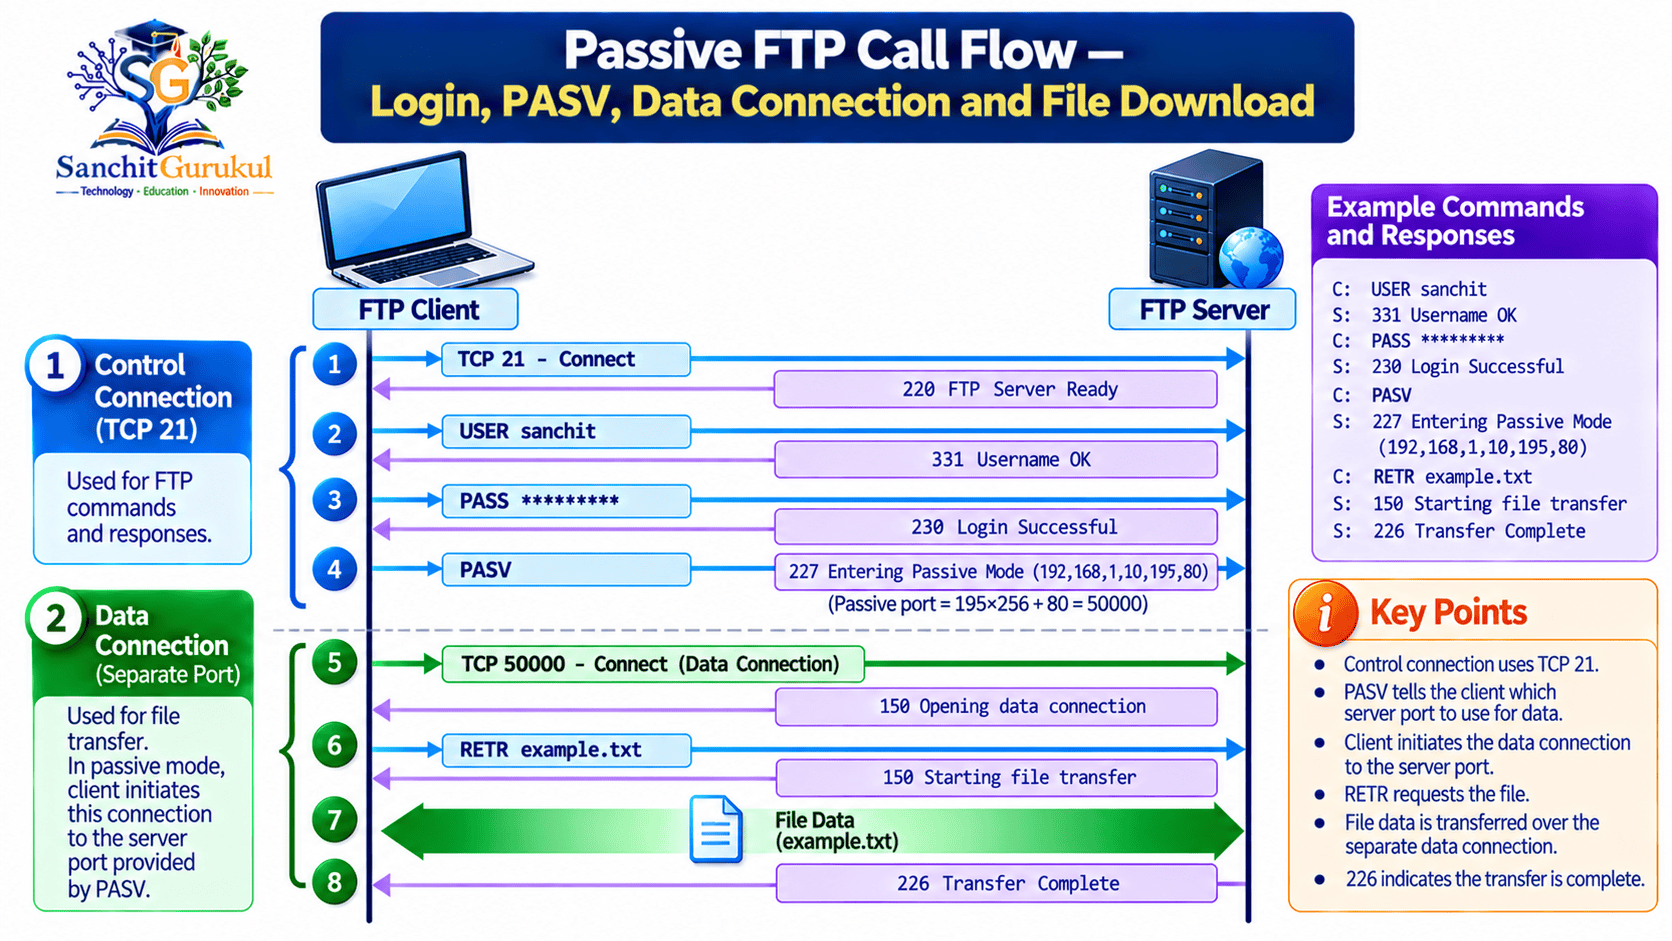
PASV vs EPSV — Commands, Responses and Port Calculation
Passive FTP commonly uses two related commands:
- PASV
- EPSV
They both allow the client to establish a data connection toward the server.
The main difference is how the connection information is returned.
What Is PASV?
PASV is the traditional passive-mode FTP command defined in RFC 959.
The client sends:
PASVThe server responds with code 227 and connection details.
For example:
227 Entering Passive Mode (203,0,113,20,195,80)The response has six numeric fields.
The first four represent the IPv4 address.
The final two represent the TCP port.
How to Calculate the Passive FTP Port
The port calculation is:
Port = (p1 × 256) + p2
For our example:
- p1 = 195
- p2 = 80
Therefore:
Port = (195 × 256) + 80 = 50000
The server is advertising TCP port 50000.
What Is EPSV?
EPSV means Extended Passive Mode.
It is defined in RFC 2428.
EPSV is useful for both IPv4 and IPv6 communication.
The client sends:
EPSVThe server may respond:
229 Entering Extended Passive Mode (|||50000|)This response provides the TCP data port without including the server IP address in the same way as PASV.
The client uses the server address associated with the control connection, according to RFC 2428.
PASV vs EPSV Comparison
| Feature | PASV | EPSV |
|---|---|---|
| Standard | RFC 959 | RFC 2428 |
| FTP Command | PASV | EPSV |
| Success Response | 227 | 229 |
| Includes IPv4 Address | Yes | No |
| Includes TCP Data Port | Yes | Yes |
| IPv6 Support | Not in traditional PASV format | Yes |
| Common Use | Traditional IPv4 FTP | IPv4/IPv6-compatible FTP |
Why Is EPSV Helpful with NAT?
Traditional PASV includes an IPv4 address inside the FTP control response.
When the server is behind NAT, that address may not be suitable for an external client.
EPSV avoids including an explicit IP address in its standard response.
The client uses the control connection’s server address and the supplied port.
However, the server must still be reachable on that port through the relevant network and firewall configuration.

Passive FTP with Firewalls and NAT — Why Transfers Sometimes Fail
Passive FTP is often used because it works more naturally with many client-side firewall and NAT configurations.
However, passive FTP does not eliminate firewall requirements.
Client-Side Firewall
In a typical passive FTP connection:
- The client initiates the control TCP connection.
- The client initiates the data TCP connection.
- The server accepts both incoming connections.
Many stateful client-side firewalls allow permitted outbound connections and the matching return traffic.
This makes passive mode easier to use than active mode in many environments.
Server-Side Firewall
The FTP server must permit the incoming control connection.
It must also accept incoming data connections on the configured passive port range.
For example:
FTP Control Port:
TCP 21

Illustrative Passive Data Port Range:
TCP 50000–50100

FTP Server:
203.0.113.20

Connection Mode:
Passive FTP
This is an example configuration plan, not a vendor-specific command.
The selected ports must match the FTP server configuration.
What Happens if the Passive Port Is Blocked?
Consider this scenario:
The client connects successfully to TCP port 21.
The username and password are accepted.
The client sends PASV.
The server returns TCP port 50000.
The client attempts to connect to TCP port 50000.
However, the server firewall blocks that connection.
The control connection still works, but the file operation cannot proceed.
Passive FTP Server Behind NAT
When an FTP server is behind a NAT router, the configuration can become more complex.
The server may need:
- An appropriate passive port range
- Correct firewall rules
- Suitable NAT port forwarding
- Correct external addressing for traditional PASV
- Compatible FTP client and server settings
For example, a server might have a private address but be accessed through a public address.
If it advertises the private address to an external client, the client may be unable to connect.
Some clients can handle certain unsuitable PASV addresses, but such behavior should not be relied upon as a universal solution.
Why Does Passive FTP Work but Sometimes Still Time Out?
Possible causes include:
- Passive data ports blocked by a firewall
- Incorrect NAT forwarding
- Incorrect server-advertised IP address
- FTP server listening on the wrong interface
- Network routing problems
- Server resource limitations
- TLS-related configuration issues in FTPS

Passive FTP Security — FTP, FTPS and SFTP
Passive FTP does not automatically provide encryption.
It only changes how the data TCP connection is established.
Traditional FTP may transmit usernames, passwords and file contents without encryption.
Is Passive FTP Secure?
Passive FTP can be easier to manage with firewalls.
However, that does not mean it protects transmitted information from interception.
Connection behavior and data encryption are different concepts.
What Is FTPS?
FTPS is FTP protected with Transport Layer Security (TLS).
It supports secure communication when properly configured.
FTPS can still use passive data connections.
For strong protection, the administrator must ensure that the relevant data connection is also encrypted.
For example, RFC 4217 defines PROT P as the FTP-TLS data protection level for a TLS-protected data connection.
What Is SFTP?
SFTP stands for SSH File Transfer Protocol.
It is a separate protocol that commonly runs through SSH on TCP port 22.
SFTP does not use FTP’s PASV or EPSV commands.
It should not be confused with Passive FTP.
Security Comparison
| Feature | Passive FTP | Passive FTPS | SFTP |
|---|---|---|---|
| Underlying Protocol | FTP | FTP with TLS | SSH File Transfer |
| Data Connection Initiated by Client | Yes | Yes | Not applicable in the FTP sense |
| Separate FTP Data Connection | Yes | Yes | No |
| Encryption | No, by default | When properly configured | Through SSH |
| Common Control Port | TCP 21 | Usually TCP 21 for explicit FTPS | Usually TCP 22 |
| PASV/EPSV Used | Yes | Yes | No |
Practical Troubleshooting — Passive FTP Login Works but File Transfer Fails
Let’s examine a simple troubleshooting case.
Scenario
A user reports:
“I can connect to the FTP server and log in successfully, but the file list does not appear.”
The FTP server uses passive mode.
The server’s control connection is available on TCP port 21.
Its passive data ports are configured within the range:
50000–50100
Step 1 — Verify the Control Connection
Confirm that the client can connect and authenticate.
A successful login indicates that the control connection is working.
Step 2 — Identify the Passive Response
Check the FTP client log or an authorized packet capture.
Look for a response such as:
227 Entering Passive Mode (203,0,113,20,195,80)This indicates the server advertised TCP port 50000.
Step 3 — Check the Data Connection
Determine whether the client actually attempts to connect to the advertised port.
If the TCP SYN receives no response, investigate relevant firewall, NAT and routing conditions.
If the connection is refused, check whether the server is listening on the expected port and whether another device rejected the connection.
Step 4 — Check Server Firewall and NAT
Confirm that the selected passive port is available through the expected network path.
Verify that the server has been configured with a suitable passive port range.
Step 5 — Review FTP Server Logs
Useful response codes include:
| FTP Code | Meaning |
|---|---|
| 220 | FTP service ready |
| 227 | Entering passive mode |
| 229 | Entering extended passive mode |
| 150 | File status okay; opening data connection |
| 226 | Data transfer action completed successfully |
| 425 | Cannot open data connection |
| 530 | Not logged in |
| 550 | Requested action not taken |
Step 6 — Verify the Transfer
After an approved correction, retry:
- Directory listing
- File download
- File upload, if permitted
Confirm that the operation completes successfully.
Wireshark Display Filters
For an authorized plain-FTP packet capture, Wireshark can help inspect control commands.
ftpFor the standard FTP control port:
tcp.port == 21For the example passive data port:
tcp.port == 50000If FTPS encrypts the control session, its commands will not normally be readable without authorized TLS decryption.
What Should You Check?
- Did the control TCP connection succeed?
- Did the client send PASV or EPSV?
- Which passive port did the server advertise?
- Did the client send a SYN to the passive port?
- Did the server respond?
- Did the data connection establish?
- Was the transfer completed successfully?
Key Takeaways
Core Concepts
- Passive FTP is a connection mode of FTP.
- The client initiates both the control and data TCP connections.
- The control connection normally uses server TCP port 21.
- The data connection uses a port selected by the server.
PASV and EPSV
- PASV uses the FTP command
PASV. - A successful PASV response uses code 227.
- PASV includes an IPv4 address and encoded port.
- EPSV is an extended passive mechanism.
- A successful EPSV response uses code 229.
- EPSV normally returns the selected listening port.
Firewall and NAT
- Passive mode is often easier for clients behind NAT.
- Server-side firewalls must allow the required data connections.
- Passive FTP servers behind NAT may need port forwarding and address configuration.
- A successful login does not prove that file transfers will work.
Security and Troubleshooting
- Passive FTP supports uploads and downloads.
- Passive FTP does not automatically provide encryption.
- FTPS can protect FTP control and data channels with TLS.
- SFTP is a separate SSH-based protocol.
- Troubleshooting should identify the failed connection stage.
Passive FTP is an important operating mode of File Transfer Protocol.
Its main advantage is that the FTP client initiates the data connection rather than requiring the server to connect back toward the client.
This often makes it easier to use FTP through client-side firewalls and NAT devices.
The PASV and EPSV commands tell the client how to establish the separate data connection.
However, the FTP server must still be configured with suitable listening ports and firewall access.
Passive FTP is not a security or encryption feature.
For sensitive file transfers, an appropriately configured secure alternative should be used.
Understanding control connections, passive data ports, PASV responses and EPSV responses makes FTP troubleshooting much easier.
Next in This Series: FTP Packet Analysis with Wireshark — PASV, EPSV, TCP Handshakes and File Transfer Troubleshooting.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


