
sFlow is a network telemetry technology designed to provide scalable visibility into traffic and network-device statistics by using statistical packet sampling together with periodic counter sampling.
Instead of attempting to export information about every packet traversing a high-speed network, an sFlow-capable device selects a statistically representative portion of traffic and sends measurement data to an external sFlow collector.
This makes sFlow especially useful in environments containing:
- High-speed Ethernet links
- Data-center fabrics
- Campus networks
- Enterprise switching
- Service-provider networks
- Multi-vendor environments
- Large numbers of interfaces
- Traffic-engineering platforms
- DDoS monitoring systems
sFlow can help answer questions such as:
- Which systems are generating the most traffic?
- Which protocols or applications dominate a link?
- Which networks are communicating?
- Is an interface experiencing errors?
- Is traffic suddenly increasing?
- Is an unusual traffic pattern appearing?
- Which VLANs or interfaces are involved?
- Is capacity approaching a threshold?
sFlow should be understood as a telemetry and statistical monitoring technology, not as a replacement for full packet capture or complete forensic logging.

What Is sFlow and Why Is It Used?
sFlow was designed to provide continuous network-wide monitoring of high-speed switched and routed networks.
Its architecture consists primarily of:
- Data Sources
- sFlow Agents
- sFlow Collectors
- Packet Flow Samples
- Counter Samples
- sFlow Datagrams
Current sFlow Version
The current specification is:
sFlow Version 5
sFlow.org states that earlier Versions 2 and 4 are deprecated and that new implementations should use Version 5.
An important historical distinction is:
RFC 3176 describes sFlow Version 4.
The later sFlow Version 5 specification explicitly replaced Version 4.
Therefore, RFC 3176 remains useful for understanding the history and core design of sFlow, but it should not be described as the current Version 5 specification.
sFlow Agent
The sFlow Agent runs on or is integrated into the monitored network device.
It is responsible for collecting telemetry from data sources such as:
- Physical interfaces
- VLANs
- Switching components
- Other supported measurement points
Depending on the implementation, packet sampling may be performed directly by switching hardware or other forwarding components.
sFlow Collector
The collector receives sFlow datagrams from one or many agents.
The collector can:
- Decode packet samples
- Process counter samples
- Estimate traffic volume
- Identify traffic patterns
- Produce dashboards
- Build historical trends
- Generate alerts
- Detect anomalies
An sFlow collector does not reconstruct every packet or every original connection.
It analyzes statistical telemetry exported by the network devices.
sFlow Transport
sFlow sends telemetry using:
UDP
The conventional/default sFlow collector port is:
UDP 6343
A different port can be configured when supported by the implementation.
How sFlow Packet and Counter Sampling Work
sFlow Version 5 uses two fundamental measurement mechanisms:
- Packet Flow Sampling
- Counter Sampling
These provide different but complementary information.
Packet Flow Sampling
Packet Flow Sampling randomly selects a fraction of observed packets.
Suppose the configured sampling rate is:
1:1000
This means that over time, approximately one packet is selected for every 1,000 eligible packets observed.
It does not mean that the device mechanically selects packet number 1,000, 2,000, 3,000, and so on.
The sFlow specification requires a statistical selection mechanism so that packets have an appropriate chance of being sampled.
A packet sample may contain information such as:
- Sampled packet header
- Original packet length
- Input interface
- Output interface
- Ethernet information
- VLAN information
- IPv4 or IPv6 information
- Transport-layer information
- Routing information
The exact information available depends on the device and sFlow record type.
Sampling Rate
The sampling rate represents the relationship between observed packets and generated samples.
For example:
| Sampling Rate | Interpretation |
|---|---|
| 100 | Approximately 1 sample per 100 packets |
| 1,000 | Approximately 1 sample per 1,000 packets |
| 10,000 | Approximately 1 sample per 10,000 packets |
| 100,000 | Approximately 1 sample per 100,000 packets |
A higher number means less frequent packet sampling.
A lower number means more frequent sampling.
Counter Sampling
Packet samples tell you about representative traffic.
Counter samples provide periodically collected operational statistics.
Depending on the implementation, these can include values such as:
- Interface octets
- Packets
- Errors
- Discards
- Broadcasts
- Multicasts
- Interface utilization
The configured period is commonly called the:
polling interval or counter sampling interval.
For example, an implementation might export counters every:
20 seconds
or:
30 seconds
but there is no requirement that every deployment use one fixed interval.
Why Both Are Important
Packet sampling can answer:
Who is communicating and what does the sampled traffic look like?
Counter sampling can answer:
How busy or healthy is the interface?
Together they provide more useful visibility than either measurement alone.
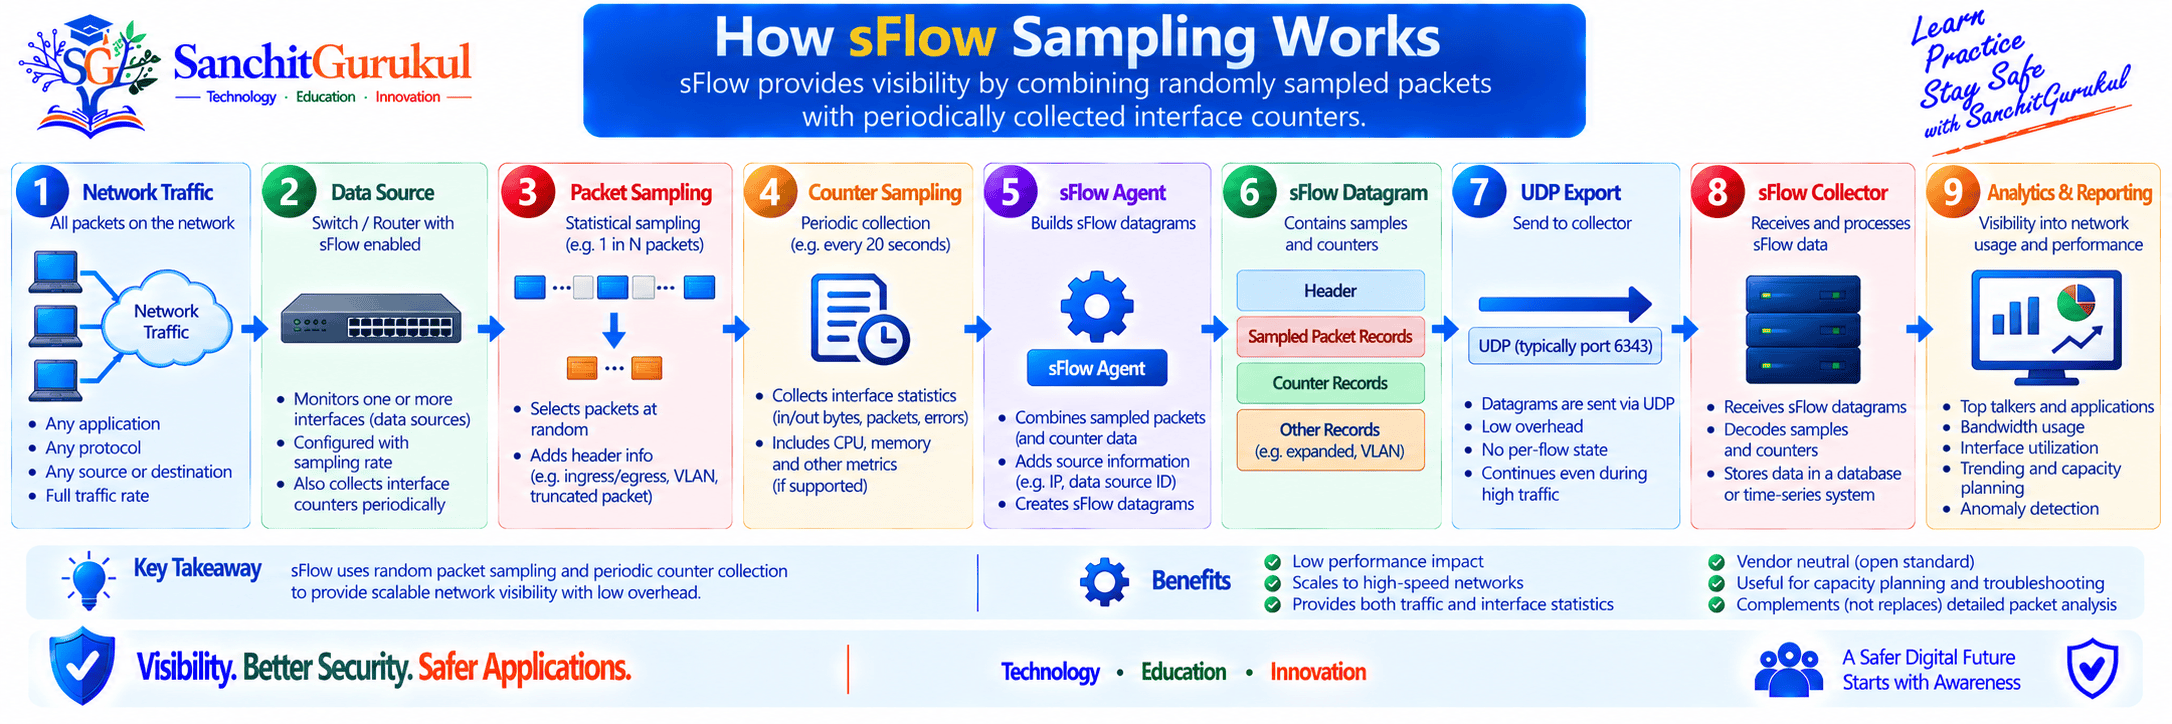
Simple Example
Consider a high-volume interface where sFlow is configured with a packet sampling rate of:
1:1000
The collector receives samples representing only a fraction of the traffic.
It uses the associated sampling information to make statistical estimates about the larger traffic population.
What Information Can sFlow Provide?
sFlow is more capable than simply exporting source and destination IP addresses.
Version 5 provides extensible structures for representing several types of telemetry.
Sampled Packet Information
Depending on implementation and packet type, the collector may receive information representing:
- Ethernet headers
- VLAN information
- IPv4
- IPv6
- TCP
- UDP
- Routing context
- MPLS
- NAT
- Tunnels
The device commonly exports only a portion of a sampled packet rather than the entire packet.
This reduces telemetry volume and limits the amount of payload information exported.
Forwarding Information
sFlow Version 5 can associate sampled traffic with forwarding context such as:
- Source interface
- Destination interface
- Source VLAN
- Destination VLAN
- Next-hop information
- Routing-related information
This can be particularly useful for determining where traffic is moving through a network.
Interface Counters
Counter records can help identify:
- Interface utilization
- Packet rates
- Errors
- Discards
- Broadcast/multicast levels
Combining flow samples with counter information allows a monitoring system to correlate:
Traffic behavior + interface health
Modern sFlow Extensions
The sFlow Version 5 ecosystem includes additional structures beyond basic packet and interface information.
Current sFlow.org specifications include extensions for areas such as:
- Dropped packets
- Transit delay
- Queue depth
- Optical interfaces
- LAG/LACP counters
- Tunnels
- Hardware table utilization
- Buffer utilization
- Host statistics
- TCP/IP host counters
- Application performance
- GPU monitoring
Support for these extensions is implementation-dependent.
A collector cannot display telemetry that the agent does not export.
sFlow Is Not Full Packet Capture
sFlow and tools such as Wireshark serve different purposes.
| sFlow | Full Packet Capture |
|---|---|
| Samples packets | Captures selected/all packets |
| Designed for continuous telemetry | Often used for detailed analysis |
| Statistical traffic view | Packet-by-packet evidence |
| Lower telemetry volume | Potentially very large storage requirement |
| Excellent for trends | Excellent for protocol-level investigation |
| May miss rare packets | Can preserve every captured packet |
sFlow vs NetFlow and IPFIX
sFlow, NetFlow, and IPFIX are often grouped together because they all provide traffic telemetry.
Their measurement models, however, are different.
sFlow
sFlow primarily exports:
- Statistical packet samples
- Counter samples
- Associated metadata
The architecture does not require the exporter to build a conventional per-flow cache for every observed connection.
NetFlow
NetFlow originated with Cisco.
Traditional and Flexible NetFlow identify traffic using a set of flow keys and maintain flow records representing packets that share those characteristics.
A flow record may contain values such as:
- Source address
- Destination address
- Protocol
- Ports
- Interface
- Packet count
- Byte count
- Timestamps
NetFlow Can Also Use Sampling
A common but incorrect comparison is:
sFlow samples traffic, while NetFlow records every flow.
Modern Flexible NetFlow can also use packet sampling.
Cisco specifically documents Flexible NetFlow Flow Sampling as a mechanism for reducing the processing load associated with traffic analysis.
The important difference is therefore not simply:
sampling vs no sampling
but rather the underlying telemetry model.
IPFIX
IP Flow Information Export, or IPFIX, is an IETF-standardized flow-export protocol derived from concepts used in NetFlow Version 9.
IPFIX uses template-based data records and is supported by multiple networking and monitoring vendors.
Practical Comparison
| Characteristic | sFlow | NetFlow / Flexible NetFlow | IPFIX |
|---|---|---|---|
| Primary model | Packet + counter sampling | Flow records | Flow records |
| Packet sampling | Fundamental design | Supported | Exporter dependent |
| Interface counters | Integrated sFlow model | Can export selected metrics | Template dependent |
| Per-flow cache required | Not inherent to sFlow sampling | Common design | Common exporter design |
| Sampled packet headers | Core capability | Possible with some Flexible NetFlow records | Template/implementation dependent |
| Standardization | sFlow.org specification | Originated with Cisco | IETF standard |
| Multi-vendor support | Broad | Broad in modern environments | Broad |
| Statistical visibility | Excellent | Depends on exporter | Depends on exporter |
| Complete forensic record | No | Not necessarily | Not necessarily |
Which Should You Use?
Use sFlow when you need:
- Highly scalable packet sampling
- Interface counters
- High-speed switching visibility
- Large numbers of interfaces
- Near-real-time statistical traffic analysis
Use NetFlow/Flexible NetFlow or IPFIX when you specifically require:
- Flow-oriented accounting
- Flow-duration information
- Detailed flow records
- Traffic accounting based on defined flow keys
Many enterprise monitoring architectures use more than one telemetry source.
sFlow, IPFIX, SNMP, streaming telemetry, logs, and packet capture can complement one another.
Benefits, Limitations and Common Use Cases
sFlow’s main strength is scalability.
High-Speed Network Monitoring
sFlow was designed specifically with high-speed switched and routed networks in mind.
Modern implementations can be used on links such as:
- 10 GbE
- 25 GbE
- 40 GbE
- 100 GbE
- 200 GbE
- 400 GbE
- 800 GbE
Support depends on the network platform.
Current NVIDIA Cumulus Linux documentation, for example, includes configurable sampling behavior through 800-Gbps interfaces.
Data-Center Visibility
In leaf-spine networks, sFlow can provide telemetry from many switch interfaces without requiring full packet capture at every location.
This can help identify:
- East-west traffic patterns
- North-south traffic
- Large traffic consumers
- Congestion
- Capacity changes
Capacity Planning
Historical sFlow information can help identify:
- Bandwidth growth
- Traffic distribution
- Busy links
- Application trends
- Changes in network behavior
DDoS Detection
sFlow can be effective for detecting large-volume traffic anomalies.
A collector may identify sudden increases in:
- Packets per second
- Traffic toward one destination
- UDP traffic
- SYN traffic
- Source address diversity
This can provide useful telemetry for DDoS detection systems.
Multi-Vendor Monitoring
sFlow is implemented by multiple network vendors.
Examples of platforms with documented sFlow support include products from vendors such as:
- Juniper Networks
- Arista Networks
- NVIDIA networking
- Other switch/router vendors
Exact capabilities and command syntax vary by product.
Important Limitations
Small Flows Can Be Missed
Because packet sampling is statistical, a short flow containing only a few packets may never be sampled.
A large elephant flow is much more likely to appear repeatedly.
Statistical Error Exists
Sampled telemetry is an estimate.
Accuracy improves with sufficient sample volume, but sampled values should not be interpreted as exact packet-by-packet records.
Not Suitable as the Only Forensic Source
sFlow does not provide a complete history of every connection.
For incident response requiring exact packet evidence, combine it with technologies such as:
- Full packet capture
- Firewall logs
- DNS logs
- Endpoint telemetry
- Flow logs
- Application logs
UDP Export Can Lose Datagrams
sFlow datagrams normally use UDP.
UDP does not provide retransmission or guaranteed delivery.
The protocol was designed so occasional telemetry loss does not require the agent to buffer and retransmit historical samples.
Deployment, Security and Troubleshooting Best Practices
A good sFlow implementation requires more than simply enabling sampling.
Select the Sampling Rate Deliberately
Do not copy one sampling rate to every interface.
Consider:
- Link speed
- Packet rate
- Collector capacity
- Number of devices
- Desired accuracy
- Type of traffic
Some platforms provide different defaults based on interface speed.
For example, current NVIDIA Cumulus Linux documentation uses progressively larger default sampling ratios as interface speed increases.
These are platform defaults, not universal sFlow requirements.
Choose an Appropriate Counter Interval
Short polling intervals provide faster visibility but produce more telemetry.
Long intervals reduce telemetry volume but may hide short-term changes.
Select an interval appropriate for:
- Monitoring requirements
- Interface count
- Collector performance
- Vendor recommendations
Monitor Important Traffic Paths
Useful locations can include:
- Data-center uplinks
- Internet edges
- Core links
- WAN interfaces
- Leaf-spine links
- Critical server networks
Enabling telemetry everywhere may be appropriate in some hardware-based implementations, but deployment should still consider collector capacity and operational requirements.
Use a Stable Agent Address
Configure a predictable source/agent address where supported.
A management or loopback address is often preferable because it is less likely to change than a physical interface address.
Validate Collector Connectivity
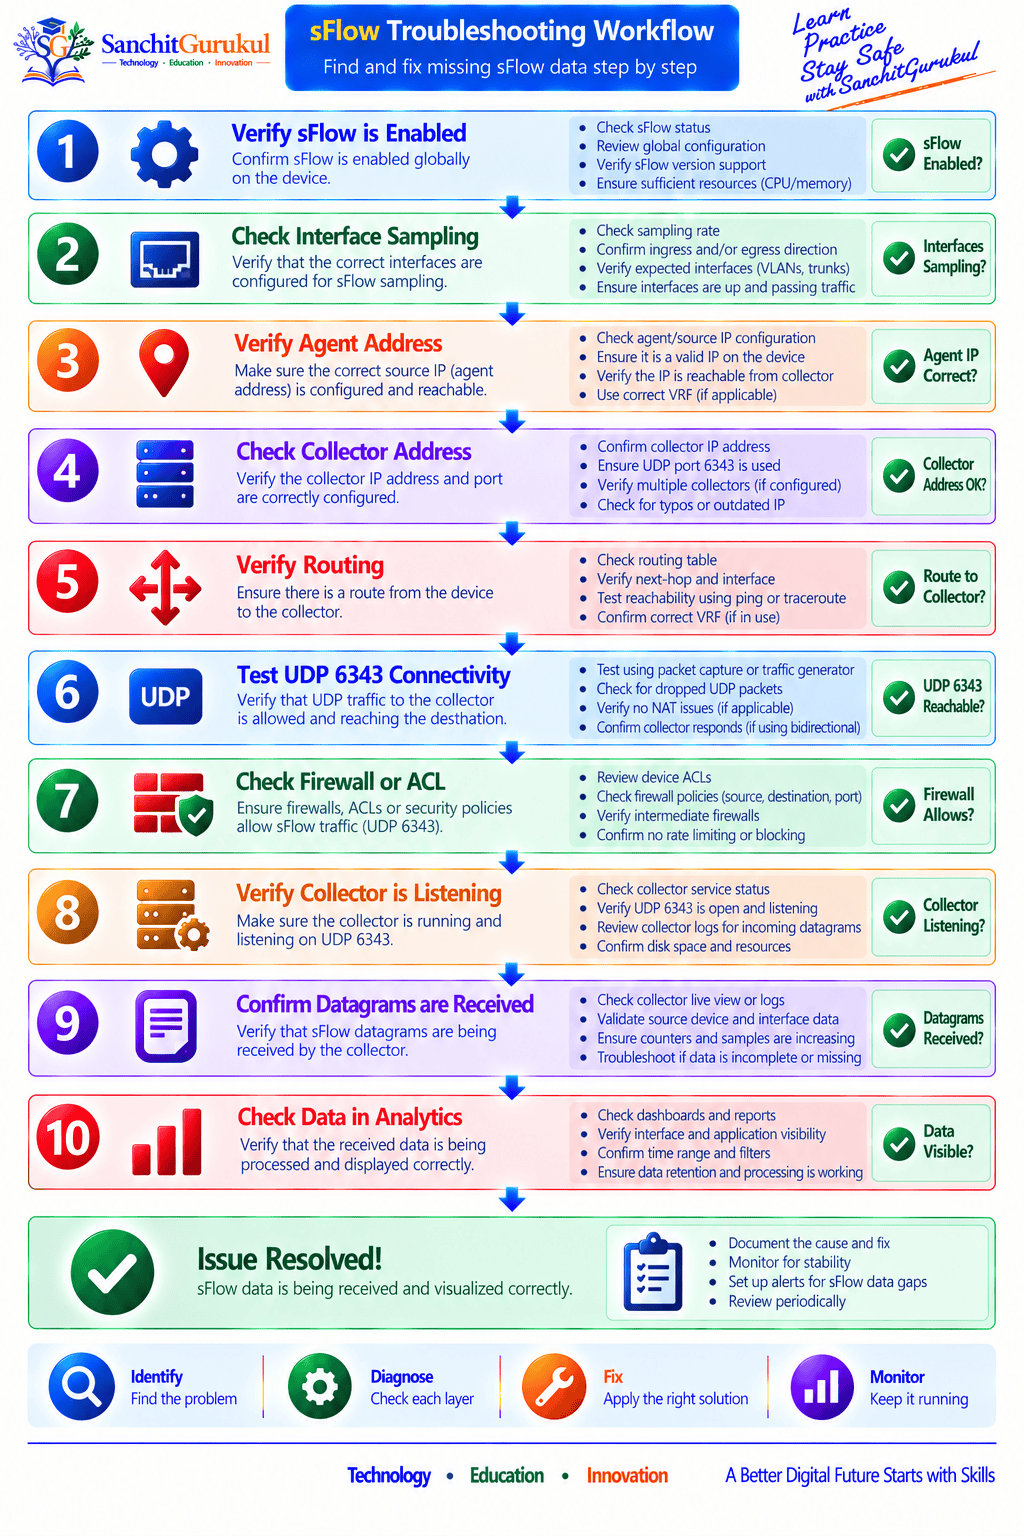
On a Linux-based collector, check whether sFlow datagrams are arriving:
sudo tcpdump -ni any udp port 6343Example output might show:
IP 192.0.2.10.52000 > 192.0.2.100.6343: UDP
IP 192.0.2.11.49152 > 192.0.2.100.6343: UDP
If nothing arrives, check:
- sFlow is enabled.
- The correct interfaces are monitored.
- Collector IP address is correct.
- UDP port matches.
- Routing is correct.
- ACL/firewall permits the export.
- A valid agent address is configured.
- The collector is listening.
Protect sFlow Telemetry
This is an important security consideration.
Native sFlow datagrams are normally exported over UDP and do not inherently provide encryption or authentication.
Sampled packet headers and traffic patterns may reveal information about:
- Internal IP addresses
- Network topology
- User activity
- Applications
- Communication relationships
Use controls such as:
- Dedicated telemetry/management networks
- Network ACLs
- Collector access controls
- VPN/IPsec when telemetry crosses an untrusted network
- Restricted collector administration
Protect the Collector
The collector should accept telemetry only from authorized agents where practical.
Also protect:
- Dashboards
- Historical traffic data
- APIs
- Stored telemetry
- Administrative accounts
Traffic metadata can reveal significant details about an organization’s network.
Key Takeaways and Summary
Key Takeaways
- sFlow is a statistical network-monitoring technology designed for scalable traffic visibility.
- The current specification is sFlow Version 5.
- RFC 3176 describes the older sFlow Version 4 rather than current Version 5.
- sFlow combines random packet-flow sampling with periodic counter sampling.
- An sFlow Agent exports telemetry to an external sFlow Collector.
- sFlow datagrams normally use UDP, with port 6343 commonly used as the default.
- Sampling rates represent statistical ratios rather than deterministic every-Nth-packet selection.
- Counter sampling provides interface and device statistics alongside packet samples.
- sFlow can provide forwarding context such as interfaces, VLANs, and routing information when supported.
- sFlow is excellent for traffic trends, capacity analysis, high-speed networks, and anomaly detection.
- sFlow cannot guarantee visibility into every short-lived or low-volume flow.
- It is not a replacement for full packet capture when exact forensic evidence is required.
- NetFlow can also use sampling, so the difference between sFlow and NetFlow is not simply sampled versus unsampled traffic.
- sFlow Version 5 provides an extensible telemetry model with numerous modern extensions.
- sFlow telemetry is not inherently encrypted, so collectors and export paths must be appropriately protected.
Summary
sFlow provides an efficient approach to network-wide traffic monitoring by combining:
Statistical packet sampling + counter polling + centralized analysis.
Its architecture makes it particularly useful for modern high-capacity networks where capturing or processing every packet at every interface would be operationally expensive.
A typical deployment consists of:
Network Device → sFlow Agent → UDP Datagrams → sFlow Collector → Analytics
sFlow can help administrators understand:
- Who is communicating
- Where traffic is flowing
- Which links are busy
- Which protocols dominate
- Whether interfaces are experiencing errors
- Whether unusual traffic patterns are emerging
Its main limitation is also the reason it scales so effectively:
sFlow intentionally samples traffic rather than attempting to preserve every packet or every individual flow.
For the best visibility, use sFlow as one part of a broader observability strategy alongside technologies such as:
- SNMP
- Streaming telemetry
- NetFlow/IPFIX
- Logs
- Packet capture
- SIEM
- Network performance monitoring
The monitoring technology should always be selected according to the question you need the network to answer.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


