
Prerequisites: Basic TCP/IP, FTP and SSH Fundamentals
Imagine you manage a web server containing important application files.
You need to upload a new configuration file from your computer.
The file must travel across the internet, but you do not want anyone monitoring the network to read its contents or capture your login password.
Traditional FTP does not encrypt this communication.
How can you transfer the file securely?
One widely used solution is SFTP (SSH File Transfer Protocol).
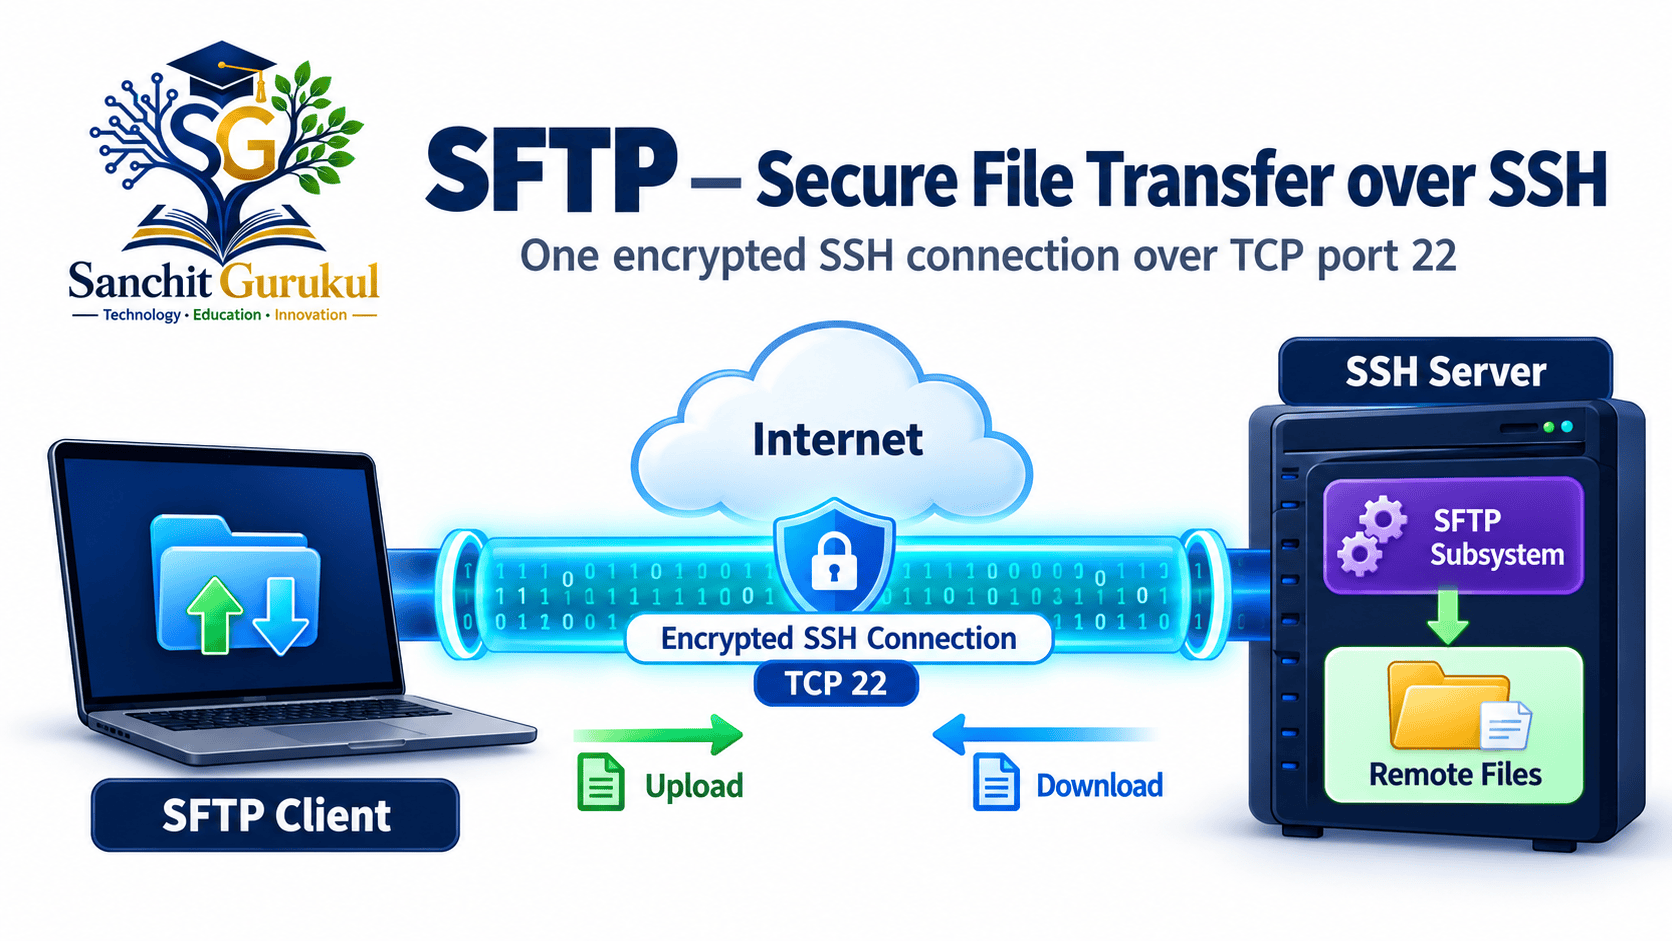
SFTP allows a client to upload, download and manage files on a remote server using a connection protected by Secure Shell (SSH).
Unlike traditional FTP, SFTP does not require separate control and data connections.
It uses an SSH connection that provides encryption, integrity protection and server authentication.
SFTP is commonly used for website administration, server maintenance, automated file exchange and other tasks involving sensitive information.
In this article, you will learn:
- What SFTP is and how it differs from FTP
- How SFTP works over SSH
- Why TCP port 22 is commonly used
- Password and public-key authentication
- SSH host-key verification
- Common SFTP commands
- How to upload and download files
- SFTP vs FTP vs FTPS
- Benefits, limitations and troubleshooting
- Best practices for secure file transfers
What Is SFTP and How Is It Different from FTP?
SFTP stands for SSH File Transfer Protocol.
It is also commonly called Secure File Transfer Protocol.
SFTP provides a method for performing remote file operations over an SSH connection.
The protocol supports tasks such as:
- Uploading files
- Downloading files
- Listing directories
- Creating directories
- Renaming files
- Deleting files
- Reading file information
- Changing supported file attributes
The actual operations available depend on the server, SFTP protocol version and user permissions.
Is SFTP a Version of FTP?
No.
SFTP and FTP are separate protocols.
Although both transfer files, they use different communication methods.
Traditional FTP uses:
- A control connection
- A separate data connection
- Commands such as USER, PASS, RETR and STOR
- Active or passive data connection establishment
SFTP commonly uses:
- An SSH transport connection
- SSH authentication
- An SFTP subsystem or compatible server implementation
- SFTP file operation messages
FTP’s PORT, PASV and EPSV commands are not part of SFTP.
Does SFTP Use TCP Port 22?
SFTP commonly uses TCP port 22 because it normally operates through SSH.
However, an SSH server can be configured to listen on another TCP port.
For example, an administrator may configure a supported SSH service on TCP port 2222.
The SFTP client must then specify the correct port.
Does Every SSH Server Support SFTP?
Not necessarily.
The server needs an SFTP-capable subsystem or an equivalent implementation.
An SSH server can support remote shell access without necessarily providing SFTP service.
Similarly, some organizations provide SFTP-only accounts that are not permitted to open an interactive remote shell.
How SFTP Works — SSH Connection, Authentication and File Transfer
An SFTP session normally begins by establishing an SSH connection to the remote server.
The process has several important stages.
Step 1 — Establish a TCP Connection
The client connects to the SSH server.
For a typical deployment:
| Component | Example |
|---|---|
| SFTP Client | User’s computer |
| SFTP Server | files.example.com |
| Transport Protocol | TCP |
| Server Destination Port | 22 |
| Security Protocol | SSH |
The hostname files.example.com is illustrative.
Step 2 — Negotiate SSH Security
The client and server negotiate compatible SSH algorithms and establish protected communication.
This process involves mechanisms such as:
- Key exchange
- Server host-key authentication
- Encryption
- Integrity protection
The exact algorithms depend on the SSH implementation and configuration.
Step 3 — Verify the Server’s Identity
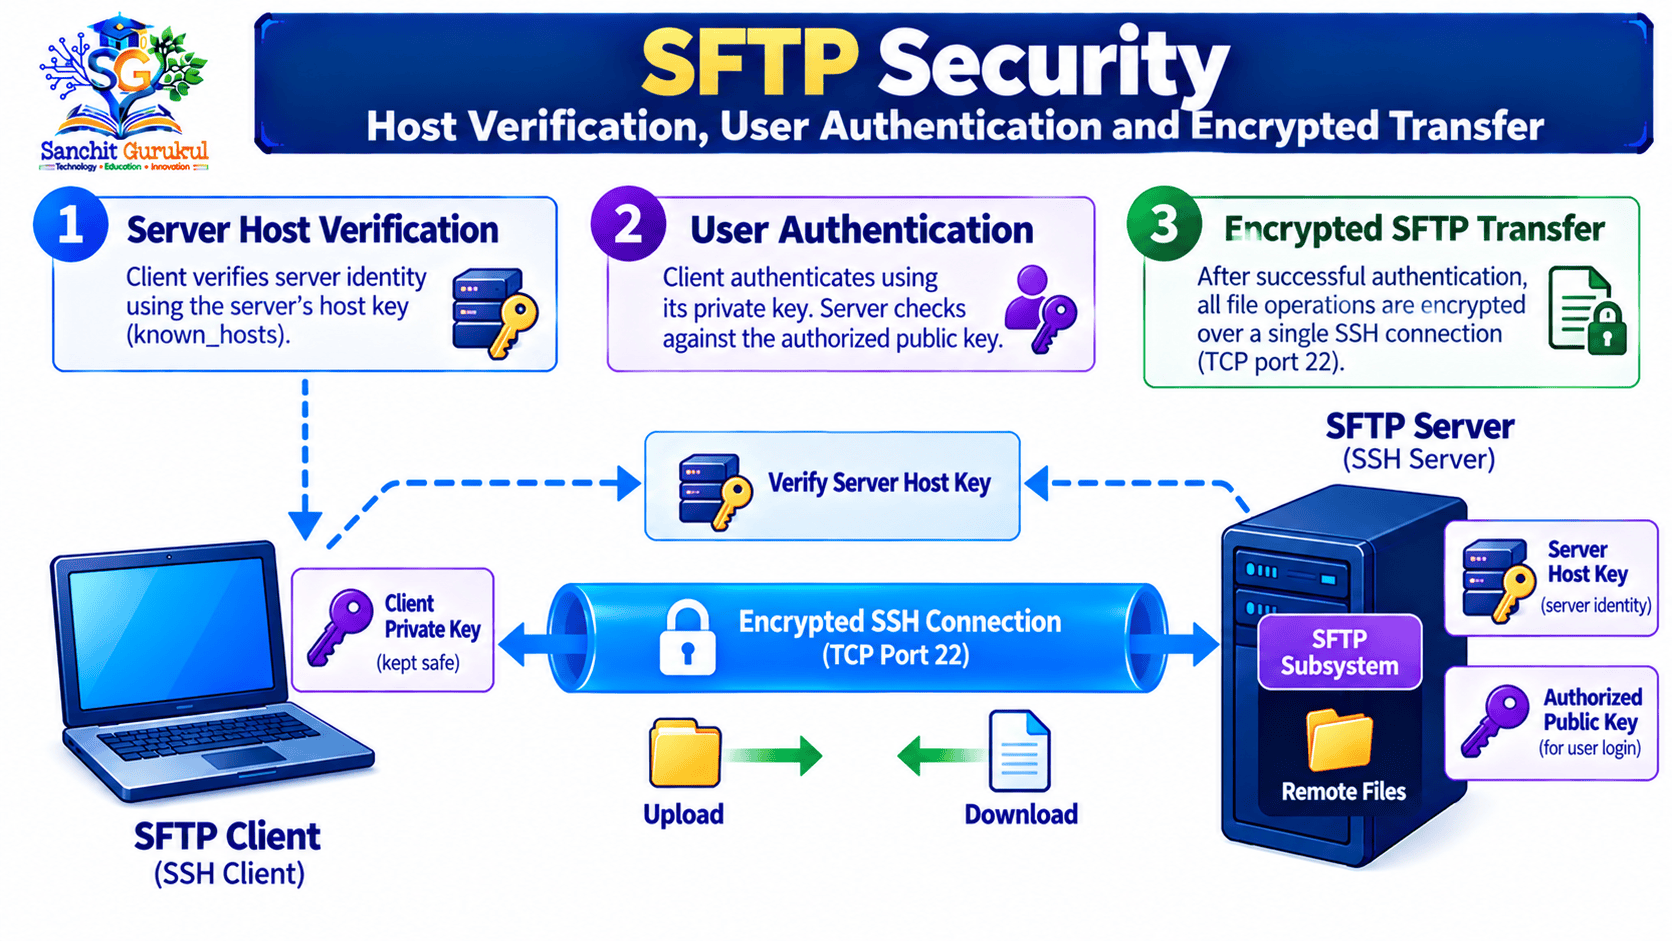
The SSH server presents its host-key identity during connection establishment.
The client needs to verify that the host key belongs to the intended server.
This helps defend against connections to an impersonating server.
On a first connection, a client may ask whether to trust an unfamiliar host key.
The fingerprint should be verified using an independent, trusted source before acceptance.
Step 4 — Authenticate the User
The server authenticates the user using an enabled SSH authentication method.
Common methods include:
- Password authentication
- Public-key authentication
- Other supported methods, depending on server policy
Successful authentication does not automatically grant access to every file.
The user must also have appropriate filesystem and server permissions.
Step 5 — Start the SFTP Subsystem
The client requests the SFTP service over an SSH channel.
A compatible SSH server starts or connects the request to its configured SFTP implementation.
For example, OpenSSH supports server-side implementations such as sftp-server and internal-sftp.
Step 6 — Perform File Operations
After the SFTP subsystem is available, the client can request operations such as:
- Open a file
- Read file contents
- Write file contents
- List a directory
- Rename a file
- Close a file
These operations are carried inside the SSH-protected connection.
Step 7 — Close the Session
When the user finishes, the SFTP client ends the session.
The SSH connection can then be closed.
Simplified SFTP Connection Flow
| Stage | What Happens |
|---|---|
| TCP Connection | Client connects to SSH server |
| SSH Negotiation | Security parameters are established |
| Host Verification | Client verifies server identity |
| User Authentication | Server authenticates the user |
| SFTP Subsystem | File-transfer functionality becomes available |
| File Operations | Files are uploaded, downloaded or managed |
| Session Closure | Client ends the session |

SFTP Authentication and Security — Passwords, SSH Keys and Integrity
One of SFTP’s main advantages is that it uses SSH security mechanisms.
However, secure operation still depends on correct configuration.
1. Password Authentication
The user supplies an account password.
SSH protects the authentication exchange inside the established encrypted transport.
This is different from traditional plaintext FTP authentication.
However, weak or reused passwords can still create account security risks.
2. Public-Key Authentication
Public-key authentication uses a related pair of cryptographic keys.
Private Key
Held securely by the user or client system.
It should not be shared.
Public Key
Registered with the server as an authorized authentication key.
During authentication, the client demonstrates possession of the appropriate private key without simply sending the private key to the server.
Why Use SSH Key-Based Authentication?
When configured and managed correctly, SSH keys can:
- Reduce reliance on account passwords
- Support authorized automation
- Resist some password-guessing attacks
- Support stronger authentication policies
However, keys must be protected.
A stolen or improperly managed private key can create significant risk.
3. Server Host-Key Verification
The SSH host key identifies the server.
It is different from the user’s authentication key.
| Key | Purpose |
|---|---|
| SSH Server Host Key | Helps establish the server’s identity |
| User Public Key | Used by the server to verify an authorized user |
| User Private Key | Used by the client to prove possession during authentication |
These keys should not be confused.
4. Encryption and Integrity Protection
SSH provides cryptographic protection for data carried through its secure connection.
This includes SFTP protocol messages and transferred file contents.
Modern SSH implementations may use authenticated encryption or compatible combinations of encryption and integrity protection.
Does SFTP Automatically Verify Every Completed File Using SHA-256?
No.
SSH protects data while it is transmitted through the secure connection.
That does not mean SFTP automatically calculates and compares an independent full-file SHA-256 checksum after every transfer.
If a workflow requires end-to-end file verification, the organization may need additional checks.
For example, an authorized administrator can compare trusted SHA-256 digests of the source and destination files.
This can help detect differences between the two completed files.
5. Permissions and Access Restrictions
SFTP authentication does not give users unlimited access to the server.
The server should enforce suitable restrictions, including:
- Authorized directories
- Read and write permissions
- Account separation
- File ownership
- Restricted SFTP-only access where appropriate
Practical Example — Connect to an SFTP Server and Transfer Files
This beginner-friendly exercise uses the OpenSSH command-line SFTP client.
Modern Windows, Linux and macOS environments may provide an OpenSSH client, although availability depends on the operating system and installed features.
Prerequisites
You need:
- An SFTP-capable server
- A valid authorized account
- The server hostname or IP address
- The configured SSH port
- Password or key-based access
- Appropriate file permissions
We will use these illustrative values:
| Setting | Example |
|---|---|
| Server | files.example.com |
| Username | student |
| TCP Port | 22 |
| Local File | example.txt |
| Remote Directory | uploads |
files.example.com is a placeholder, not a live SFTP training server.
Step 1 — Check the SFTP Client
Open a terminal.
Run:
sftp -hSome OpenSSH versions print usage information and exit with an error status because -h is not universally supported as a help option.
You can also run:
sftpWithout a destination, OpenSSH displays its usage information.
If the system reports that sftp is not recognized, check whether OpenSSH Client is installed and available in your command path.
Step 2 — Connect to the Server
Use:
sftp student@files.example.comThe client attempts an SSH connection to the server’s default port.
If this is the first connection, the client may require host-key verification.
After successful authentication, the interactive SFTP prompt is normally displayed.
sftp>This is illustrative; exact connection messages differ.
Step 3 — Check the Remote Directory
At the SFTP prompt, run:
pwdThis displays the current remote directory.
To list files:
lsStep 4 — Check the Local Directory
To display the local working directory:
lpwdTo list local files:
llsThe l prefix identifies these as local operations.
Step 5 — Upload a File
To upload a local file:
put example.txtThe client attempts to transfer example.txt to the current remote directory.
The operation requires a readable local file and suitable remote write permission.
Step 6 — Download a File
To download a remote file:
get example.txtThe client saves the file in the selected local destination.
Step 7 — Work with Remote Directories
Create a remote directory if permitted:
mkdir uploadsChange to that directory:
cd uploadsReturn to the previous directory as appropriate:
cd ..Step 8 — Rename a Remote File
rename example.txt example-backup.txtThis requires the original file to exist and the account to have the necessary permissions.
Step 9 — End the Session
byeThe SFTP session ends.
Common OpenSSH SFTP Commands
| Command | Purpose |
|---|---|
pwd |
Show current remote directory |
lpwd |
Show local working directory |
ls |
List remote files |
lls |
List local files |
cd |
Change remote directory |
lcd |
Change local directory |
get |
Download a file |
put |
Upload a file |
mkdir |
Create remote directory |
rename |
Rename remote file |
rm |
Delete remote file |
reget |
Attempt to resume a download |
reput |
Attempt to resume an upload |
bye |
Close the session |
Connecting to a Nonstandard SSH Port
If an authorized server uses TCP port 2222:
sftp -P 2222 student@files.example.comFor the OpenSSH SFTP command, uppercase -P specifies the remote port.
Connecting with an SSH Private Key
If you have an authorized private key:
sftp -i ~/.ssh/id_ed25519 student@files.example.comThe path is an example for Unix-like environments. On Windows, use the appropriate path to your private key.
Never copy or share the private key merely to troubleshoot an SFTP login.
Can SFTP Resume Interrupted Transfers?
Some SFTP clients support resuming partial transfers.
OpenSSH provides commands such as:
reget largefile.zipand:
reput largefile.zipHowever, resumption assumes that the existing partial file matches the corresponding portion of the source file.
If the files differ, the completed result may be corrupted.
Resumption also depends on permissions and implementation support.
For important files, validate the completed transfer.
SFTP vs FTP vs FTPS — Protocol and Security Comparison
FTP, FTPS and SFTP can all transfer files, but they use different protocols.
FTP
Traditional FTP uses separate control and data TCP connections.
It normally uses server TCP port 21 for control communication.
Plain FTP does not provide encryption.
FTPS
FTPS adds TLS protection to FTP.
It retains FTP’s control and data connection architecture.
Security depends on proper TLS configuration for the required channels.
SFTP
SFTP uses an SSH-protected connection.
It does not use FTP’s PORT, PASV or EPSV commands.
Detailed Comparison
| Feature | FTP | FTPS | SFTP |
|---|---|---|---|
| Underlying Protocol | FTP | FTP with TLS | SSH File Transfer Protocol |
| Encryption | No, by default | TLS when configured | SSH |
| Common TCP Port | 21 | 21 explicit; 990 implicit | 22 |
| Separate FTP Control and Data Connections | Yes | Yes | No |
| Active and Passive FTP Modes | Yes | Yes | Not applicable |
| SSH Public-Key Authentication | No | Not inherent to FTPS | Supported through SSH |
| Firewall Configuration | Multiple connection considerations | Multiple connection considerations | Usually one SSH connection |
| Suitable for Confidential Files | No | With secure configuration | With secure configuration |
Why Is SFTP Often Easier for Firewalls?
FTP requires a separate data connection in addition to its control connection.
SFTP normally transfers both its protocol messages and file contents over the existing SSH connection.
This often simplifies firewall requirements.
For example, an organization may permit approved clients to connect to an SSH server on TCP port 22.
No separate FTP passive-port range is needed for those SFTP sessions.
However, SFTP still requires:
- Correct routing
- Firewall permission
- A working SSH service
- Successful authentication
- Appropriate server access controls
Is SFTP Always Faster Than FTP?
No.
SFTP encrypts its traffic, which introduces processing requirements.
Actual transfer performance depends on factors such as network bandwidth, latency, file size, server capacity, SSH algorithms and client implementation.
SFTP’s primary benefit is secure file transfer rather than guaranteed speed.

SFTP Use Cases, Benefits, Limitations and Troubleshooting
SFTP is used wherever organizations need controlled, secure file exchange.
Common SFTP Use Cases
1. Website Administration
Uploading authorized website files and downloading server content.
2. Secure Business File Exchange
Transferring documents between approved business systems.
3. Backup Transfer
Moving backup archives to authorized remote systems.
4. Network and Server Administration
Transferring configuration backups, log files and other administrative data.
5. Automated Workflows
Running scheduled file transfers using supported client tools and authentication methods.
6. Sensitive Data Exchange
Supporting secure transfer requirements in environments such as finance and healthcare, subject to applicable policies and regulations.
Benefits of SFTP
Encrypted Communication
SSH protects transferred information from ordinary network eavesdropping.
Integrity Protection in Transit
SSH helps detect unauthorized modification of protected connection data.
Authentication
SSH supports authentication mechanisms such as public keys and passwords.
Simplified Network Connectivity
A typical SFTP session does not require additional FTP data ports.
Remote File Management
SFTP can perform multiple file operations through the protected connection.
Automation Support
Clients and servers can support noninteractive file transfers when configured securely.
Limitations of SFTP
SSH Configuration Required
A compatible SSH service and SFTP implementation are needed.
Key Management
Authentication keys require secure storage, rotation and revocation procedures.
Permission Problems
A valid login does not guarantee write access to every directory.
Resource Usage
Encryption and file operations consume computing resources.
Client Compatibility
Not every client supports every SFTP extension or protocol feature.
Interrupted Transfers
Resumption capabilities vary and require validation.
Common SFTP Problems
| Problem | Possible Cause |
|---|---|
| Connection timed out | Firewall, routing or unavailable server |
| Connection refused | Wrong port or SSH service not listening |
| Permission denied | Authentication failure or access restrictions |
| Host key verification failed | Server identity mismatch or key change |
| SSH works but SFTP fails | SFTP subsystem unavailable or restricted |
| Upload fails | Remote permissions, quota or storage capacity |
| Download fails | File missing or insufficient read permission |
| Slow transfer | Network or endpoint performance limitations |
SFTP Troubleshooting — Step by Step
Step 1 — Verify the Server and Port
Confirm that the correct hostname and TCP port are configured.
Step 2 — Confirm Network Connectivity
Check routing, firewall and server availability.
Step 3 — Review SSH Authentication
Determine whether the server permits the chosen authentication method.
Step 4 — Verify the Server Host Key
Investigate any host-key mismatch instead of bypassing verification.
Step 5 — Confirm SFTP Service Support
Check that the SSH server provides the required SFTP subsystem.
Step 6 — Check File Permissions
Verify the user’s read, write and directory access permissions.
Step 7 — Review Logs
Use authorized client and server logs to identify the failed stage.
Using Verbose SFTP Diagnostics
OpenSSH provides a verbose option:
sftp -v student@files.example.comThis can provide additional information about connection establishment and authentication.
For more detailed diagnostics, OpenSSH supports additional verbosity options.
Do not share unreviewed diagnostic logs publicly because they may contain usernames, addresses, paths and other sensitive details.
SFTP Security Best Practices
- Verify SSH server host keys.
- Use strong authentication and protect private keys.
- Restrict accounts to necessary directories and operations.
- Keep SSH server software updated.
- Disable unnecessary access methods according to policy.
- Monitor authentication failures and file-transfer activity.
- Protect stored files and backups.
- Verify completed files when independent integrity assurance is required.
- Review automated transfer credentials and permissions regularly.
Key Takeaways
Core SFTP Concepts
- SFTP stands for SSH File Transfer Protocol.
- It is a separate protocol from FTP.
- It commonly operates over SSH on TCP port 22.
- It does not use active or passive FTP data connections.
- An SSH server must support SFTP functionality.
How SFTP Works
- The client establishes an SSH connection.
- The server’s identity should be verified.
- SSH authenticates the user.
- The client requests the SFTP subsystem.
- File operations occur over the protected SSH connection.
Security and Authentication
- SSH provides encryption and integrity protection in transit.
- Password and public-key authentication are commonly supported.
- User private keys must remain protected.
- SSH host keys identify servers.
- SFTP does not automatically provide an independent full-file checksum comparison.
Operations and Troubleshooting
- SFTP supports uploads, downloads and remote file management.
- OpenSSH provides commands such as
get,put,lsandpwd. - Some interrupted transfers can be resumed.
- File permissions affect available operations.
- Connection errors, authentication errors and subsystem failures should be investigated separately.
SFTP is a widely used solution for secure file transfer.
It allows users and applications to upload, download and manage remote files through SSH-protected communication.
Its main security features come from SSH, including encrypted communication, integrity protection and authentication.
Unlike traditional FTP, SFTP does not require separate control and data connections or active/passive data connection negotiation.
This often makes firewall configuration simpler.
However, SFTP security still depends on proper authentication, trusted host keys, appropriate permissions and secure server configuration.
For beginners, the most important concepts are understanding how SSH protects the connection, how the SFTP subsystem handles files, and why SFTP is different from FTP and FTPS.
Next in This Series: SFTP Authentication Explained — Password vs SSH Keys, Host-Key Verification and Secure File Transfer.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


