
A zero-day vulnerability is a security weakness that defenders or the affected vendor did not previously know about when attackers begin exploiting it.
A zero-day exploit is the code, technique, or method used to take advantage of that vulnerability.
A zero-day attack occurs when the exploit is actually used against a target.
These attacks are especially challenging because defenders may initially have:
- No vendor patch
- Limited indicators of compromise
- Incomplete understanding of the vulnerability
- No mature detection signature
- Limited time to assess exposure
However, a zero-day vulnerability does not mean an organization is completely defenseless.
Security controls such as:
- Endpoint detection and response
- Network segmentation
- Least privilege
- Application control
- Behavioral monitoring
- Intrusion prevention
- WAF protections
- Attack-surface reduction
- Strong authentication
may still prevent exploitation or limit the attack’s impact.
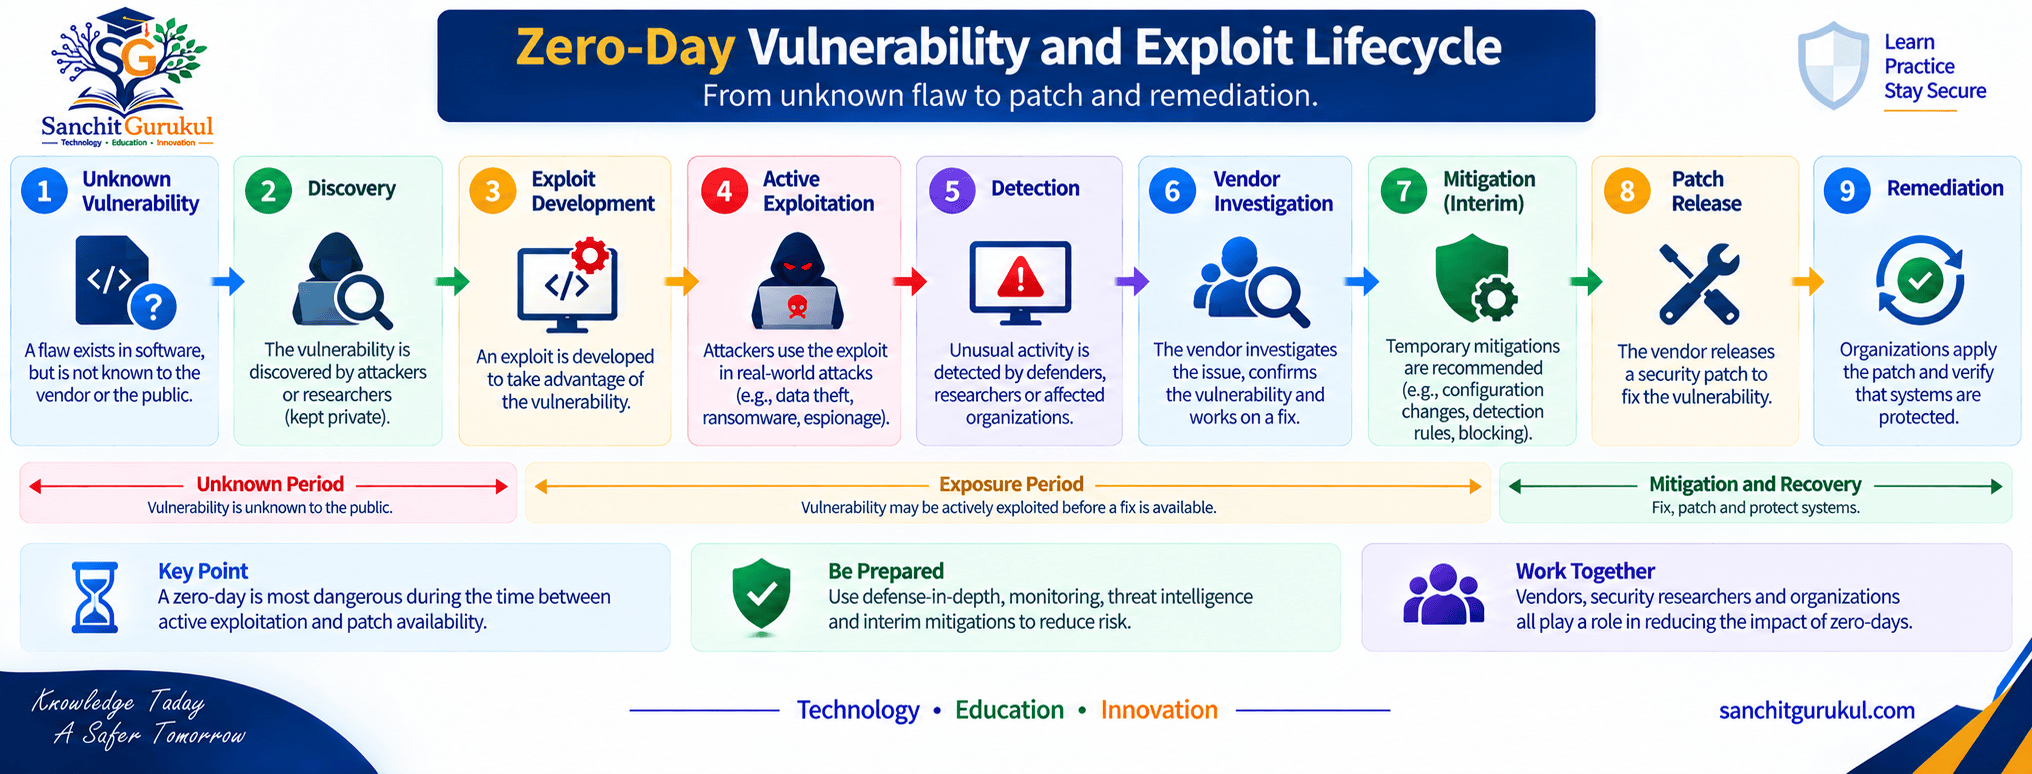
What Is a Zero-Day Vulnerability, Exploit and Attack?
The terms vulnerability, exploit, and attack are often incorrectly used as if they mean the same thing.
They describe different parts of the security problem.
Zero-Day Vulnerability
A vulnerability is a weakness in:
- Software
- Firmware
- Hardware
- Security controls
- System design
- Implementation
that could be exploited to compromise security.
A zero-day vulnerability is generally one that was previously unknown to the organization responsible for correcting it when exploitation begins.
Examples could involve:
- Memory corruption
- Authentication bypass
- Privilege escalation
- Remote code execution
- Sandbox escape
- Improper access control
- Command injection
Zero-Day Exploit
An exploit is a method that takes advantage of the vulnerability.
An exploit might allow an attacker to:
- Execute code
- Gain additional privileges
- Bypass authentication
- Escape a security boundary
- Read protected information
- Modify system data
A vulnerability may exist for years without anyone publicly knowing how to exploit it.
Zero-Day Attack
A zero-day attack occurs when someone actively uses a zero-day exploit against a target.
The relationship can therefore be understood as:
| Term | Meaning |
|---|---|
| Zero-Day Vulnerability | Previously unknown security weakness |
| Zero-Day Exploit | Technique or code that exploits the weakness |
| Zero-Day Attack | Actual malicious use of the exploit |
| Patch | Vendor remediation correcting the weakness |
| Mitigation | Temporary or permanent control reducing exploitation risk |
Zero-Day vs Known Vulnerability
Once a vulnerability has been publicly disclosed and defenders understand it, it is normally considered a known vulnerability rather than an undisclosed zero-day.
A CVE identifier may then be assigned.
Example:
CVE-YYYY-NNNNNHowever:
Having a CVE does not mean a vulnerability is being actively exploited.
Likewise:
Not every actively exploited vulnerability originally began as a publicly observed zero-day.
CISA maintains the Known Exploited Vulnerabilities Catalog, or KEV, to identify vulnerabilities with evidence of exploitation in the wild.
How Zero-Day Exploitation Happens
Zero-day attacks do not all follow an identical path, but several stages are commonly seen.
Vulnerability Exists
The vulnerability may have been introduced during:
- Software development
- Firmware development
- Hardware design
- Feature implementation
- Integration of third-party components
It may remain undiscovered for months or years.
Vulnerability Discovery
The weakness might be discovered by:
- Security researchers
- Product developers
- Threat actors
- Intelligence organizations
- Penetration testers
- Automated fuzzing systems
Discovery does not automatically mean exploitation.
A security researcher may responsibly disclose the vulnerability to the vendor before publishing details.
An attacker may instead keep the vulnerability secret.
Exploit Development
An attacker may determine how to reliably trigger the vulnerability.
Depending on the vulnerability, successful exploitation might result in:
- Remote code execution
- Privilege escalation
- Information disclosure
- Authentication bypass
- Security-control bypass
Some vulnerabilities are easy to exploit.
Others require very specific:
- Operating systems
- Application versions
- Memory layouts
- User actions
- Privilege levels
- Configurations
Therefore, not every zero-day vulnerability produces a practical exploit.
Initial Exploitation
An attacker may deliver the exploit through vectors such as:
- Malicious websites
- Phishing
- Compromised documents
- Internet-facing services
- Messaging applications
- Removable media
- Supply-chain compromise
The delivery mechanism and the exploited vulnerability are separate concepts.
For example, phishing might deliver a file containing an exploit.
Post-Exploitation
Successful exploitation may only be the first stage.
An attacker might then attempt:
- Credential theft
- Persistence
- Privilege escalation
- Lateral movement
- Command-and-control communication
- Data collection
- Data exfiltration
This is why preventing exploitation is only one part of the defense.
Discovery by Defenders
Security teams may discover exploitation through:
- EDR telemetry
- Crash analysis
- Malware analysis
- Network anomalies
- Threat intelligence
- Incident response
- Vendor investigation
- Security research
At this point, defenders may still have no patch.
Vendor Mitigation
The vendor may publish temporary measures such as:
- Disable a vulnerable feature
- Restrict network access
- Apply configuration changes
- Disable an affected service
- Add detection rules
- Remove a component
- Apply a temporary workaround
Patch Release
After understanding the root cause, the vendor can develop and test a security update.
Organizations should then prioritize deployment according to:
- Active exploitation
- Asset criticality
- Internet exposure
- Vulnerability impact
- Existing mitigations
Why Zero-Day Exploits Are Dangerous
Zero-day attacks can be difficult to stop because traditional defenses may initially lack exact signatures or vulnerability-specific rules.
No Immediate Patch
If the vendor has not yet developed a fix, organizations must rely on compensating controls.
Examples include:
- Network restrictions
- Feature disablement
- WAF rules
- IPS signatures
- Endpoint controls
- Application allowlisting
- Isolation
Signature-Based Detection May Initially Miss It
Traditional signature-based systems are strongest when they already know what to detect.
A completely new exploit may not initially match an existing signature.
However, this does not mean EDR, IDS/IPS, SIEM, or network security products are useless.
They may still detect:
- Unusual process execution
- Suspicious child processes
- Memory exploitation behavior
- Privilege escalation
- Unexpected network connections
- Command-and-control activity
- Lateral movement
Attackers Can Chain Vulnerabilities
A single vulnerability may not provide everything an attacker needs.
For example, one exploit might provide initial code execution while another provides:
- Higher privileges
- Sandbox escape
- Persistence
This is sometimes described as an:
Exploit chain
High-Value Targets
Zero-days can be especially valuable when they affect widely deployed technologies such as:
- Browsers
- Operating systems
- VPN gateways
- Firewalls
- Email servers
- Mobile devices
- Network appliances
- Cloud infrastructure
Internet-facing systems deserve particular attention because attackers may be able to reach them without first gaining internal network access.
Historical Example — Stuxnet
Stuxnet remains one of the best-known historical examples of sophisticated exploitation.
CISA’s archived ICS analysis reported that Stuxnet used:
Four zero-day exploits
along with additional vulnerabilities and propagation techniques.
It spread using mechanisms including:
- Removable media
- Network shares
- Windows Print Spooler exploitation
- STEP 7-related mechanisms
The malware interacted with Siemens industrial automation software.
The most important lesson for defenders is broader than the specific malware:
Sophisticated attacks can combine multiple vulnerabilities, propagation mechanisms and post-exploitation capabilities.
Defense Against Zero-Day Threats
There is no single product that can guarantee protection against every unknown vulnerability.
A more effective strategy is:
Defense in depth
The goal is to make successful exploitation harder and reduce the damage if one security control fails.

Reduce Internet Exposure
Internet-facing systems should be limited to services that genuinely require external access.
Review:
- Public IP addresses
- Remote-management interfaces
- VPN portals
- Administrative services
- Cloud services
- Legacy applications
CISA recommends reducing unnecessary internet exposure and continuously reviewing internet-accessible assets.
Network Segmentation
Segmentation can reduce the blast radius of a successful exploit.
Separate high-value environments such as:
- Management networks
- Servers
- User networks
- Backup infrastructure
- OT/ICS
- Security systems
Apply access controls between segments.
An exploited endpoint should not automatically have unrestricted access to every other system.
Least Privilege
Reduce the permissions available to:
- Users
- Applications
- Service accounts
- Administrative accounts
If exploitation occurs under a restricted account, additional privilege escalation may be required before an attacker gains broader control.
Application Allowlisting
Application allowlisting can limit which software is permitted to execute.
This can help restrict:
- Unknown executables
- Unauthorized scripts
- Malicious tools
It should be carefully designed and tested to avoid disrupting legitimate applications.
Endpoint Detection and Response
EDR can provide visibility into behavior occurring after exploitation.
Useful detections may include:
- Suspicious process trees
- Memory manipulation
- Credential access
- Unexpected PowerShell activity
- Privilege escalation
- Persistence mechanisms
IDS and IPS
Network detection controls may identify:
- Exploit patterns
- Command-and-control traffic
- Scanning
- Suspicious protocol behavior
Once a zero-day becomes understood, security vendors may publish signatures before the affected product vendor completes a patch.
Web Application Firewall
For vulnerabilities exposed through web applications, a WAF may provide temporary protections by blocking known malicious request patterns.
This is often called:
Virtual patching
Security Monitoring
Monitor high-value assets using:
- SIEM
- EDR
- NDR
- Firewall logs
- Authentication logs
- DNS logs
- Proxy logs
- Application logs
Look for behavior that differs from normal operations.
Backups
Reliable backups may not prevent exploitation, but they can significantly improve recovery from attacks involving:
- Ransomware
- Data destruction
- Configuration corruption
Backups should be:
- Protected
- Separated from normal user access
- Regularly tested
Keep Systems Updated
Patching cannot prevent exploitation of a vulnerability that no one knows about.
However, maintaining current systems still matters because attackers frequently combine new techniques with older vulnerabilities.
An attacker should not be able to use a zero-day for initial access and then use a five-year-old unpatched vulnerability for privilege escalation.
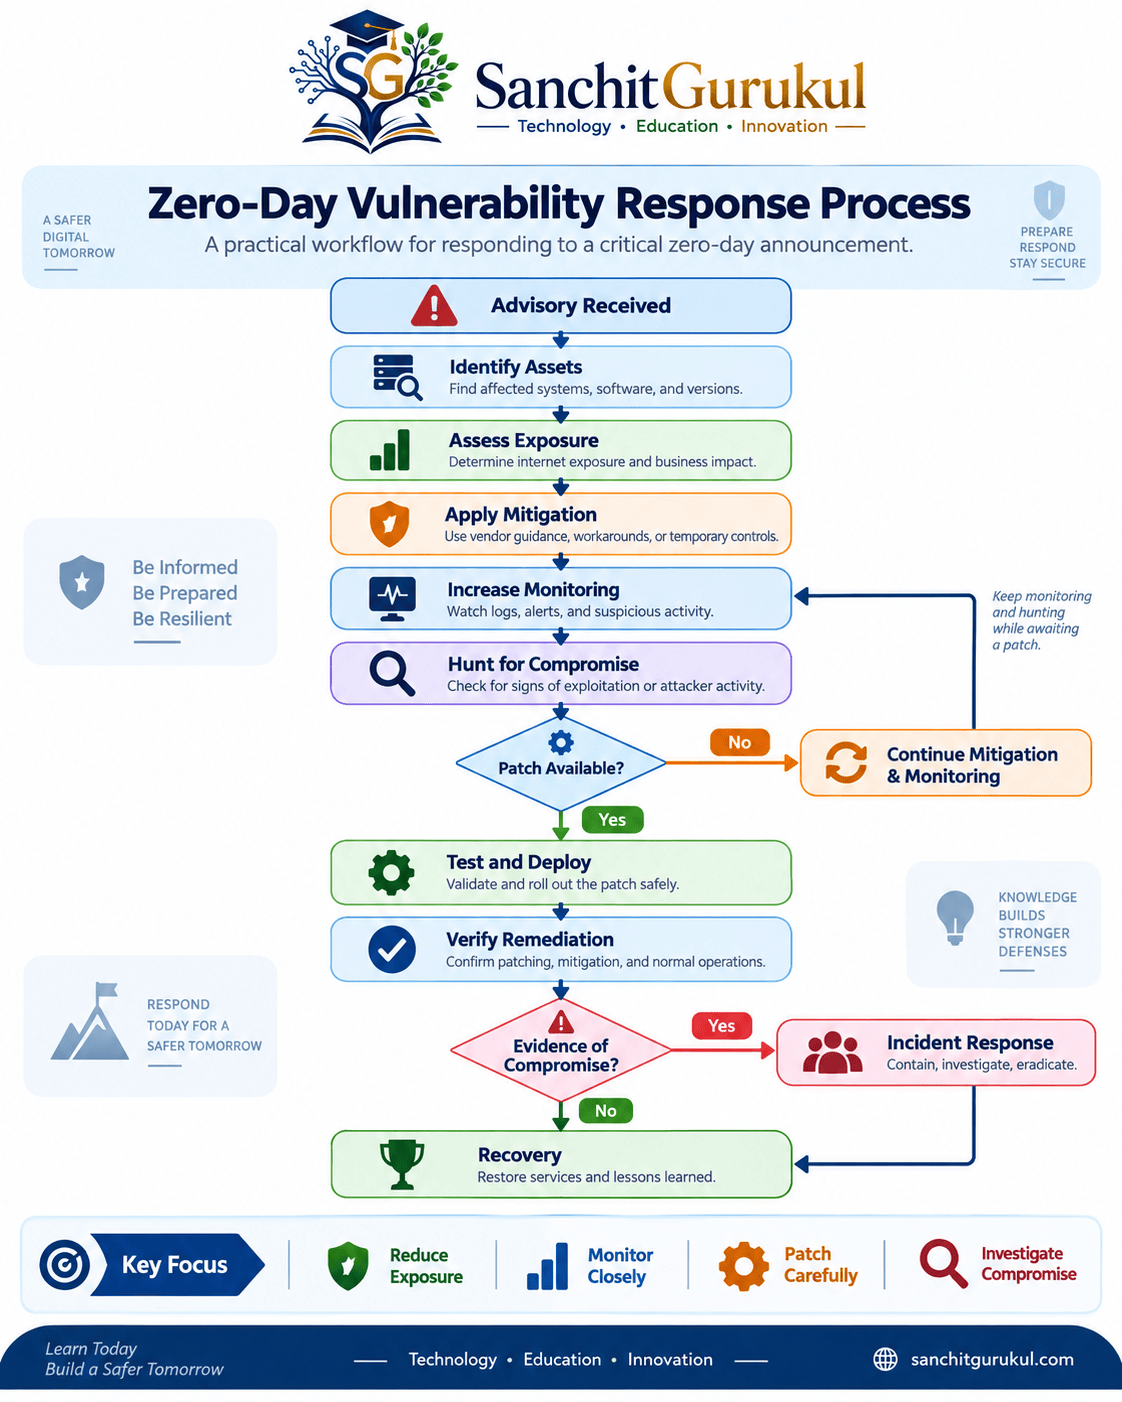
Responding When a Zero-Day Is Announced
When a critical zero-day becomes public, organizations may have only limited information.
A structured response is more effective than making random configuration changes.
Step 1 — Determine Exposure
Identify:
- Affected product
- Vulnerable versions
- Number of affected assets
- Internet-facing systems
- Critical business systems
- Privileged systems
Do not assume your vulnerability scanner immediately knows about a newly disclosed issue.
Use:
- Asset inventory
- Software inventory
- CMDB
- Cloud inventory
- Network discovery
Step 2 — Review Vendor Guidance
Use the vendor’s official:
- Security advisory
- Mitigation guidance
- Detection guidance
- Patch information
Avoid relying only on social-media summaries.
Step 3 — Check Active Exploitation
Review trusted sources such as:
- CISA Known Exploited Vulnerabilities Catalog
- Vendor security advisories
- National CERT advisories
- Trusted threat intelligence
Active exploitation should significantly increase remediation priority.
Step 4 — Apply Temporary Mitigations
If no patch exists, possible actions may include:
- Disable the vulnerable feature.
- Restrict external access.
- Isolate the system.
- Apply WAF or IPS rules.
- Remove public exposure.
- Restrict management interfaces.
- Increase endpoint monitoring.
Always follow product-specific guidance.
Step 5 — Increase Monitoring
Search for:
- Known indicators of compromise
- Suspicious authentication
- Unexpected processes
- New accounts
- Configuration changes
- Network connections
- Privilege changes
Do not search only for one IOC.
Attackers can change:
- IP addresses
- Domains
- File names
- File hashes
Behavioral investigation is also important.
Step 6 — Patch When Available
NIST describes enterprise patch management as identifying, prioritizing, acquiring, installing and verifying patches and updates.
For a critical actively exploited vulnerability:
- Obtain the update from the vendor.
- Validate compatibility where operationally possible.
- Prioritize exposed and critical assets.
- Deploy the patch.
- Verify successful installation.
- Confirm the vulnerability is no longer exposed.
Step 7 — Investigate Previous Exposure
Installing the patch does not prove that the system was never compromised.
If exploitation occurred before remediation, the attacker may already have established:
- Persistence
- Additional accounts
- Malware
- Stolen credentials
Organizations should therefore investigate potentially exposed systems.
Step 8 — Follow the Incident Response Process
If compromise is suspected, activate the organization’s incident response process.
NIST SP 800-61 Rev. 3 emphasizes integrating incident response throughout cybersecurity risk management so organizations can prepare for, detect, respond to and recover from incidents.
Key Takeaways and Summary
Key Takeaways
- A zero-day vulnerability is the underlying security weakness; a zero-day exploit is the method used to exploit it.
- A zero-day attack is the actual use of that exploit against a target.
- Zero-day does not simply mean that an individual organization has failed to install an existing patch.
- A zero-day may not initially have a CVE identifier or mature security signatures.
- No available patch does not mean there are no defenses; compensating controls can significantly reduce risk.
- Segmentation, least privilege, attack-surface reduction, EDR, IPS and monitoring help limit zero-day exploitation and post-exploitation activity.
- WAF and IPS rules can provide temporary virtual-patching protection, but they do not remove the underlying vulnerability.
- CISA’s KEV Catalog is useful for identifying vulnerabilities with confirmed exploitation in the wild.
- Once a patch is available, remediation should be prioritized according to exploitation, exposure and asset criticality.
- Patching a compromised system is not enough by itself—organizations should investigate whether exploitation occurred before remediation.
Summary
Zero-day exploits represent one of the most challenging areas of cybersecurity because defenders may initially be responding to a vulnerability they do not fully understand.
The basic lifecycle involves:
Unknown vulnerability → discovery → exploit development → exploitation → detection → mitigation → patching → recovery
But successful defense should begin long before a specific zero-day is discovered.
Organizations can reduce risk through:
- Small attack surfaces
- Secure configurations
- Network segmentation
- Least privilege
- Strong authentication
- Endpoint protection
- Application control
- Centralized monitoring
- Vulnerability management
- Reliable backups
- Incident-response planning
When a critical zero-day becomes known, the immediate objective is not simply:
“Wait for the patch.”
The better response is:
Identify exposure → reduce attack surface → apply mitigations → increase monitoring → investigate compromise → deploy the patch → verify remediation.
Zero-day vulnerabilities cannot always be prevented from existing.
What organizations can control is how difficult those vulnerabilities are to exploit, how far an attacker can move after exploitation, how quickly the attack is detected, and how effectively affected systems can be recovered.
That is the foundation of resilient defense against zero-day threats.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.
