
IPv6 does not use the IPv4 Address Resolution Protocol — ARP.
Instead, IPv6 uses Neighbor Discovery Protocol — NDP, which is carried through ICMPv6.
NDP performs several important functions on an IPv6 network, including:
- Discovering neighboring devices
- Resolving IPv6 addresses to link-layer addresses
- Discovering routers
- Learning network prefixes
- Detecting duplicate addresses
- Verifying neighbor reachability
- Identifying better first-hop paths
On Ethernet, the link-layer address is normally a:
MAC address
but Neighbor Discovery itself is defined more generally in terms of link-layer addresses.
NDP is therefore much more than an IPv6 replacement for ARP.
It combines several functions that IPv4 implements through separate mechanisms.
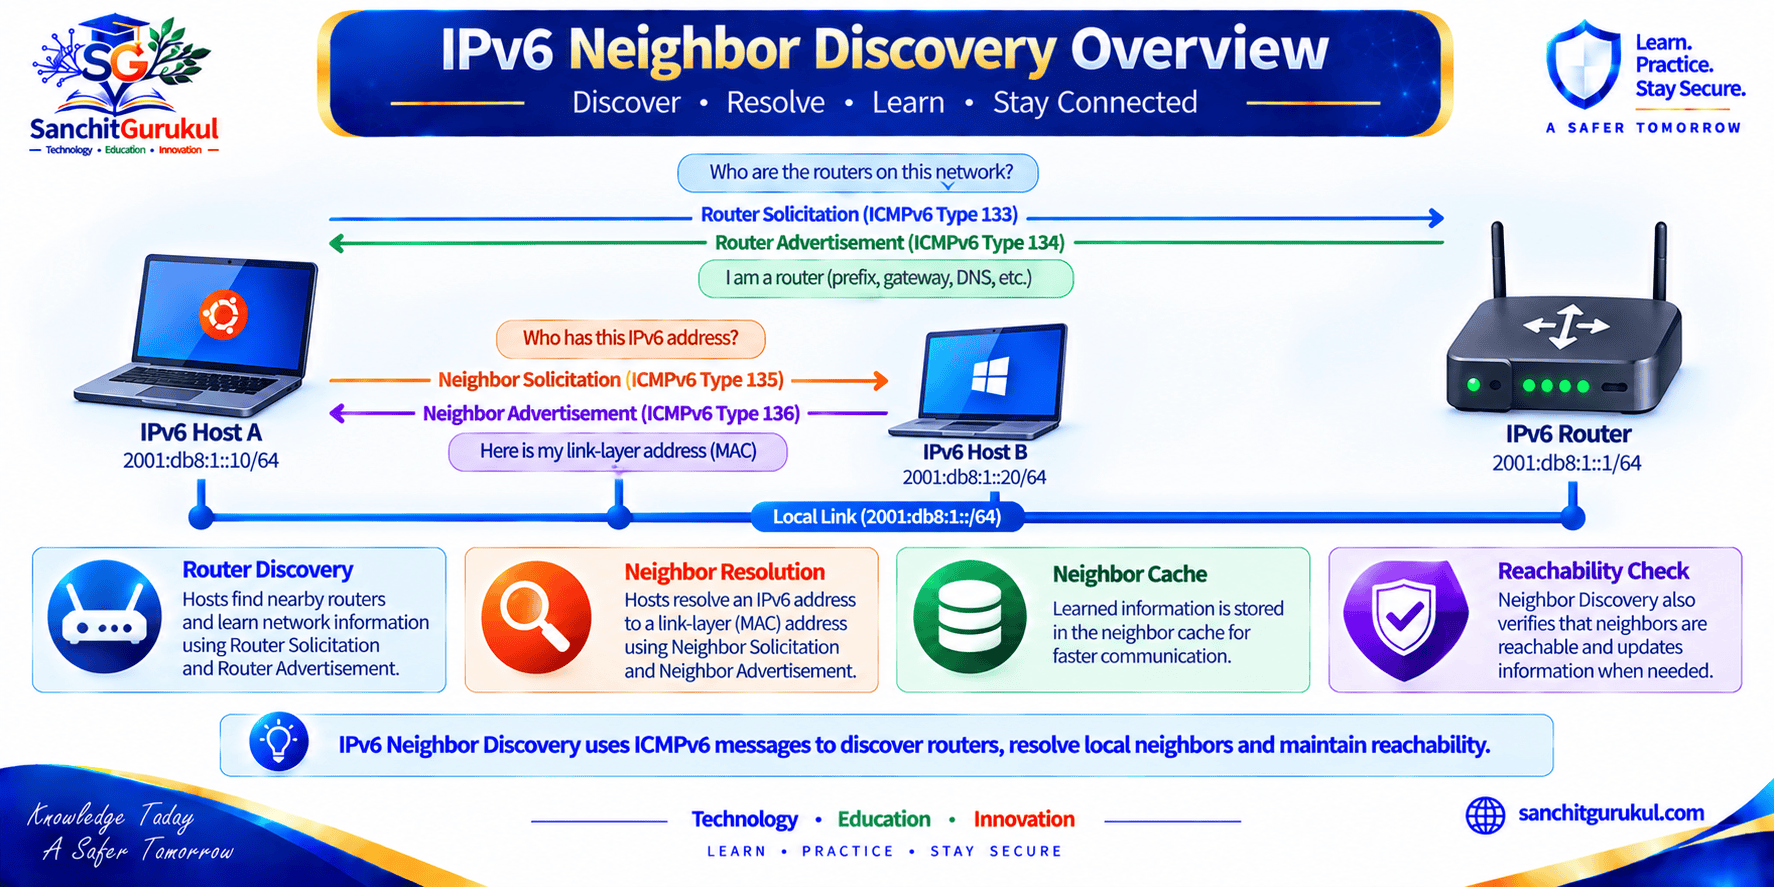
Understanding IPv6 Neighbor Discovery
Neighbor Discovery is primarily defined by RFC 4861.
It uses five ICMPv6 message types.
| NDP Message | ICMPv6 Type | Primary Purpose |
|---|---|---|
| Router Solicitation | 133 | Ask local routers to advertise |
| Router Advertisement | 134 | Advertise router and link information |
| Neighbor Solicitation | 135 | Resolve or verify a neighbor |
| Neighbor Advertisement | 136 | Advertise neighbor information |
| Redirect | 137 | Inform a host about a better first hop |
Router Solicitation — RS
When a host first connects to an IPv6 network, it may not want to wait for the next periodic Router Advertisement.
It can send a:
Router Solicitation
to:
ff02::2This is the IPv6:
All-Routers multicast address
The message effectively asks:
Are there IPv6 routers on this link?
A typical RS may use:
Source:
Host IPv6 address

Destination:
ff02::2

ICMPv6 Type:
133
If the host does not yet have a suitable source address, the unspecified IPv6 address may be used:
::Router Advertisement — RA
IPv6 routers send:
Router Advertisements
periodically and may also send them in response to a Router Solicitation.
A typical unsolicited RA is sent to:
ff02::1which is the:
All-Nodes multicast address
The source address of a valid Router Advertisement is normally the router’s link-local IPv6 address.
Example:
Source:
fe80::1

Destination:
ff02::1

ICMPv6 Type:
134
An RA can contain information such as:
- Prefix Information
- Router Lifetime
- Current Hop Limit
- Reachable Time
- Retransmission Timer
- MTU
- SLAAC information
- Managed and Other configuration flags
RA Does Not Contain a Traditional Gateway Field
A common misconception is that an IPv6 Router Advertisement contains a field similar to the IPv4 DHCP:
Default Gateway
It does not.
Instead, the host receives an RA from a router.
If the Router Lifetime indicates that the router is eligible to act as a default router, the host can add the RA sender’s IPv6 address to its default-router list.
This is normally the router’s link-local address.
For example:
Default Router:
fe80::1
This is why an IPv6 routing table may show:
default via fe80::1 dev ens18How IPv6 Address Resolution Works
Address resolution determines the link-layer address required to transmit a packet on the local network.
IPv4 commonly uses:
ARP Request + ARP Reply
IPv6 instead uses:
Neighbor Solicitation + Neighbor Advertisement
First Determine Whether the Destination Is On-Link
Before performing address resolution, the host must determine whether the destination is directly reachable on the local link.
Suppose the host is:
2001:db8:10::10/64and wants to communicate with:
2001:db8:10::25Both addresses belong to:
2001:db8:10::/64The destination is therefore expected to be on the local link.
The sender must discover the destination’s link-layer address.
Neighbor Solicitation — NS
The sender creates a Neighbor Solicitation.
Example:
Source IPv6:
2001:db8:10::10

Target IPv6:
2001:db8:10::25

ICMPv6 Type:
135
Instead of broadcasting the request to every device, IPv6 normally sends address-resolution NS messages to the target’s:
Solicited-Node Multicast Address
For:
2001:db8:10::25the solicited-node multicast address is:
ff02::1:ff00:25This reduces unnecessary processing compared with sending a request to every IPv6 node on the LAN.
Solicited-Node Multicast
Solicited-node multicast uses the prefix:
ff02::1:ff00:0/104combined with the lower 24 bits of the target IPv6 address.
On Ethernet, the corresponding multicast MAC address begins with:
33:33:ffFor this example, it would map to:
33:33:ff:00:00:25Neighbor Advertisement — NA
The device owning:
2001:db8:10::25responds with a:
Neighbor Advertisement
The response can contain the device’s target link-layer address.
Example:
Target IPv6:
2001:db8:10::25

Target MAC:
00:1a:2b:3c:4d:5e

ICMPv6 Type:
136
The sender can then create or update its:
Neighbor Cache
If the Destination Is Remote
Suppose the host:
2001:db8:10::10/64needs to reach:
2001:db8:20::50The destination is not on the local /64.
The host does not perform Neighbor Discovery for the remote server’s MAC address.
Instead, it selects a router from its routing information.
Assume the next hop is:
fe80::1The host resolves the router’s link-layer address and sends the Ethernet frame to that router.
The IPv6 packet still has:
IPv6 Destination:
2001:db8:20::50
but the local Ethernet frame is addressed to the next-hop router.

DAD, Neighbor Reachability and Redirects
Neighbor Discovery continues to operate after basic address resolution.
Duplicate Address Detection — DAD
Before most IPv6 unicast addresses become fully usable on an interface, the node normally checks whether another device is already using the address.
This process is called:
Duplicate Address Detection
The address being checked is treated as:
Tentative
during DAD.
DAD Neighbor Solicitation
Suppose a host intends to use:
2001:db8:10::25It sends a Neighbor Solicitation with:
Source IPv6:
::

Target IPv6:
2001:db8:10::25

Destination:
Solicited-node multicast address of the target
The source is:
::because the tentative address cannot yet be used normally as a source address.
What Indicates a Duplicate?
If another node already owns that address, the DAD process may receive a Neighbor Advertisement indicating a conflict.
DAD also accounts for the situation where two nodes are simultaneously testing the same tentative address.
If a duplicate is detected, the tentative address must not be used normally.
If the required DAD process completes without evidence of a duplicate, the address can become usable.
Neighbor Unreachability Detection — NUD
Finding a neighbor’s link-layer address once does not guarantee that the neighbor remains reachable forever.
IPv6 uses:
Neighbor Unreachability Detection
to determine whether the forward path to a neighbor is still working.
Reachability may be confirmed by:
- Upper-layer protocol information
- Solicited Neighbor Advertisements
If necessary, the node probes the neighbor using Neighbor Solicitation messages.
Neighbor Cache States
Linux and other IPv6 implementations maintain states similar to:
| State | Meaning |
|---|---|
| INCOMPLETE | Address resolution is still in progress |
| REACHABLE | Neighbor was recently confirmed reachable |
| STALE | Entry exists but recent reachability is not confirmed |
| DELAY | System is waiting before actively probing |
| PROBE | Unicast reachability probes are being sent |
| FAILED | Address resolution or reachability failed |
These states are extremely useful during troubleshooting.
Redirect Messages
An IPv6 router may send:
ICMPv6 Redirect — Type 137
to inform a host that a better first hop exists.
For example, the host sends traffic through Router A, but Router A knows that another router on the same link is a better next hop.
A Redirect may also tell the host that the destination itself is actually on-link.
Hosts do not send IPv6 Redirect messages.
Redirect processing must follow the validation rules defined by Neighbor Discovery.
Observing and Troubleshooting Neighbor Discovery
NDP can be inspected directly on Linux and in Wireshark.
View the Linux Neighbor Cache
ip -6 neigh showExample:
2001:db8:10::25 dev ens18 lladdr 00:1a:2b:3c:4d:5e REACHABLE
fe80::1 dev ens18 lladdr 00:50:56:aa:bb:cc STALE
This shows:
- Neighbor IPv6 address
- Interface
- Link-layer address
- Neighbor state
Inspect One Interface
ip -6 neigh show dev ens18Check IPv6 Routes
ip -6 route showThis is important because the route determines which neighbor needs to be resolved.
Check the Selected Next Hop
ip -6 route get 2001:db8:20::50Example:
2001:db8:20::50 via fe80::1 dev ens18 src 2001:db8:10::10The important next-hop neighbor is:
fe80::1Capture NDP Traffic with tcpdump
Capture ICMPv6:
sudo tcpdump -nn -i ens18 icmp6A more focused capture can inspect NDP activity while reproducing a connectivity problem.
Wireshark Display Filters
All ICMPv6:
icmpv6Router Solicitation:
icmpv6.type == 133Router Advertisement:
icmpv6.type == 134Neighbor Solicitation:
icmpv6.type == 135Neighbor Advertisement:
icmpv6.type == 136Redirect:
icmpv6.type == 137Troubleshooting — Neighbor Remains INCOMPLETE
Example:
2001:db8:10::25 dev ens18 INCOMPLETEPossible causes include:
- Target host is offline
- Wrong VLAN
- Incorrect prefix
- Multicast filtering
- Layer 2 problem
- NDP security control blocking traffic
Troubleshooting — Neighbor Changes to FAILED
2001:db8:10::25 dev ens18 FAILEDThis indicates that the host could not successfully resolve or confirm the neighbor.
Check:
- Interface state
- VLAN
- IPv6 prefix
- Packet capture
- Switch security policy
- Target availability
Troubleshooting — No Default Router
Check:
ip -6 route show defaultIf the network expects RA-learned routing and no default route appears, capture:
sudo tcpdump -nn -i ens18 'icmp6'Look specifically for:
- Router Solicitation
- Router Advertisement
Troubleshooting — Address Becomes DADFAILED
A duplicate-address event can prevent the IPv6 address from becoming usable.
Investigate:
- Manually duplicated static addresses
- Duplicate VM templates
- Incorrect automation
- Unexpected cloned interface configuration

Neighbor Discovery Security and Best Practices
Neighbor Discovery operates on the local IPv6 link and therefore requires protection on untrusted or enterprise access networks.
Hop Limit 255
Valid Neighbor Discovery messages use an IPv6 Hop Limit of:
255This is an important validation mechanism.
If an attacker sends an NDP packet through a router, the router decrements the Hop Limit.
The receiving host therefore will not see a value of 255.
This helps prevent remotely routed packets from being accepted as legitimate on-link Neighbor Discovery messages.
It does not protect against an attacker already connected to the same Layer 2 network.
Rogue Router Advertisements
A malicious host on the same LAN could attempt to send unauthorized Router Advertisements.
Potential effects include:
- Incorrect default router
- Traffic redirection
- Bogus prefixes
- Connectivity disruption
Enterprise switches can use:
RA Guard
to restrict Router Advertisements to trusted router-facing ports.
RA Guard Does Not Protect Every NDP Message
RA Guard focuses specifically on:
Router Advertisements
It does not automatically protect every:
- Neighbor Solicitation
- Neighbor Advertisement
- Redirect
Other first-hop security controls may be required.
Depending on the platform, these can include:
- Neighbor Discovery inspection
- IPv6 Source Guard
- Device tracking
- DHCPv6 Guard
Secure Neighbor Discovery
SEND — Secure Neighbor Discovery
adds cryptographic protection to Neighbor Discovery.
It uses mechanisms including:
- Cryptographically Generated Addresses
- Digital signatures
SEND is standardized, but actual deployment and platform support should be verified before relying on it.
Neighbor Discovery and Fragmentation
Modern IPv6 rules prohibit the normal NDP messages from being transmitted using the IPv6 Fragment Header.
This applies to messages including:
- RS
- RA
- NS
- NA
- Redirect
Nodes are expected to ignore these NDP messages when carried using IPv6 fragmentation.
This improves security and makes first-hop filtering more reliable.
Do Not Block ICMPv6
NDP is carried through ICMPv6.
A firewall policy that simply blocks:
all ICMPv6
can break:
- Router Discovery
- Neighbor Discovery
- SLAAC
- Duplicate Address Detection
- Path MTU Discovery
- Normal IPv6 error reporting
Use IPv6-aware firewall policy instead of treating ICMPv6 as unnecessary traffic.
Key Takeaways and Summary
Key Takeaways
- IPv6 uses Neighbor Discovery instead of IPv4 ARP for link-layer address resolution.
- NDP is carried using ICMPv6 and provides more functionality than ARP alone.
- The five primary NDP messages are RS, RA, NS, NA and Redirect.
- Router Solicitations are normally sent to
ff02::2, the all-routers multicast address. - Router Advertisements commonly use a router’s link-local source address and can advertise prefixes and other network parameters.
- Hosts learn candidate default routers from Router Advertisements rather than from a traditional gateway field.
- Neighbor Solicitation uses solicited-node multicast for normal IPv6 address resolution.
- Neighbor Advertisement provides link-layer information and can confirm neighbor reachability.
- For remote destinations, the host resolves the next-hop router rather than the remote destination’s MAC address.
- Duplicate Address Detection uses NS and NA to determine whether a tentative IPv6 address is already in use.
- Neighbor Unreachability Detection continuously helps determine whether cached neighbors remain reachable.
- NDP is security-sensitive local-link traffic and should be protected without broadly blocking ICMPv6.
Summary
IPv6 Neighbor Discovery is a fundamental part of IPv6 networking.
It replaces several functions that IPv4 handles through separate protocols and mechanisms.
NDP provides:
- Router discovery
- Prefix discovery
- Address resolution
- Neighbor reachability detection
- Duplicate Address Detection
- Redirect processing
For local address resolution, the sender first determines whether the destination is on-link.
If it is on-link, the sender discovers the target’s link-layer address using:
Neighbor Solicitation and Neighbor Advertisement
If the destination is remote, the sender instead resolves the link-layer address of the selected:
next-hop router
Router discovery uses:
- Router Solicitation
- Router Advertisement
while Duplicate Address Detection ensures that an IPv6 address is not already in use before it becomes fully usable.
During troubleshooting, the most useful commands are:
ip -6 addr showip -6 route showip -6 route get ip -6 neigh showsudo tcpdump -nn -i icmp6The most important troubleshooting principle is:
Identify the next hop first.
Then determine whether NDP successfully resolved and maintained that neighbor.
This makes Neighbor Discovery troubleshooting much more systematic than simply assuming an IPv6 routing problem.
Useful Links and References
SanchitGurukul Static Resources
Official External References
Your feedback matters
Was this post helpful?
Discussion
0 approved comments
No approved comments yet. You can start the discussion below.
Leave a Comment
No login is required. Name and email are used for moderation/security. Your email is never displayed publicly. All comments require administrator approval.
Discover more from SanchitGurukul
Subscribe to get the latest posts sent to your email.


